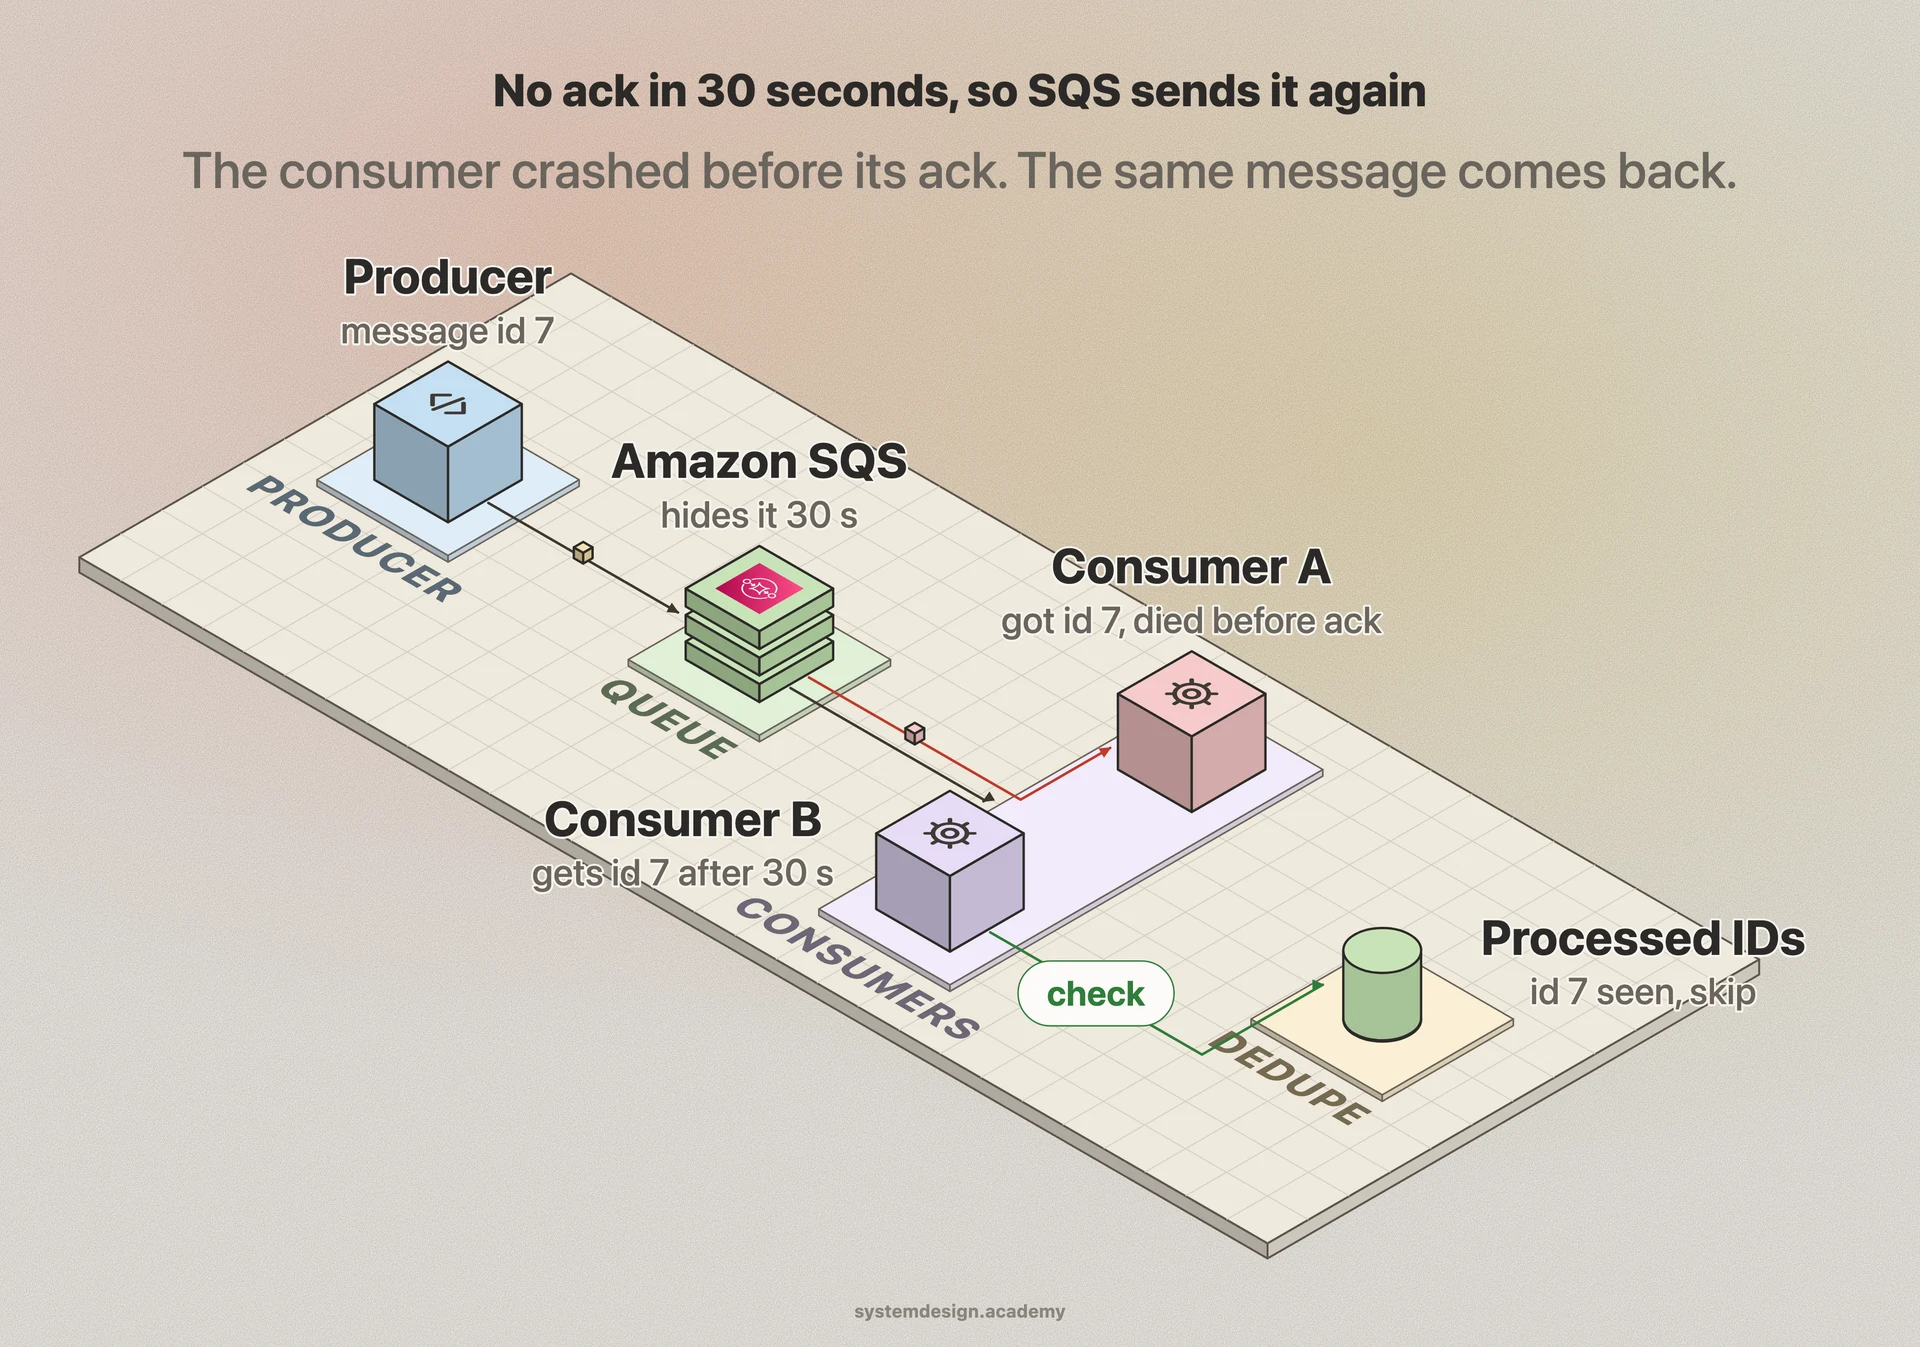
The mechanism is an acknowledgment plus a redelivery timer. When a consumer pulls a message, the broker marks it as in-flight and starts a clock (in Amazon SQS this is the visibility timeout, default 30 seconds). The message is hidden from other consumers during that window.
If the consumer sends an ack before the timer expires, the broker deletes the message and moves on. If the consumer crashes, times out, or the ack is lost on the network, the timer fires, the message becomes visible again, and another consumer picks it up. Kafka does the equivalent with consumer offset commits: the message is reprocessed if the offset was not committed before a rebalance or crash.
Duplicates also come from the producer side. A producer sends a message, the broker stores it, but the broker's success response is lost in transit. The producer assumes failure and resends, so now two copies exist. This is why at-least-once duplication can happen even when every consumer behaves perfectly.
The standard defense is idempotency on the consumer. You attach a unique message ID or business key, record processed IDs in a database or cache, and skip anything you have already seen. Operations that are naturally idempotent, like setting a value rather than incrementing it, need no extra bookkeeping at all.