Login systems set an allowed amount of skew. Kerberos, the login protocol behind Windows domains, rejects a message when the clocks differ by more than its clockskew setting. In MIT Kerberos that limit defaults to 300 seconds, or five minutes. A server whose clock drifts past it starts failing logins with no other fault in sight.
Tokens carry time too. A JWT has an exp claim (expires at) and an nbf claim (not valid before). The JWT standard, RFC 7519, says implementers may allow a small leeway, usually no more than a few minutes, to account for clock skew. Without it, a token issued on one server can look not-yet-valid on another whose clock runs a little behind.
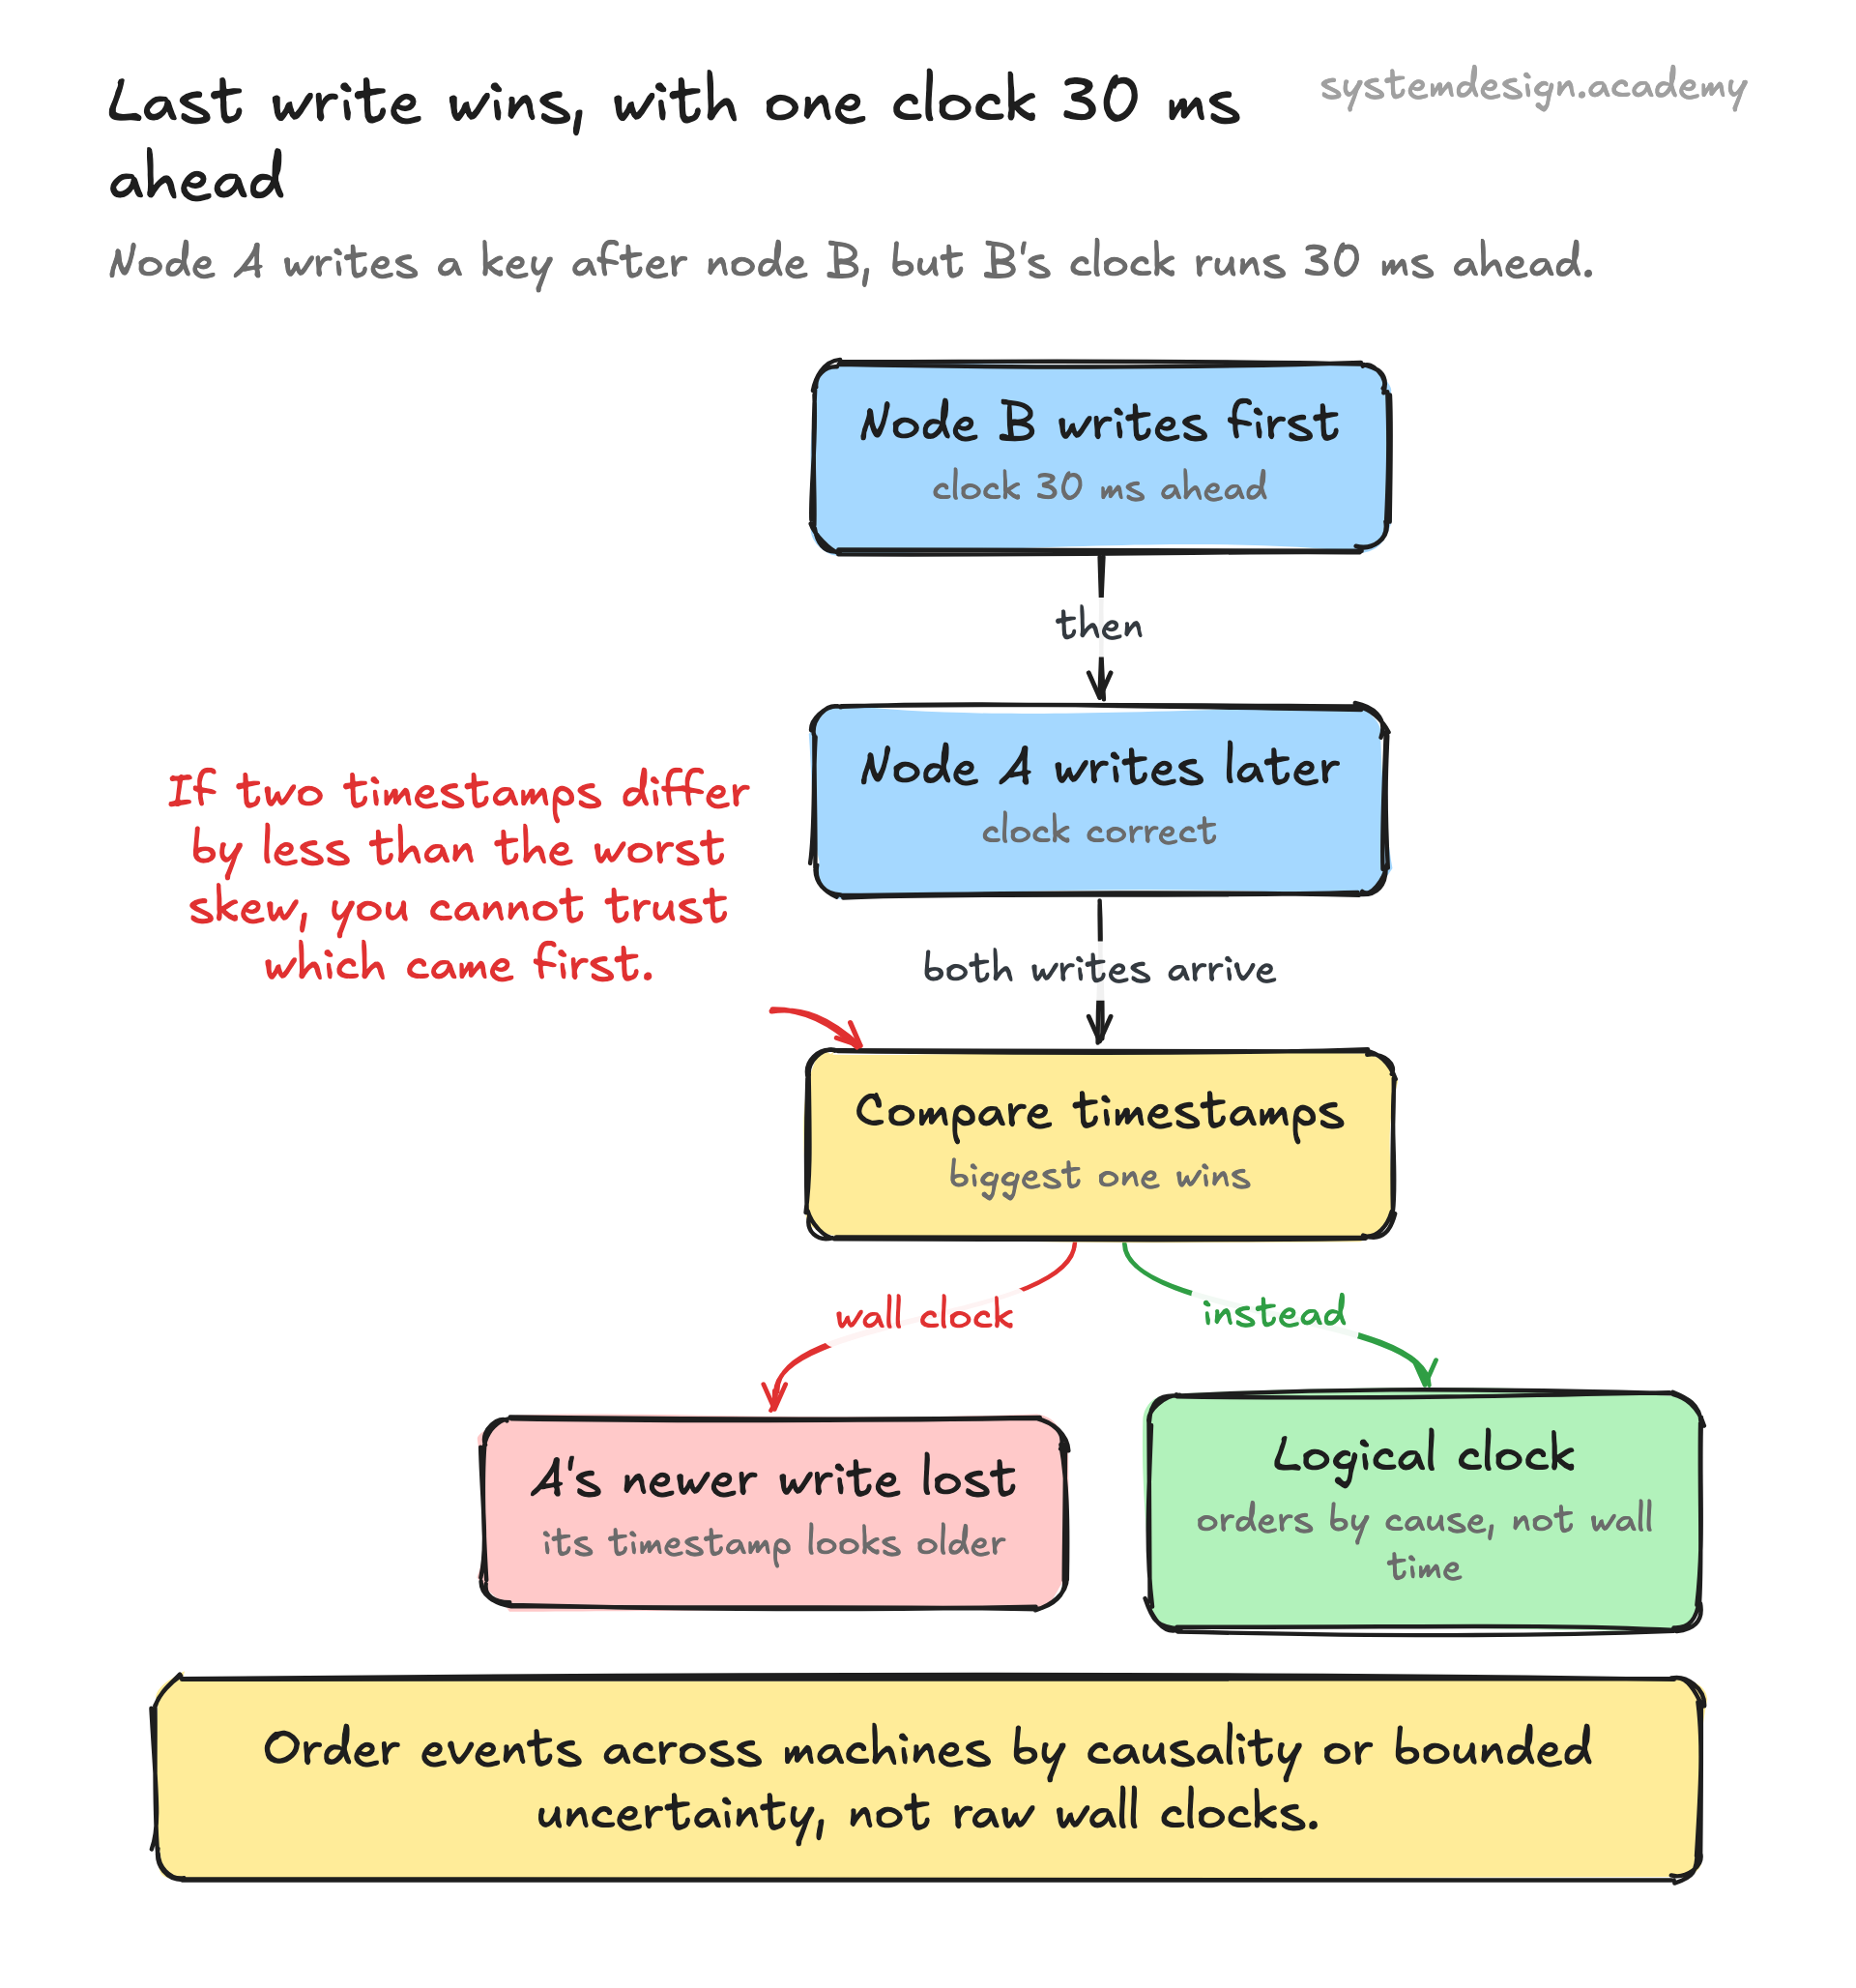
Databases that rely on time often enforce a hard limit. CockroachDB assumes node clocks stay within a maximum offset, 500 milliseconds by default. When a node finds its clock is out of sync with at least half the other nodes by 80 percent of that limit, it shuts itself down. gRPC avoids the problem for deadlines by sending the remaining time, with elapsed time already taken off, so skewed clocks do not shift the deadline. A distributed job scheduler has to handle skew when deciding which jobs are due, and Lamport timestamps give an order that needs no clock at all.
One note on the name: in chip and circuit design, clock skew means something different. There it is the difference in when one clock signal reaches different parts of a circuit. This page is about the distributed-systems meaning, the gap between two computers' clocks.