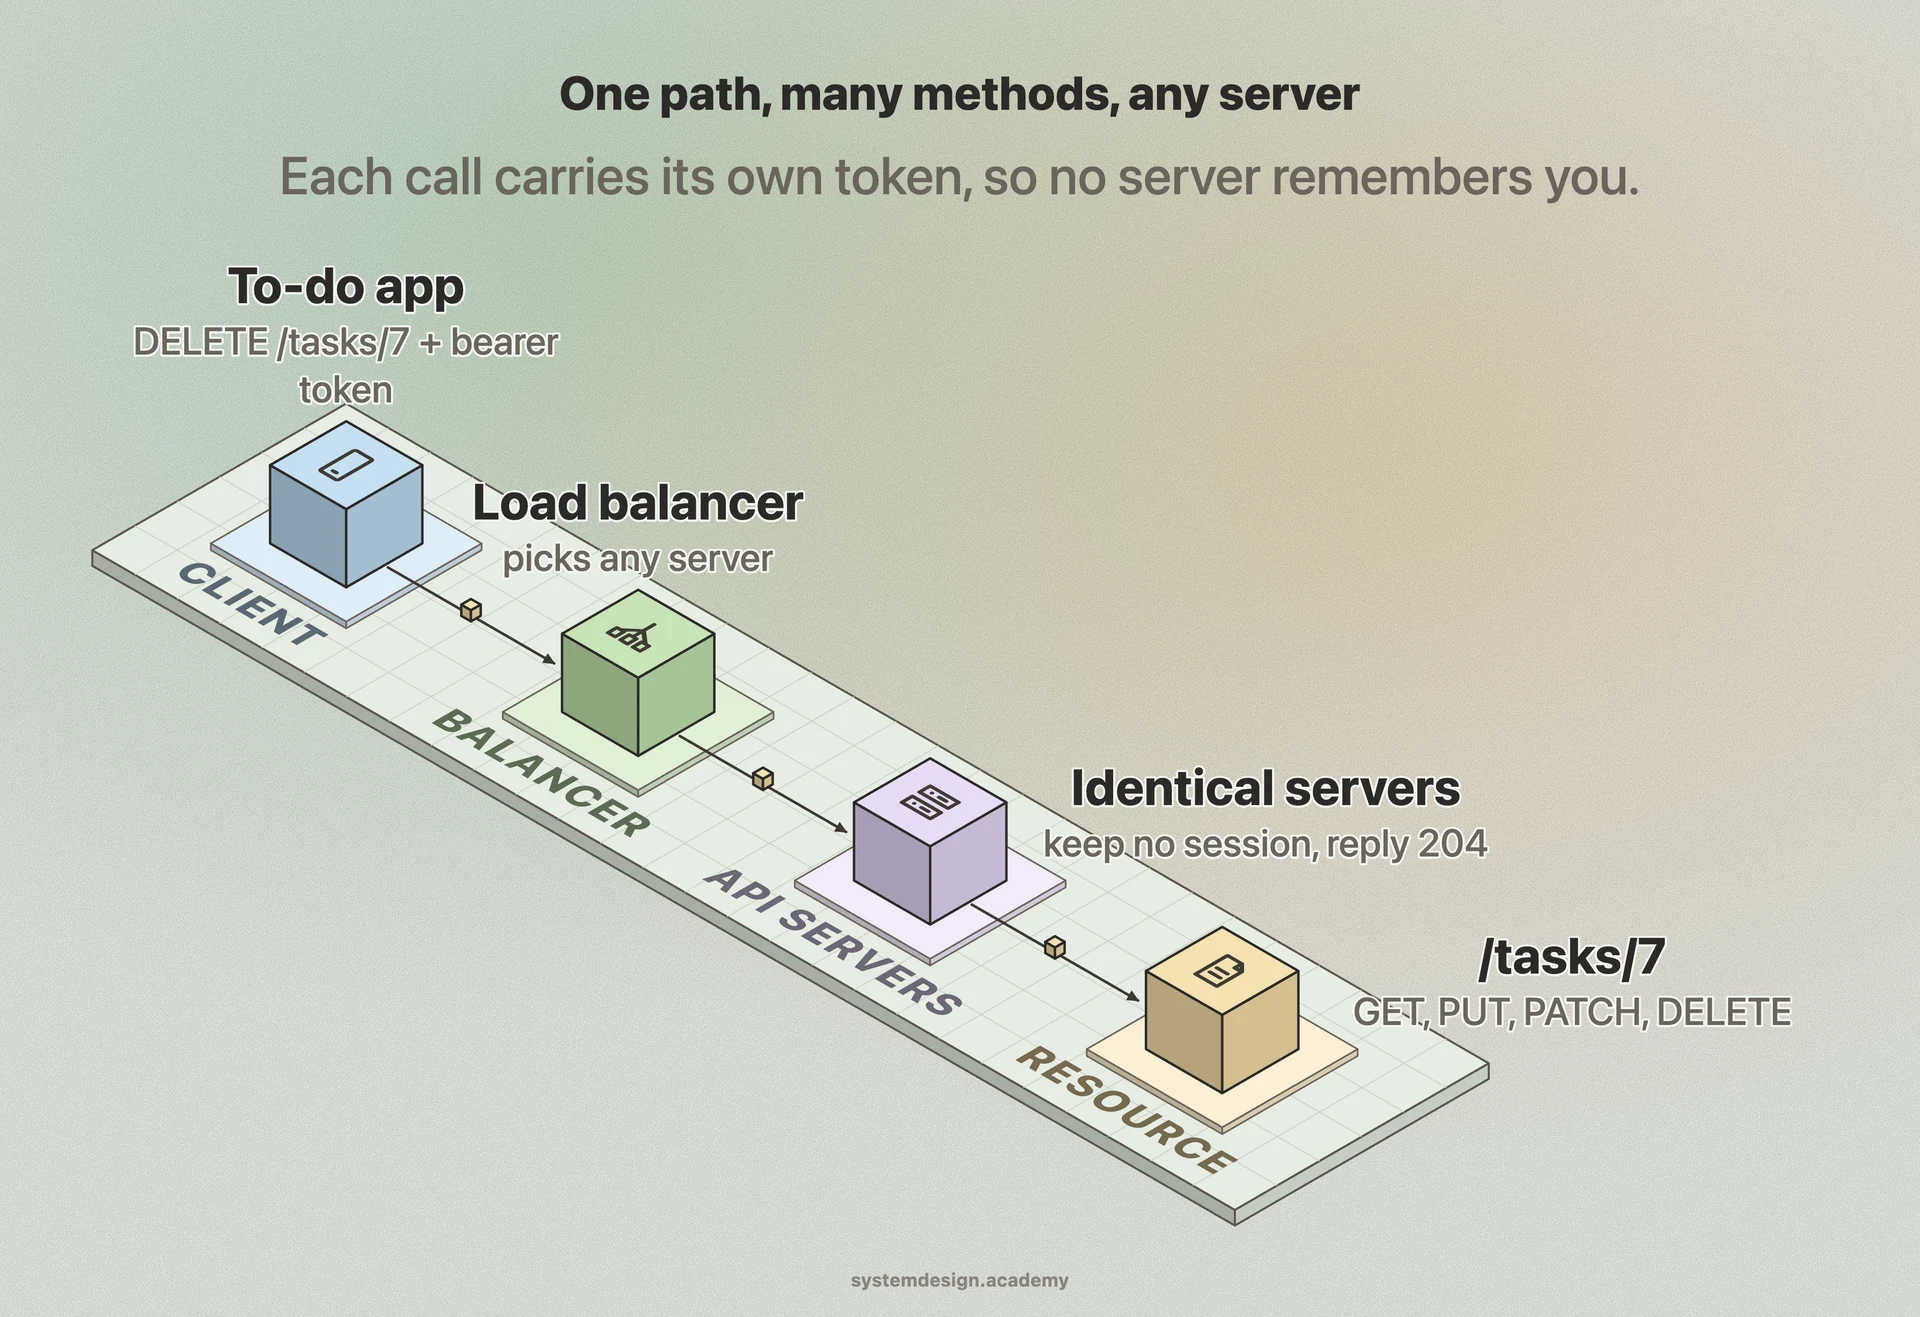
A REST call is just an HTTP request. The method (verb) says what to do, the path says which resource, headers carry metadata like Content-Type and Authorization, and the body carries data for writes. The server replies with a status code, response headers, and usually a JSON body.
Status codes carry real meaning and clients are expected to read them: 200 OK for a successful read, 201 Created after a POST that made something new, 204 No Content for a successful delete, 400 for a bad request, 401 when you are not authenticated, 403 when you are not allowed, 404 when the resource does not exist, and 500 when the server broke.
REST is stateless. The server keeps no memory of previous requests, so every call must include its own authentication token and any context it needs. This is what lets you run hundreds of identical API servers behind a load balancer: any server can handle any request because none of them hold session state. Several HTTP methods are also idempotent by design, meaning GET, PUT, and DELETE produce the same end result whether you call them once or five times, which makes safe retries possible.
Good REST APIs lean on HTTP features instead of reinventing them: caching through ETag and Cache-Control headers, content negotiation through the Accept header, and partial reads through query parameters like /users?role=admin&limit=50.