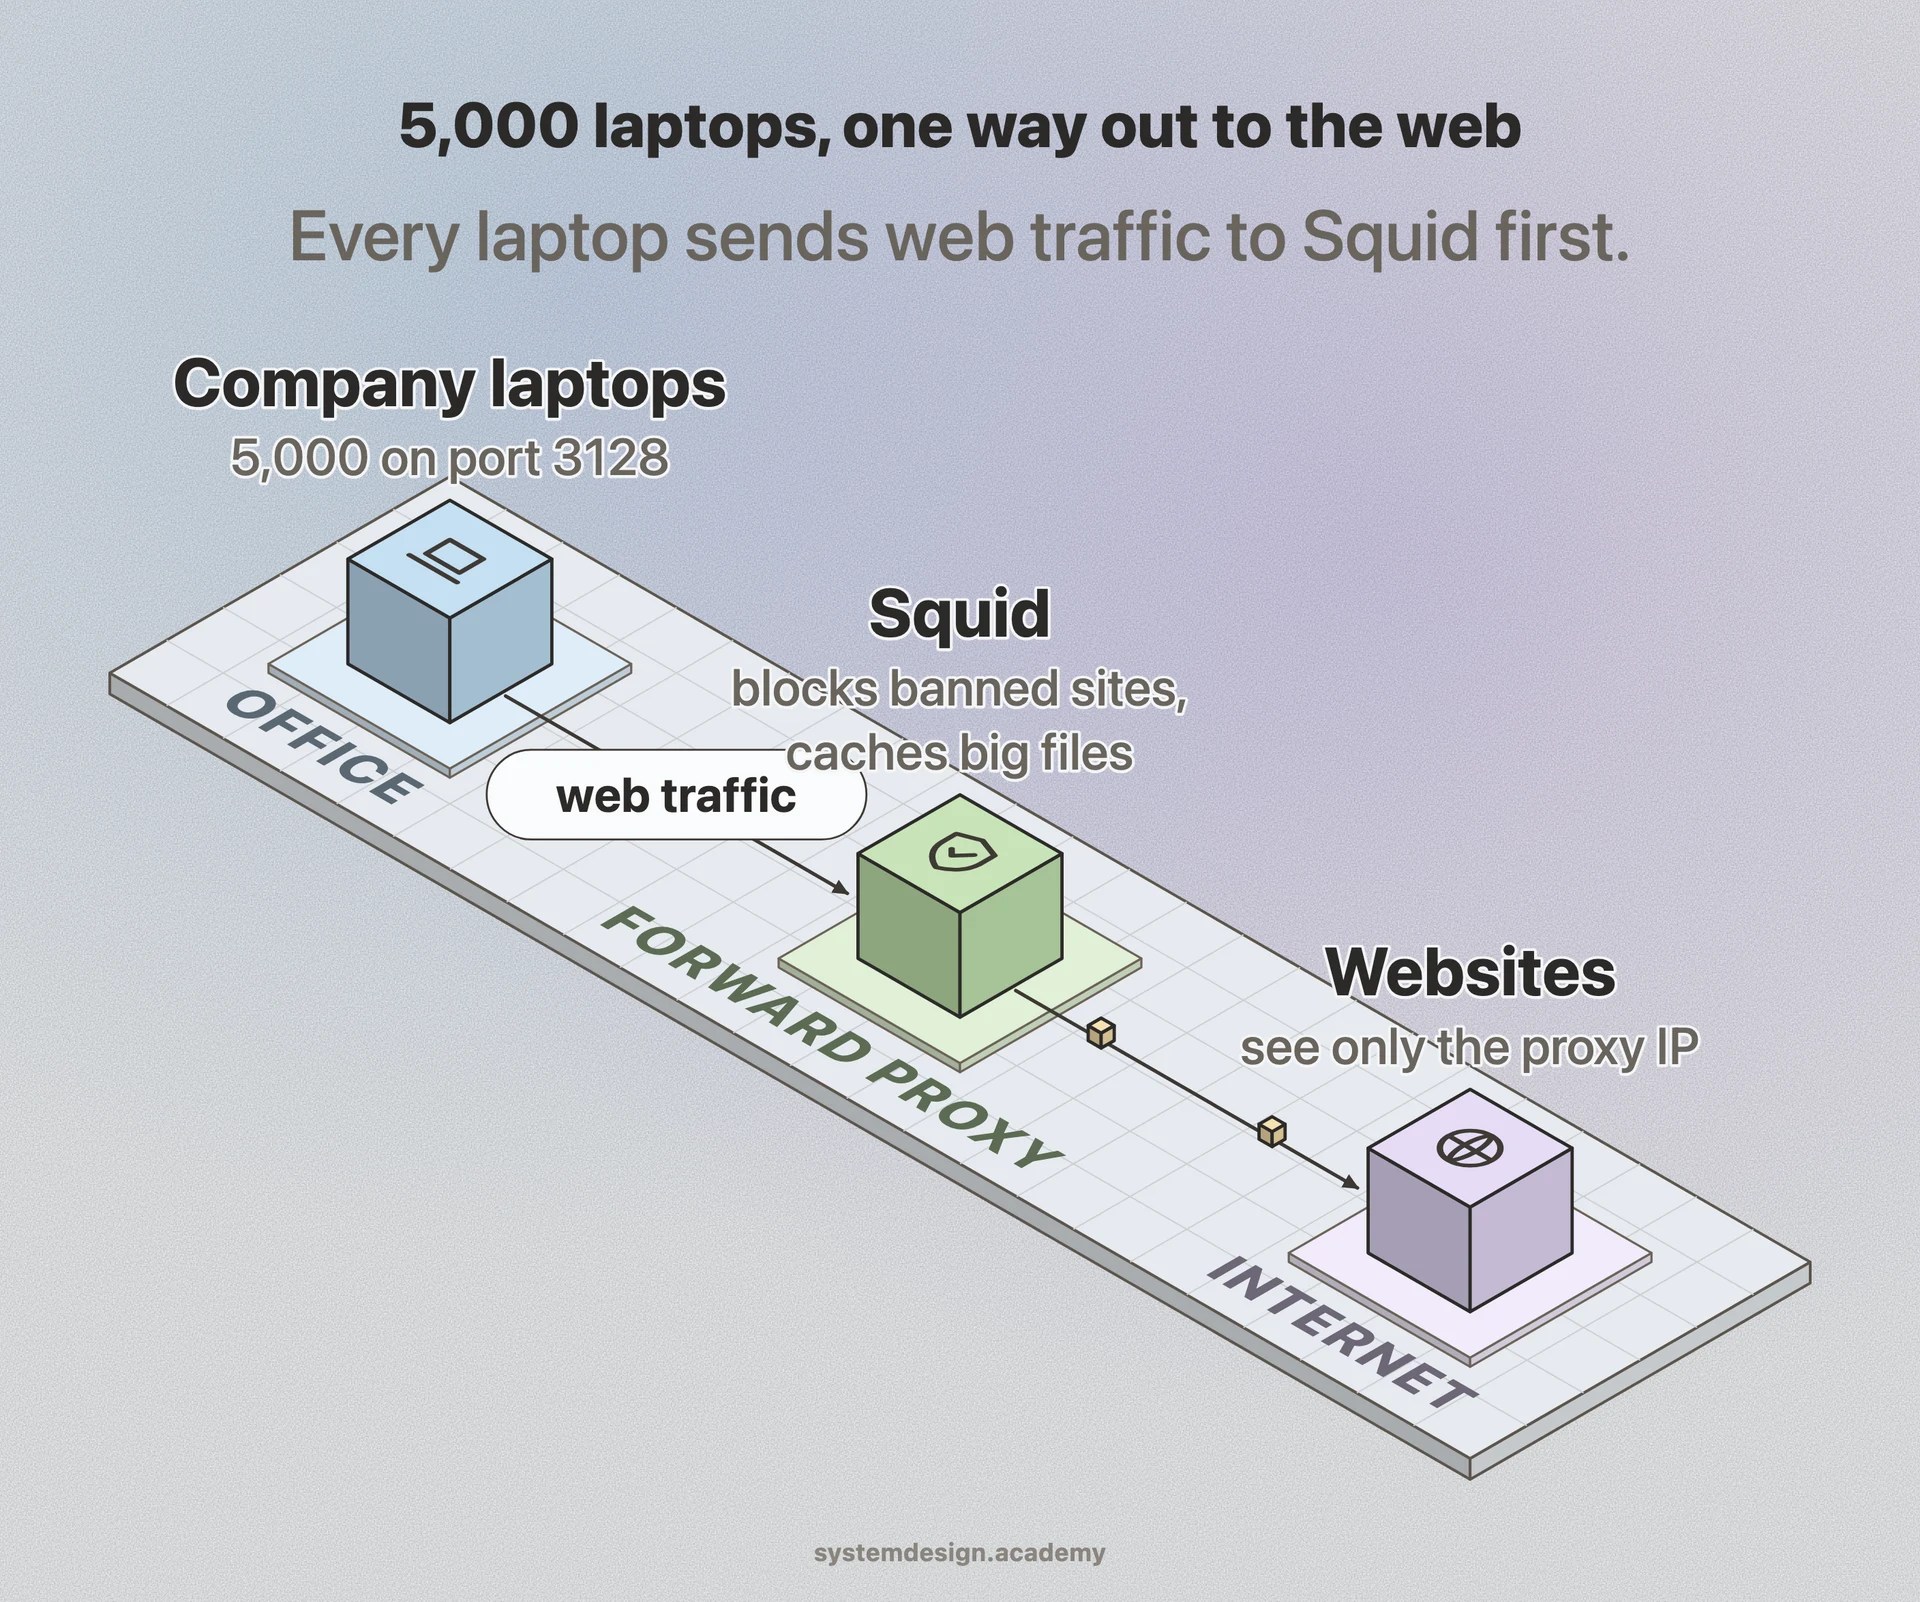
For plain HTTP, the client sends the full request to the proxy, the proxy reads the destination from the request line or Host header, opens its own connection to that server, fetches the response, and relays it back. The proxy can read, log, cache, or rewrite the request because the traffic is in the clear.
For HTTPS, the proxy cannot read the encrypted payload by default. The client sends a CONNECT request naming the target host and port, and the proxy opens a raw TCP tunnel and blindly pipes encrypted bytes in both directions. If an organization wants to inspect HTTPS, it runs a man-in-the-middle proxy that terminates TLS, decrypts, inspects, then re-encrypts, which requires installing the proxy's root certificate on every client.
A common extra job is caching. If two users request the same large file, the proxy can serve the second request from its local store instead of going out to the internet again. Squid, one of the oldest forward proxies, was built largely for this in the days of expensive bandwidth.