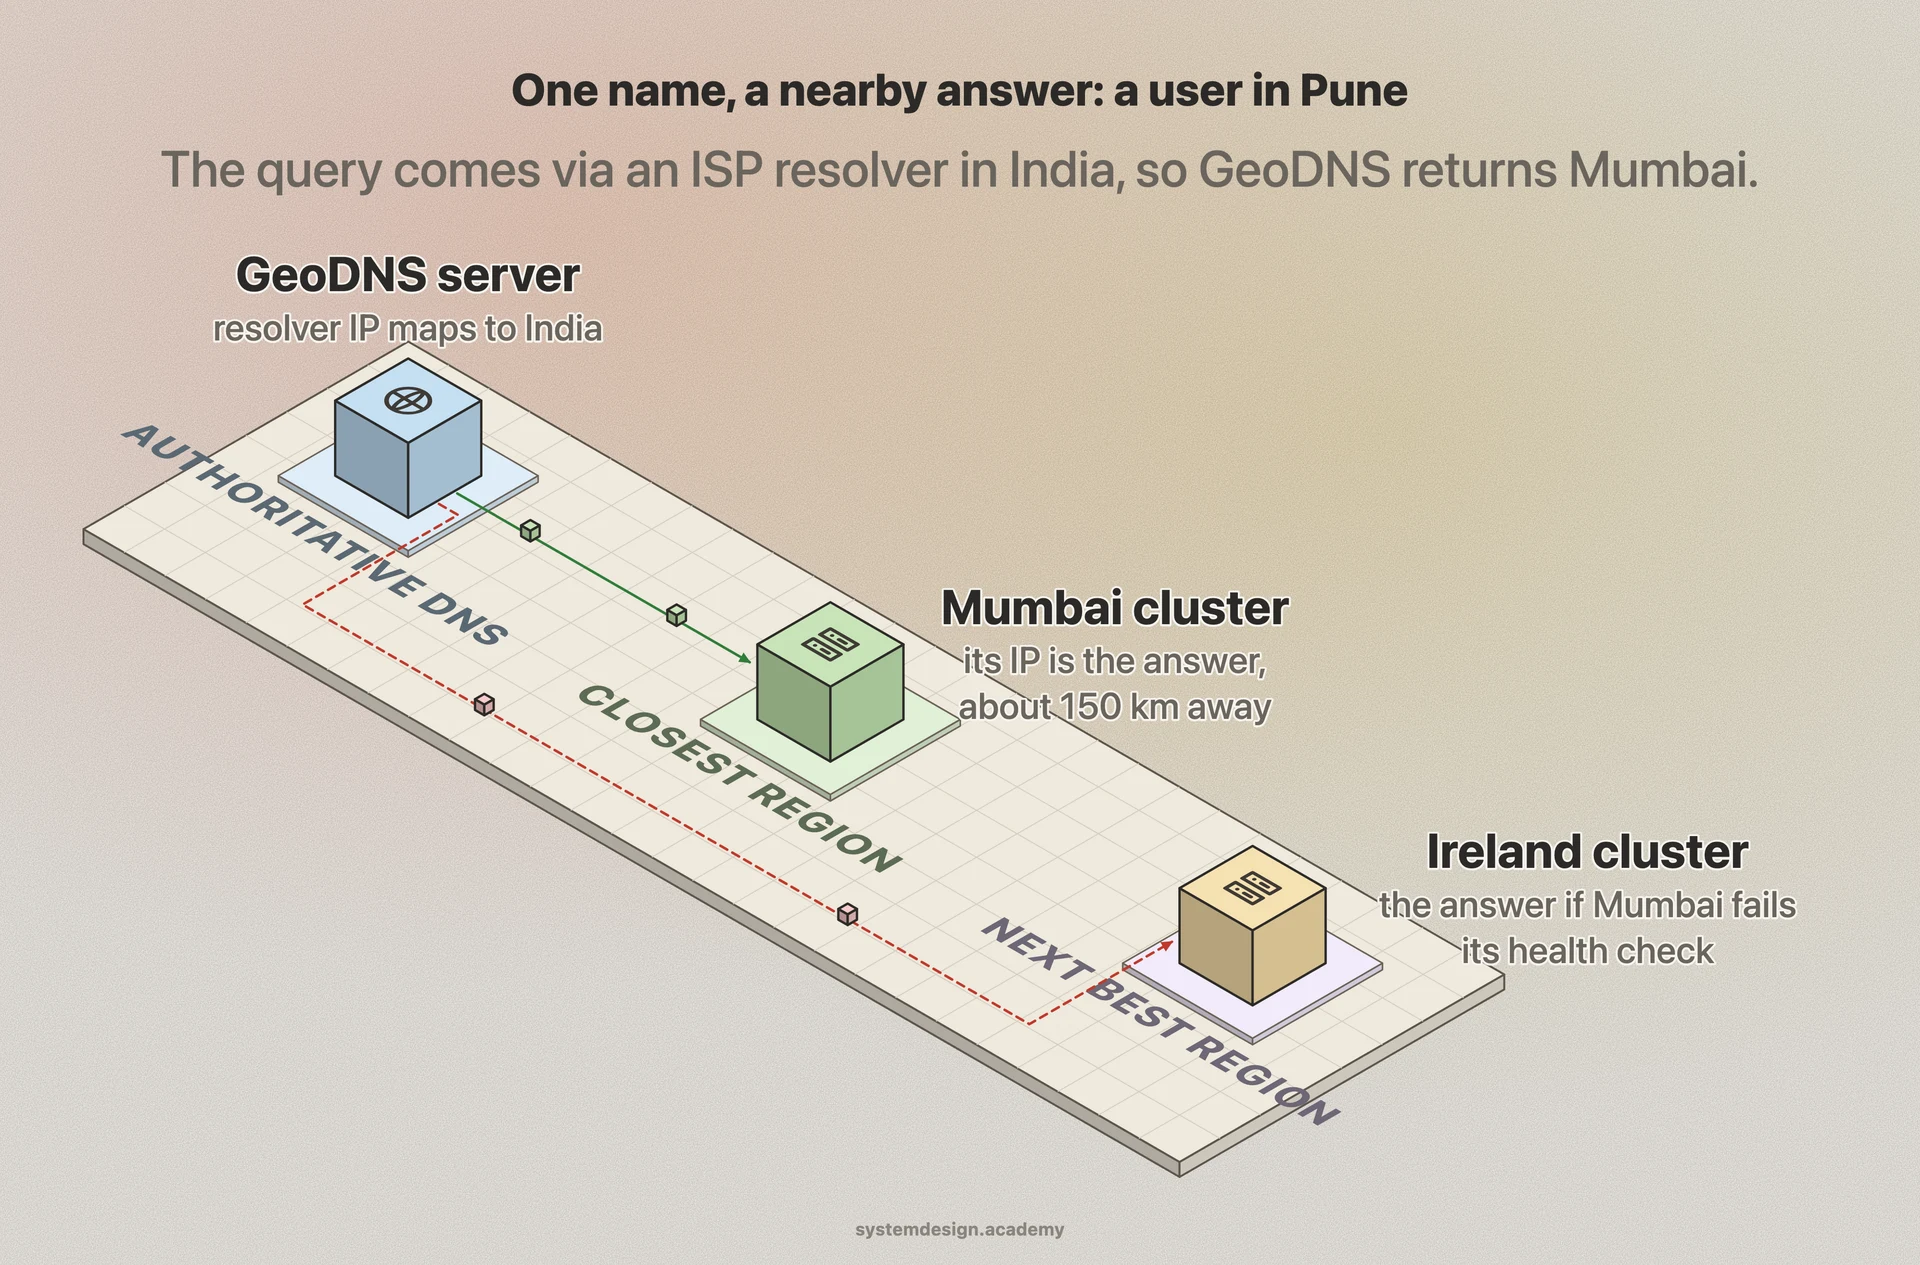
The key input is the client IP seen by the authoritative server. In most cases that is the IP of the user's recursive resolver (for example their ISP or a public resolver like 8.8.8.8), not the user's own device. The DNS server matches that IP against a geolocation database such as MaxMind GeoIP2 to guess a location, then picks the closest configured pool of records.
Because the resolver IP is used, accuracy depends on the user querying a nearby resolver. If someone in India uses a resolver hosted in the US, GeoDNS may route them to a US server. The EDNS Client Subnet extension (ECS, RFC 7871) fixes much of this by letting the resolver forward a truncated version of the real client subnet, so the authoritative server sees roughly where the user is.
TTL matters a lot. A short TTL such as 30 to 60 seconds lets you reroute users quickly during a regional outage, but it increases DNS query volume. A long TTL means clients cache the regional IP for hours and ignore later geo decisions until the cache expires.
Many GeoDNS systems also fold in health checks. If the closest region is failing its health check, the authoritative DNS server returns the next-best region instead, which turns GeoDNS into a basic global failover mechanism rather than pure proximity routing.