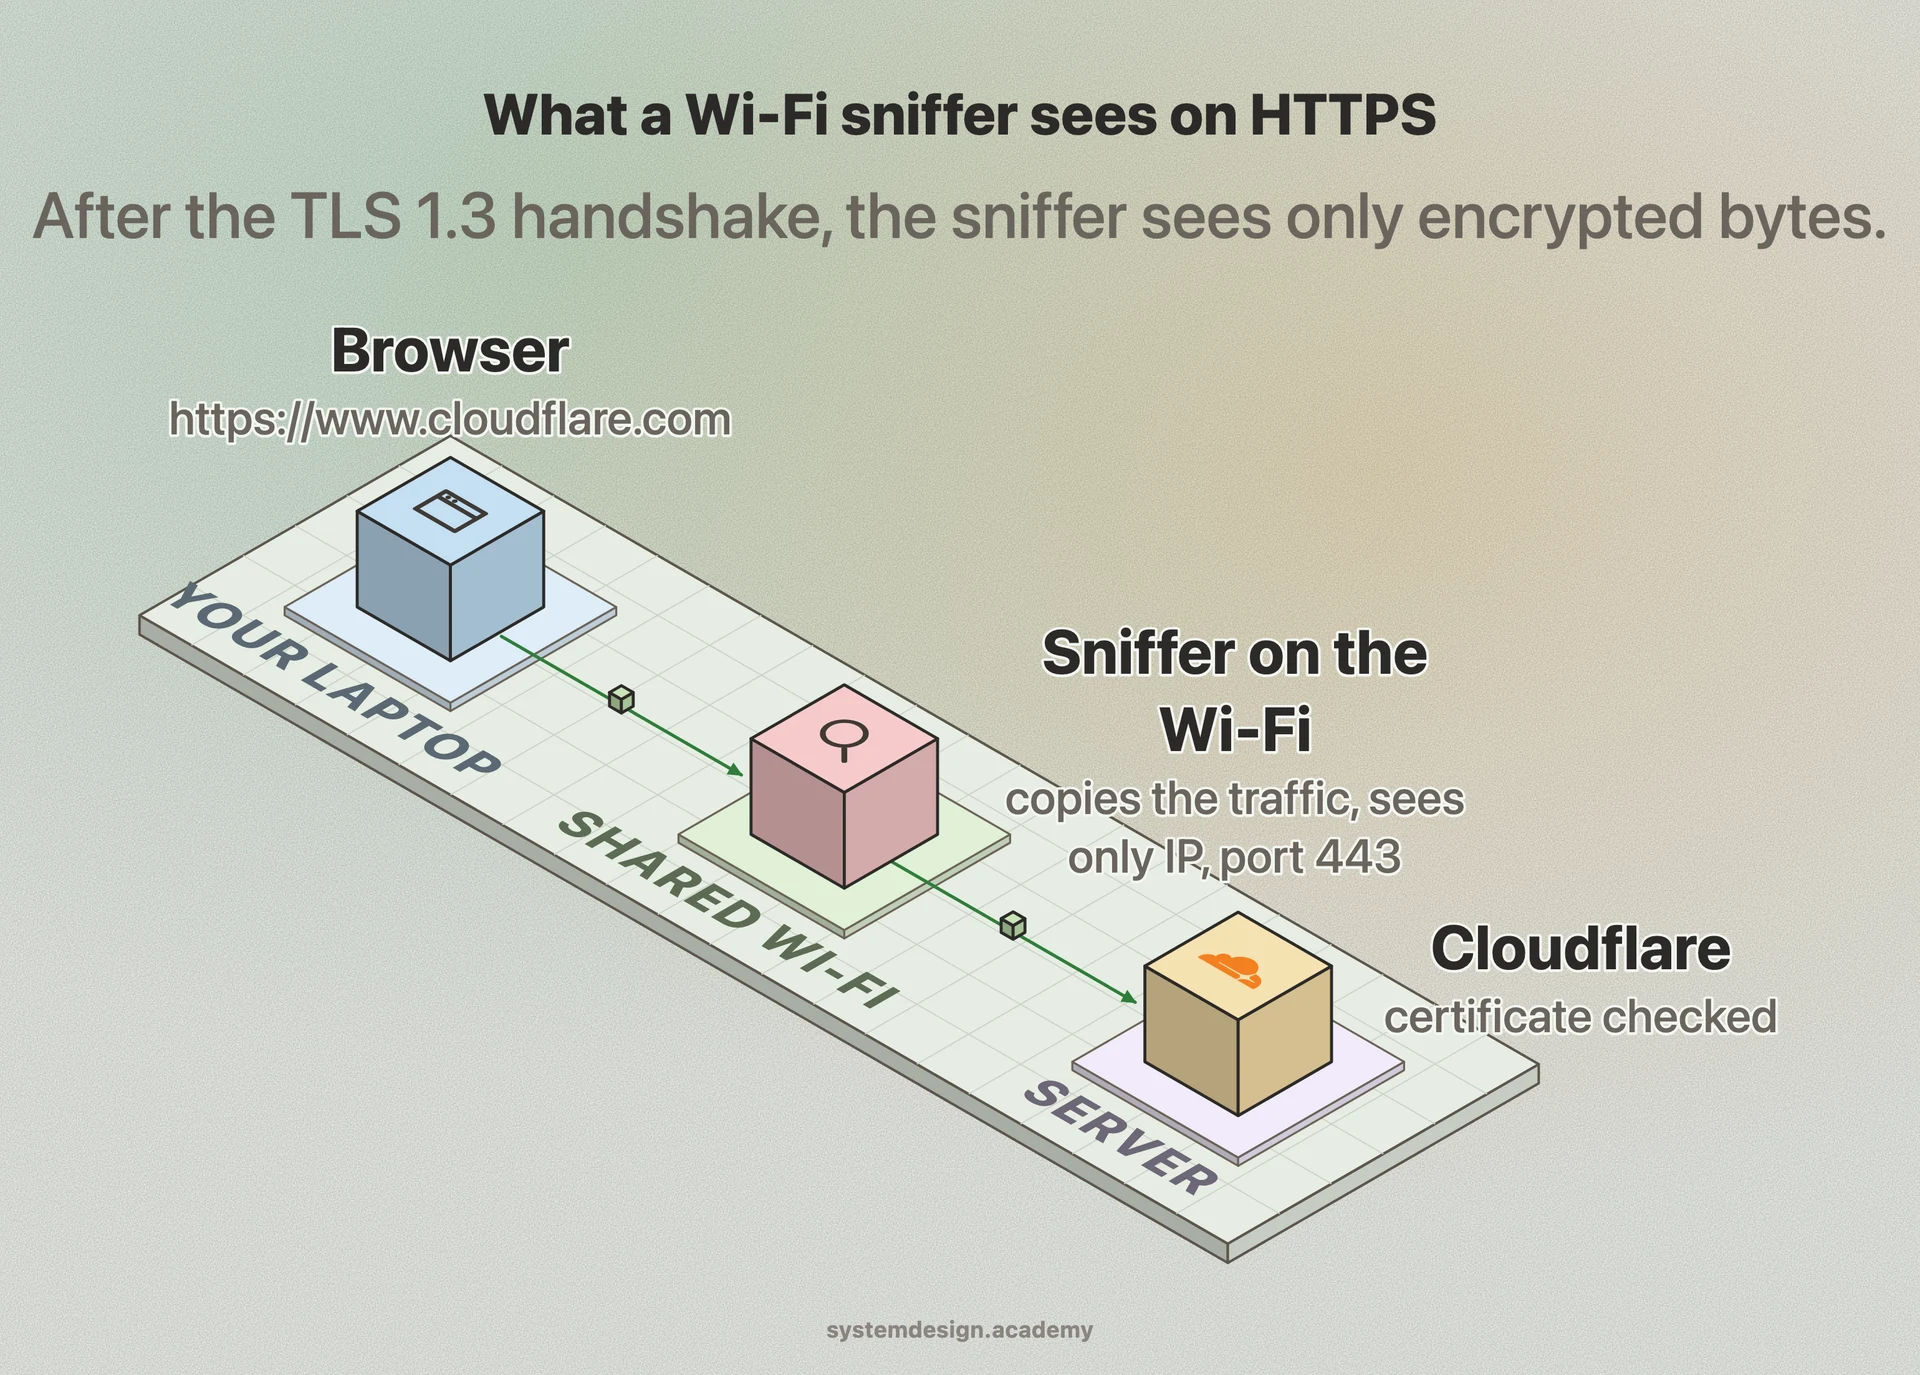
The answer today is always. Every production site should serve HTTPS only and redirect HTTP to it. Chrome and Firefox label plain HTTP pages as Not Secure, browser features like service workers, HTTP/2, geolocation, and the camera API refuse to run without it, and Google uses HTTPS as a ranking signal. There is no real case for serving public traffic over HTTP anymore.
The cost is small but real. There is the one-time handshake overhead per connection, certificate management, and the discipline of renewing certificates before they expire. Let's Encrypt made certificates free and automatable, and tools like Certbot or the cert handling built into nginx, Caddy, and cloud load balancers renew them on a schedule, so a forgotten renewal causing an outage is the main risk to watch.
One limit worth knowing: HTTPS encrypts the request path, headers, and body, but the server's IP address and the destination hostname in the older SNI field are still visible to network observers. Encrypted Client Hello is the newer fix that hides the hostname too, but it is not yet universal.