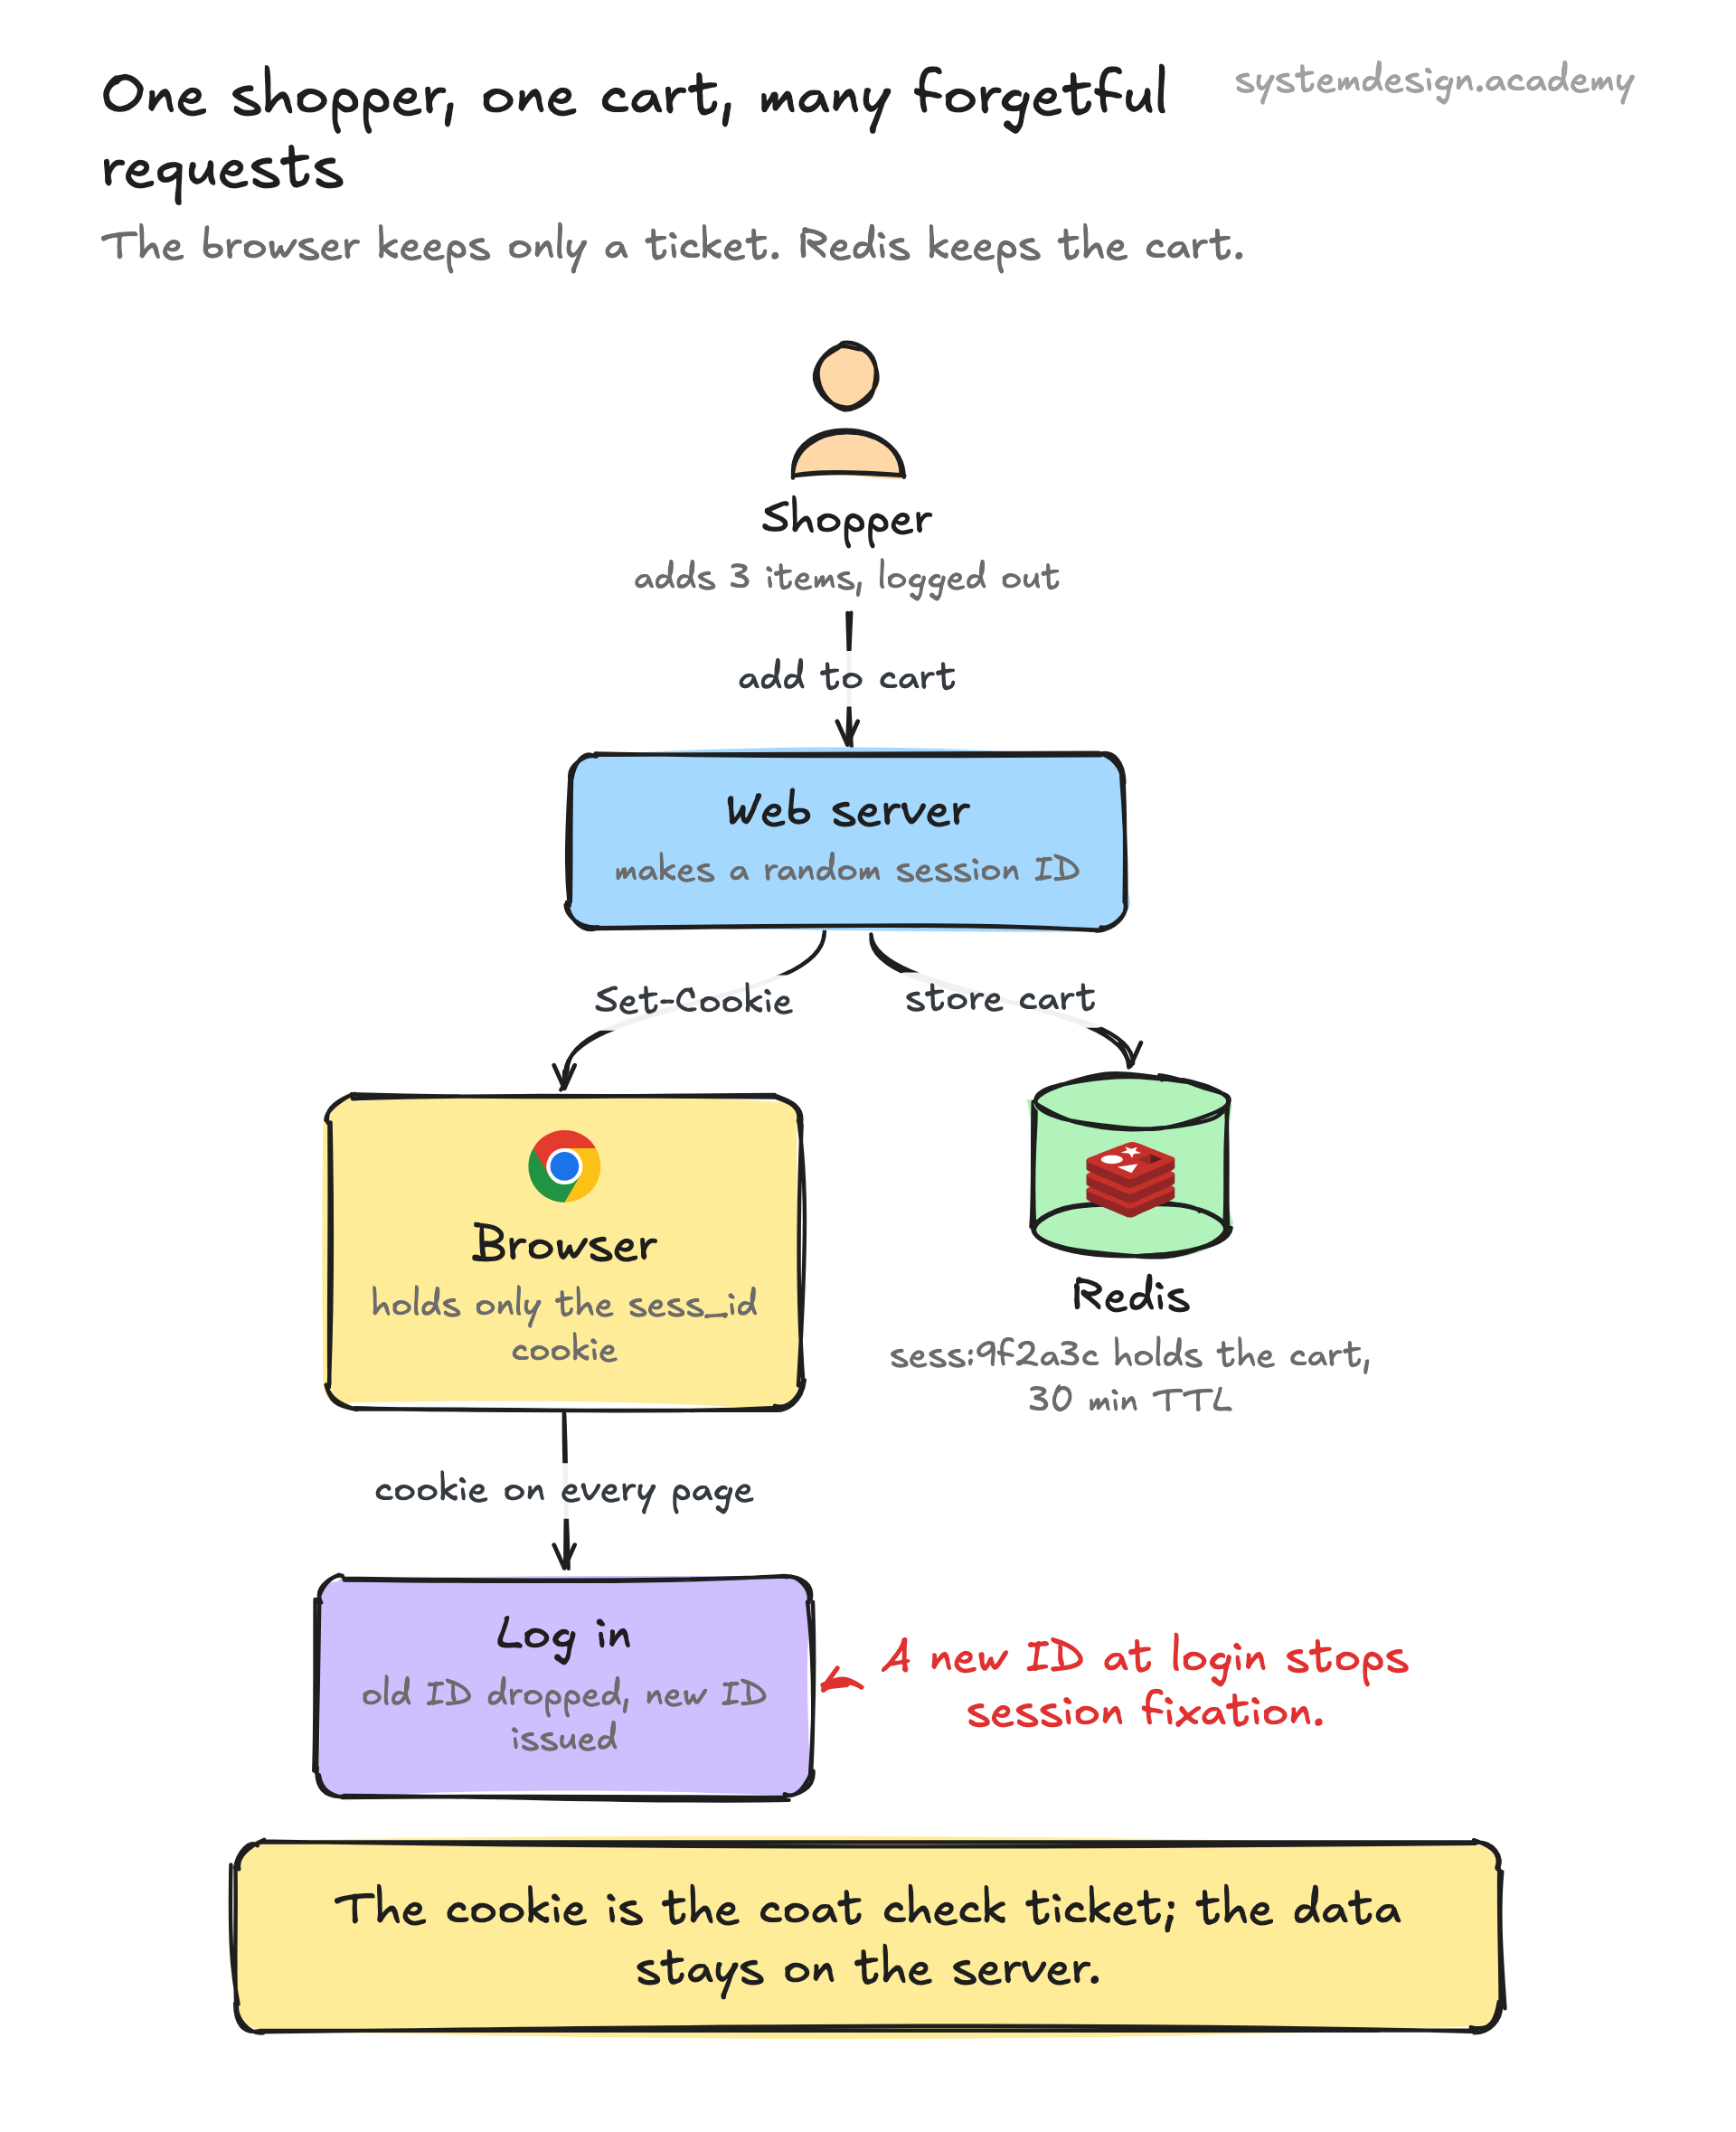
HTTP is stateless. Each request stands alone, and the server treats the second request from you exactly like the first, with no memory that you logged in five seconds ago. A session is the workaround. It is a bundle of data the server keeps about one user, identified by a single random string called the session ID.
Think of a coat check at a theater. You hand over your coat, you get a numbered ticket, and the theater keeps the coat. The ticket is small and means nothing on its own, but it lets the theater find your coat later. The session ID is the ticket; the actual data (user ID, cart contents, permissions) is the coat, sitting on the server.
The browser carries the ticket automatically. On login the server generates a session ID like 9f2a3c..., stores the real data against that key, and sends the ID back in a Set-Cookie header. The browser then attaches that cookie to every following request to the same site, so the server can look up who you are without asking you to log in again.