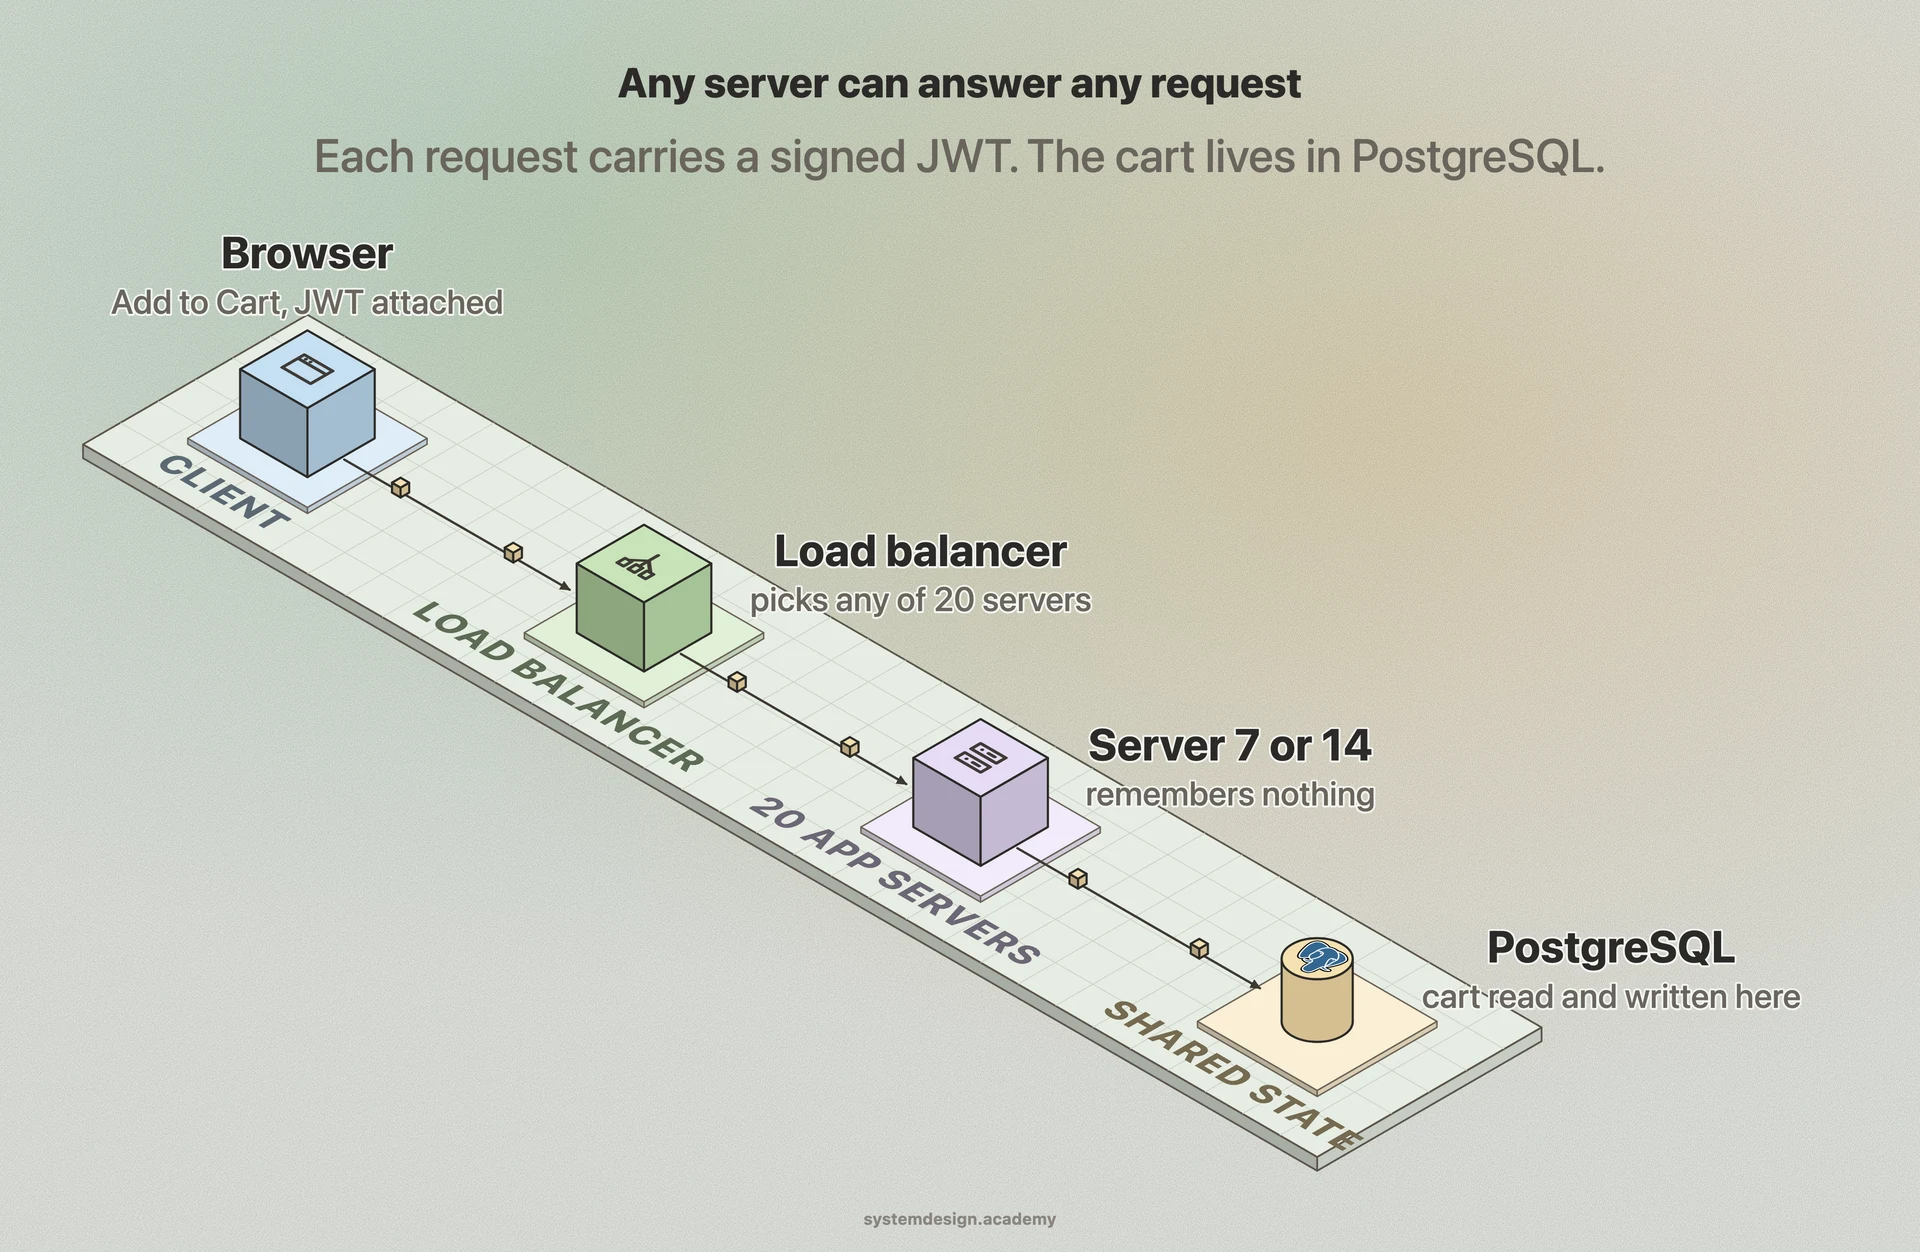
HTTP was designed to be stateless from the start. A browser opens a connection, sends GET /products, gets a response, and the server is free to forget the whole exchange. To layer identity on top of that, the request includes something self-contained. A common choice is a JSON Web Token (JWT): a signed blob the client stores and sends in the Authorization header on every request. The server verifies the signature and reads the user ID straight out of the token, no lookup of server memory required.
Because no server holds private session data, a load balancer can send your requests to any of 50 identical app servers and each one can answer correctly. This is why stateless services pair so well with horizontal scaling and auto-scaling groups. You can spin up a new instance, route traffic to it instantly, kill it later, and nobody loses their session.
The cost is moved elsewhere. Shared state goes to a database or a cache that all servers can reach, and that store becomes the thing you must scale and protect. With JWTs, you also accept larger requests (the token travels every time) and the headache of revoking a token before it expires, since the server is not tracking it.