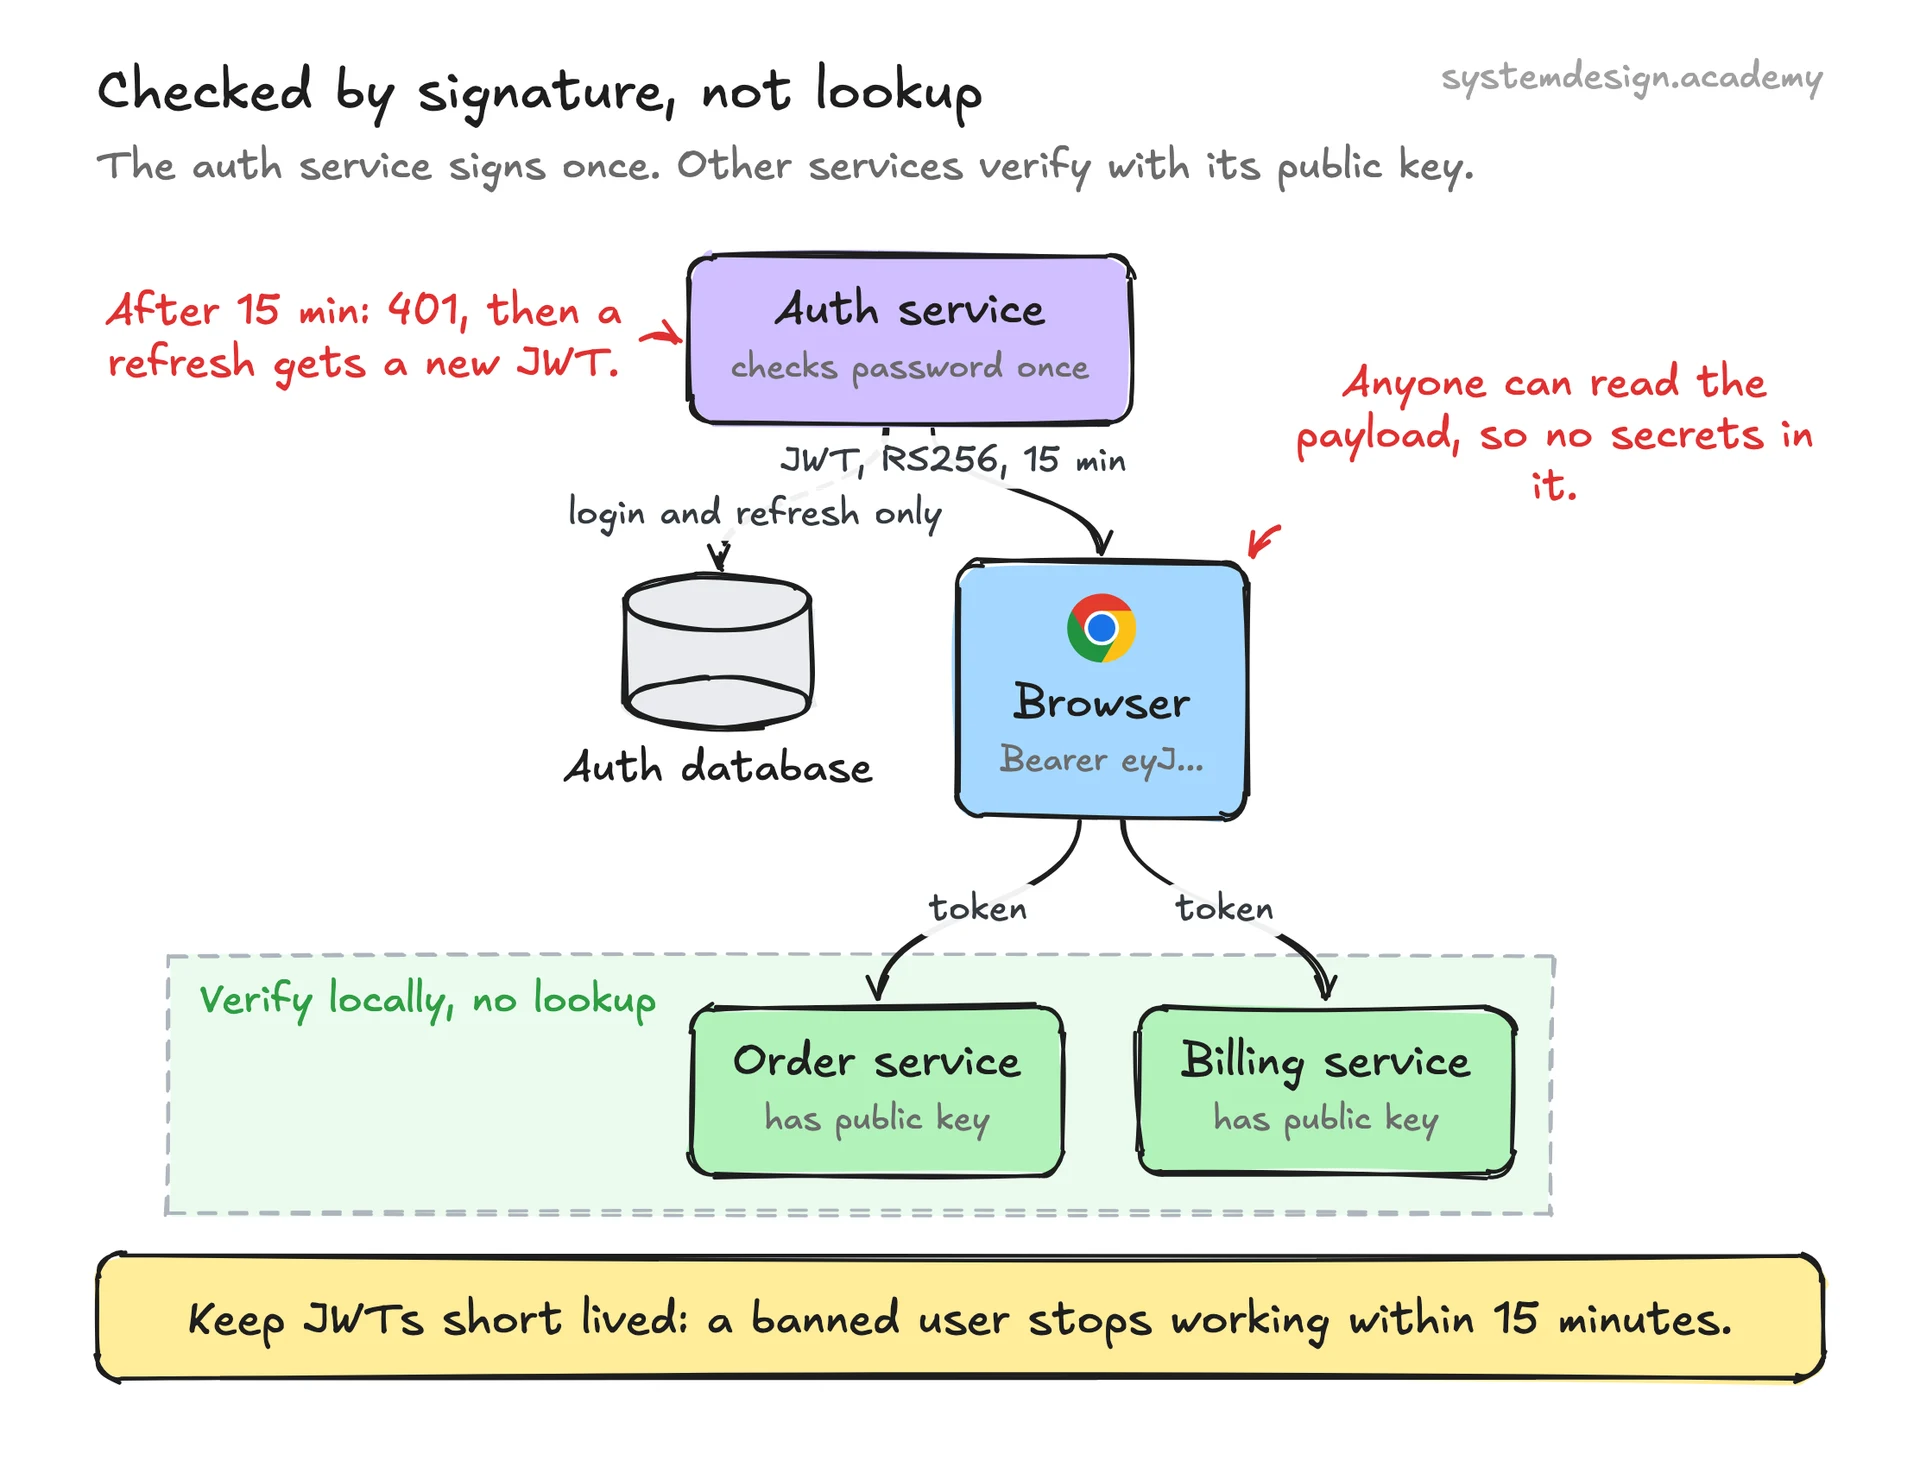
Say a user logs in to an API. The auth service checks the password once, then issues a JWT with sub set to the user ID, role set to admin, and exp set to 15 minutes from now, signed with RS256. The browser stores it and sends it on each request as Authorization: Bearer eyJ...
An order service and a billing service, running on different machines, each hold only the auth service public key. When a request arrives, each one verifies the signature locally, reads role admin from the payload, and decides whether to allow the action. Neither service ever talks to the auth database to authenticate the call.
Fifteen minutes later the token expires and requests start failing with 401. The browser quietly sends its refresh token to the auth service, which does check its database, confirms the user is still active, and mints a fresh 15-minute JWT. The user never notices, and a banned user stops working within at most 15 minutes.