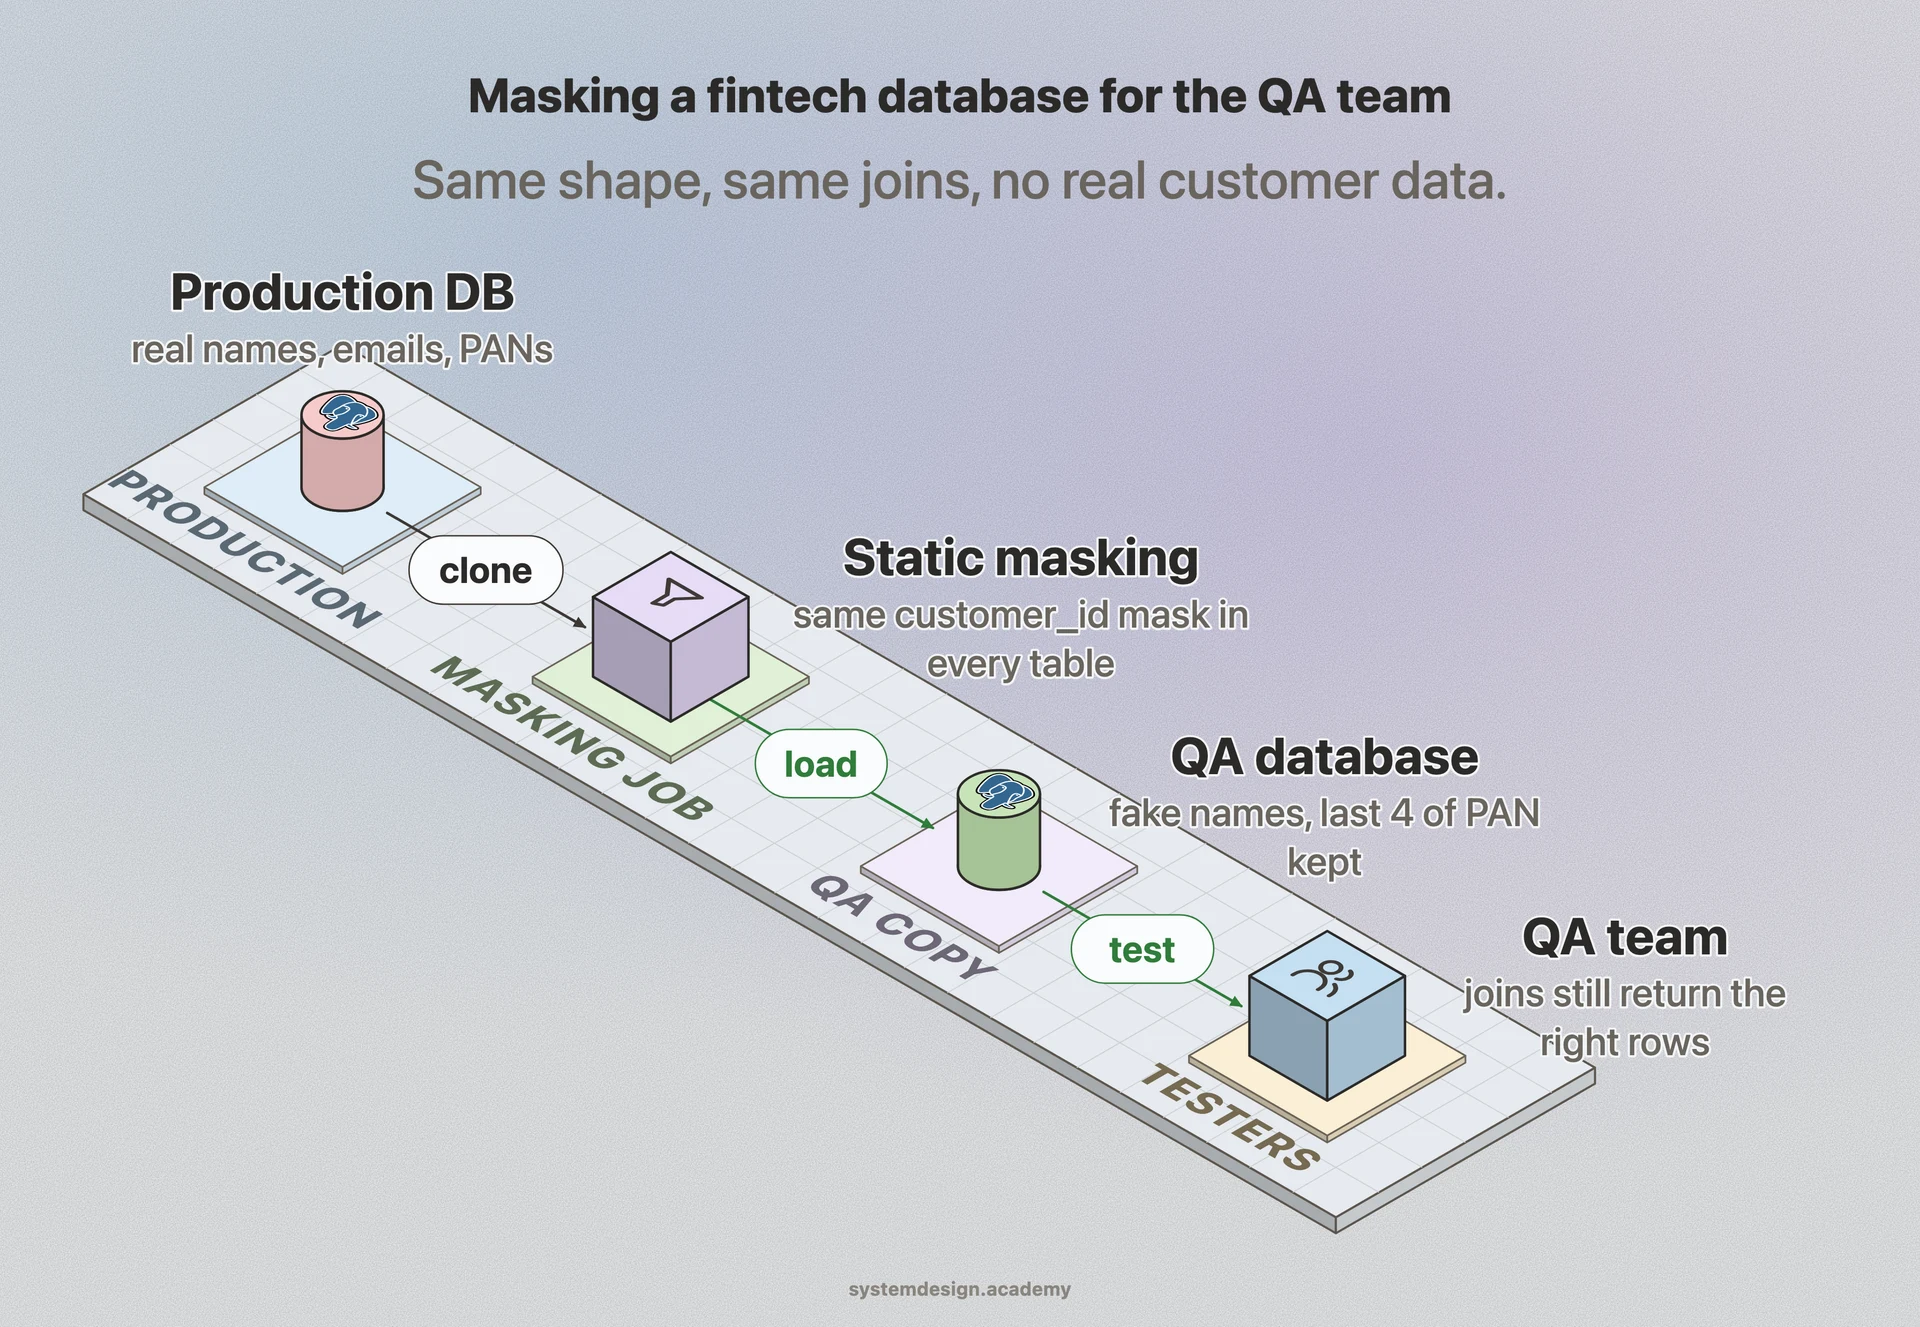
Reach for masking whenever non-production systems need production-like data: building features, load testing, training analysts, sharing data with a vendor, or running demos. It is also a direct lever for GDPR, HIPAA, and PCI DSS, all of which expect that real personal data is not casually copied into dev and test environments.
The hard part is referential integrity. If customer_id is masked one way in the orders table and a different way in the payments table, every join across them breaks and your test data becomes garbage. This is why deterministic, consistent masking across all tables matters, and why teams that bolt masking on after the fact often struggle.
The other trade-off is leakage through correlation. If you mask names but leave an exact birth date, ZIP code, and rare medical diagnosis untouched, someone can often re-identify the person anyway. Masking has to be applied to the whole set of quasi-identifiers, not just the obvious primary fields, or it gives a false sense of safety. Dynamic masking also does not protect against a user who can run aggregate queries or dump the underlying table directly, so it is a presentation-layer control, not a storage control.