Every act of processing personal data needs a lawful basis. There are six: consent, contract, legal obligation, vital interests, public task, and legitimate interests. Consent is the one most people know, but it is often the weakest choice because it has to be freely given, specific, informed, and as easy to withdraw as to give. A pre-ticked checkbox is not valid consent.
GDPR splits responsibility between the controller (the company that decides why and how data is processed) and the processor (a vendor that processes data on the controller's behalf, like AWS or a payment provider). The two sign a Data Processing Agreement that spells out obligations. A controller stays liable even when a processor causes the breach.
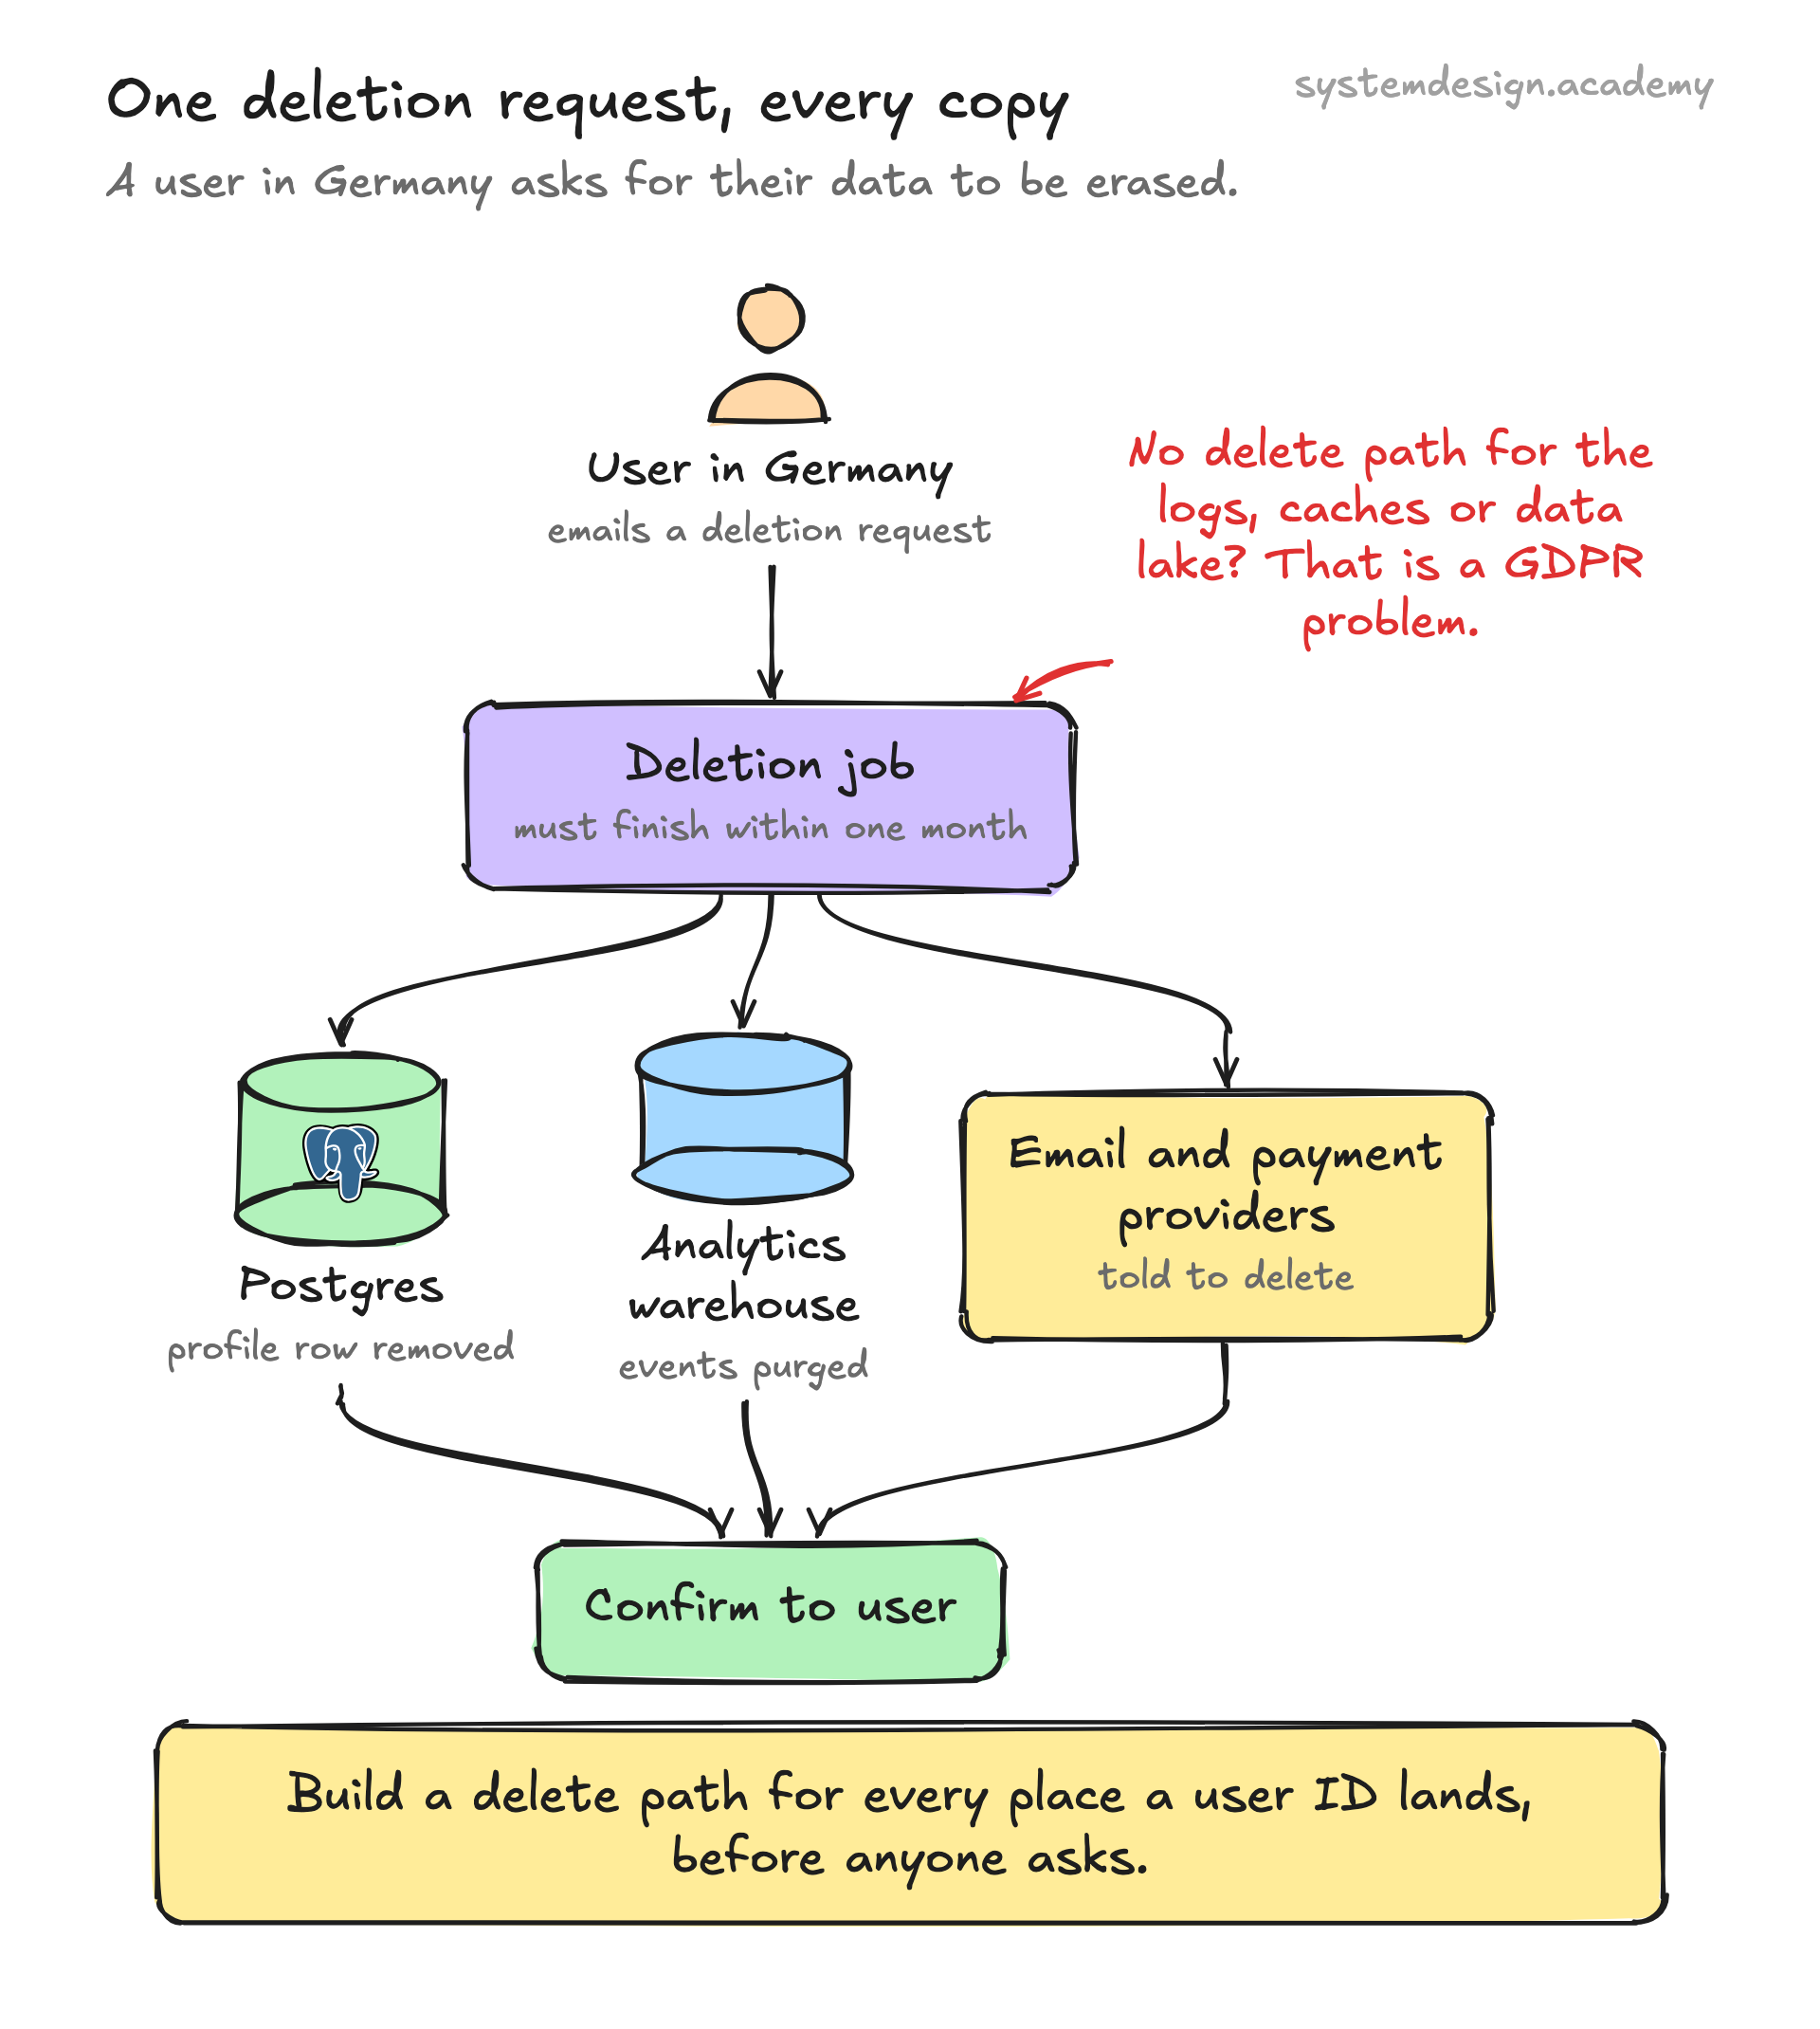
It grants individuals concrete rights: access (get a copy of their data), rectification (fix errors), erasure (the right to be forgotten), portability (export data in a machine-readable format like JSON or CSV), and the right to object. Most requests must be answered within one month, free of charge.
Two engineering principles are baked in. Data protection by design means privacy is a default in the system, not bolted on later. Data minimization means you only collect what you actually need. If a data breach happens, the controller must notify the supervisory authority within 72 hours of becoming aware of it.