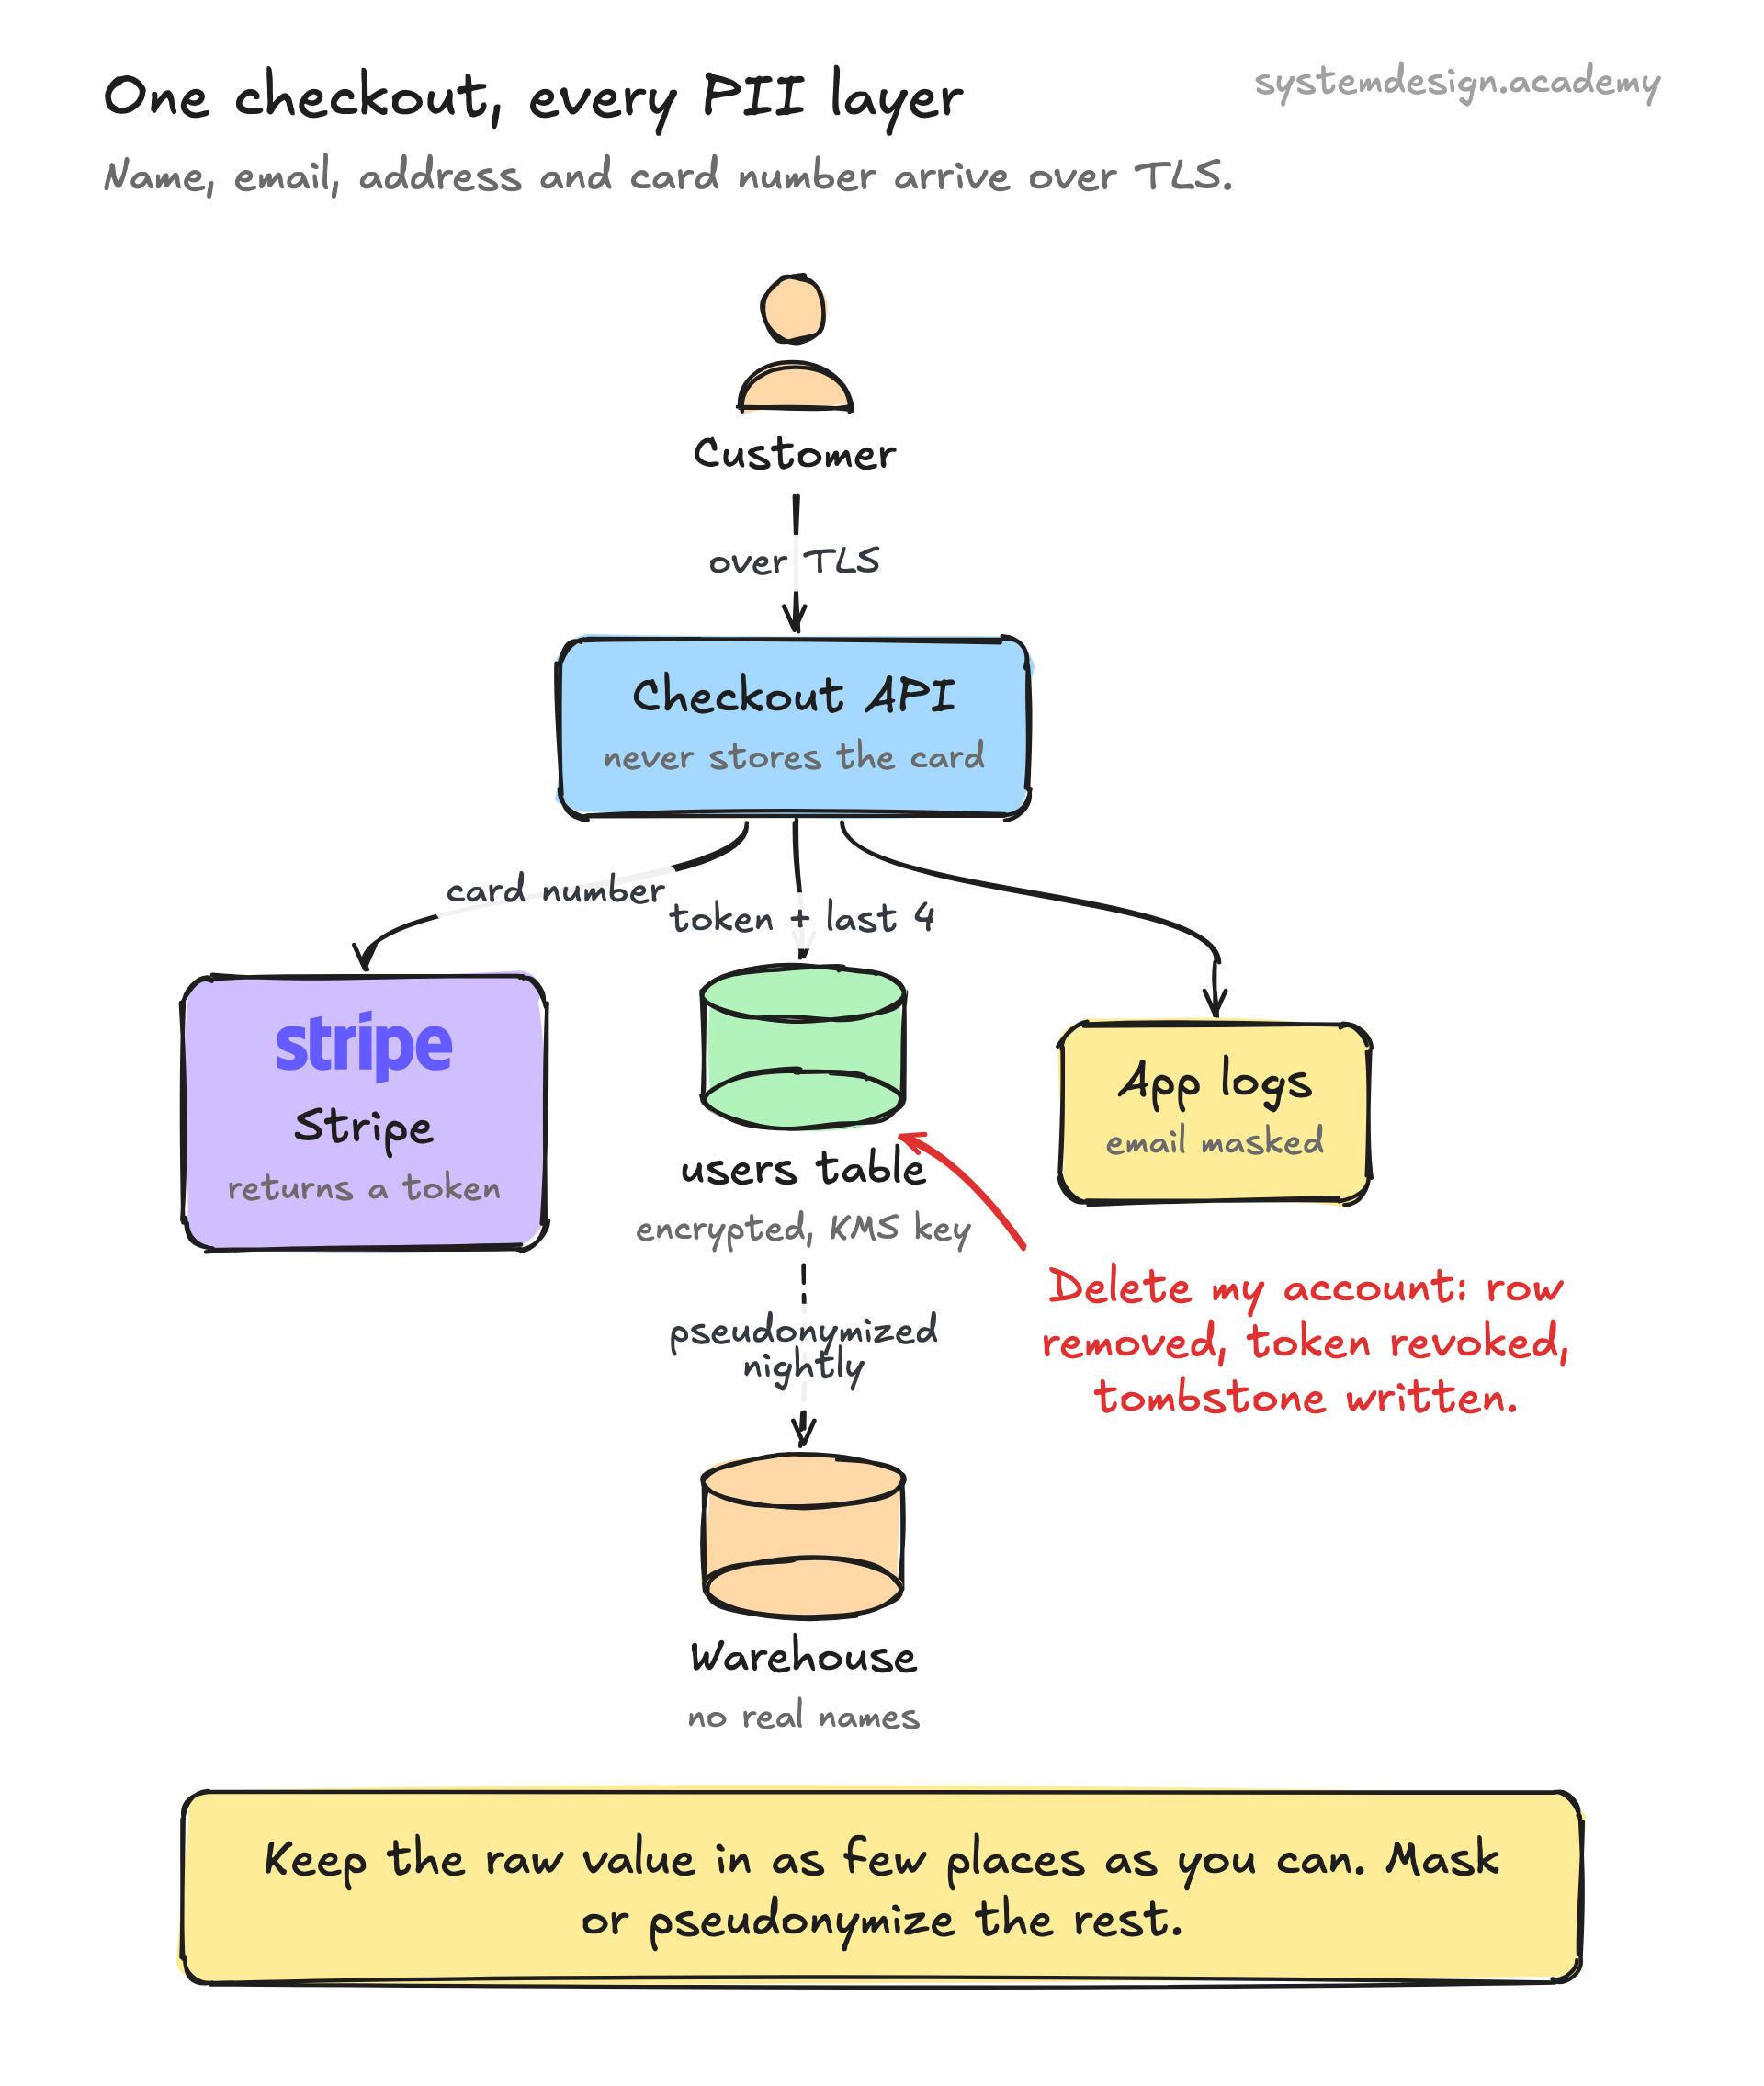
Picture a checkout flow. The user submits name, email, shipping address, and card number over TLS. Your API never stores the card. It sends the number straight to Stripe, which returns a token, and you save only the token plus the last 4 digits for display.
The name, email, and address go into a users table where those columns are encrypted at rest with a KMS-managed key. Application logs scrub the email down to a masked form so a leaked log file does not leak inboxes. A nightly job pseudonymizes the order data before it lands in the analytics warehouse, so the BI team can count orders by region without ever seeing a real name.
When that user later clicks delete my account, a workflow removes their row, revokes the Stripe token, and writes a tombstone record proving the deletion happened. That single flow shows every layer working together: minimize, tokenize, encrypt, mask, pseudonymize, audit, and delete on request.