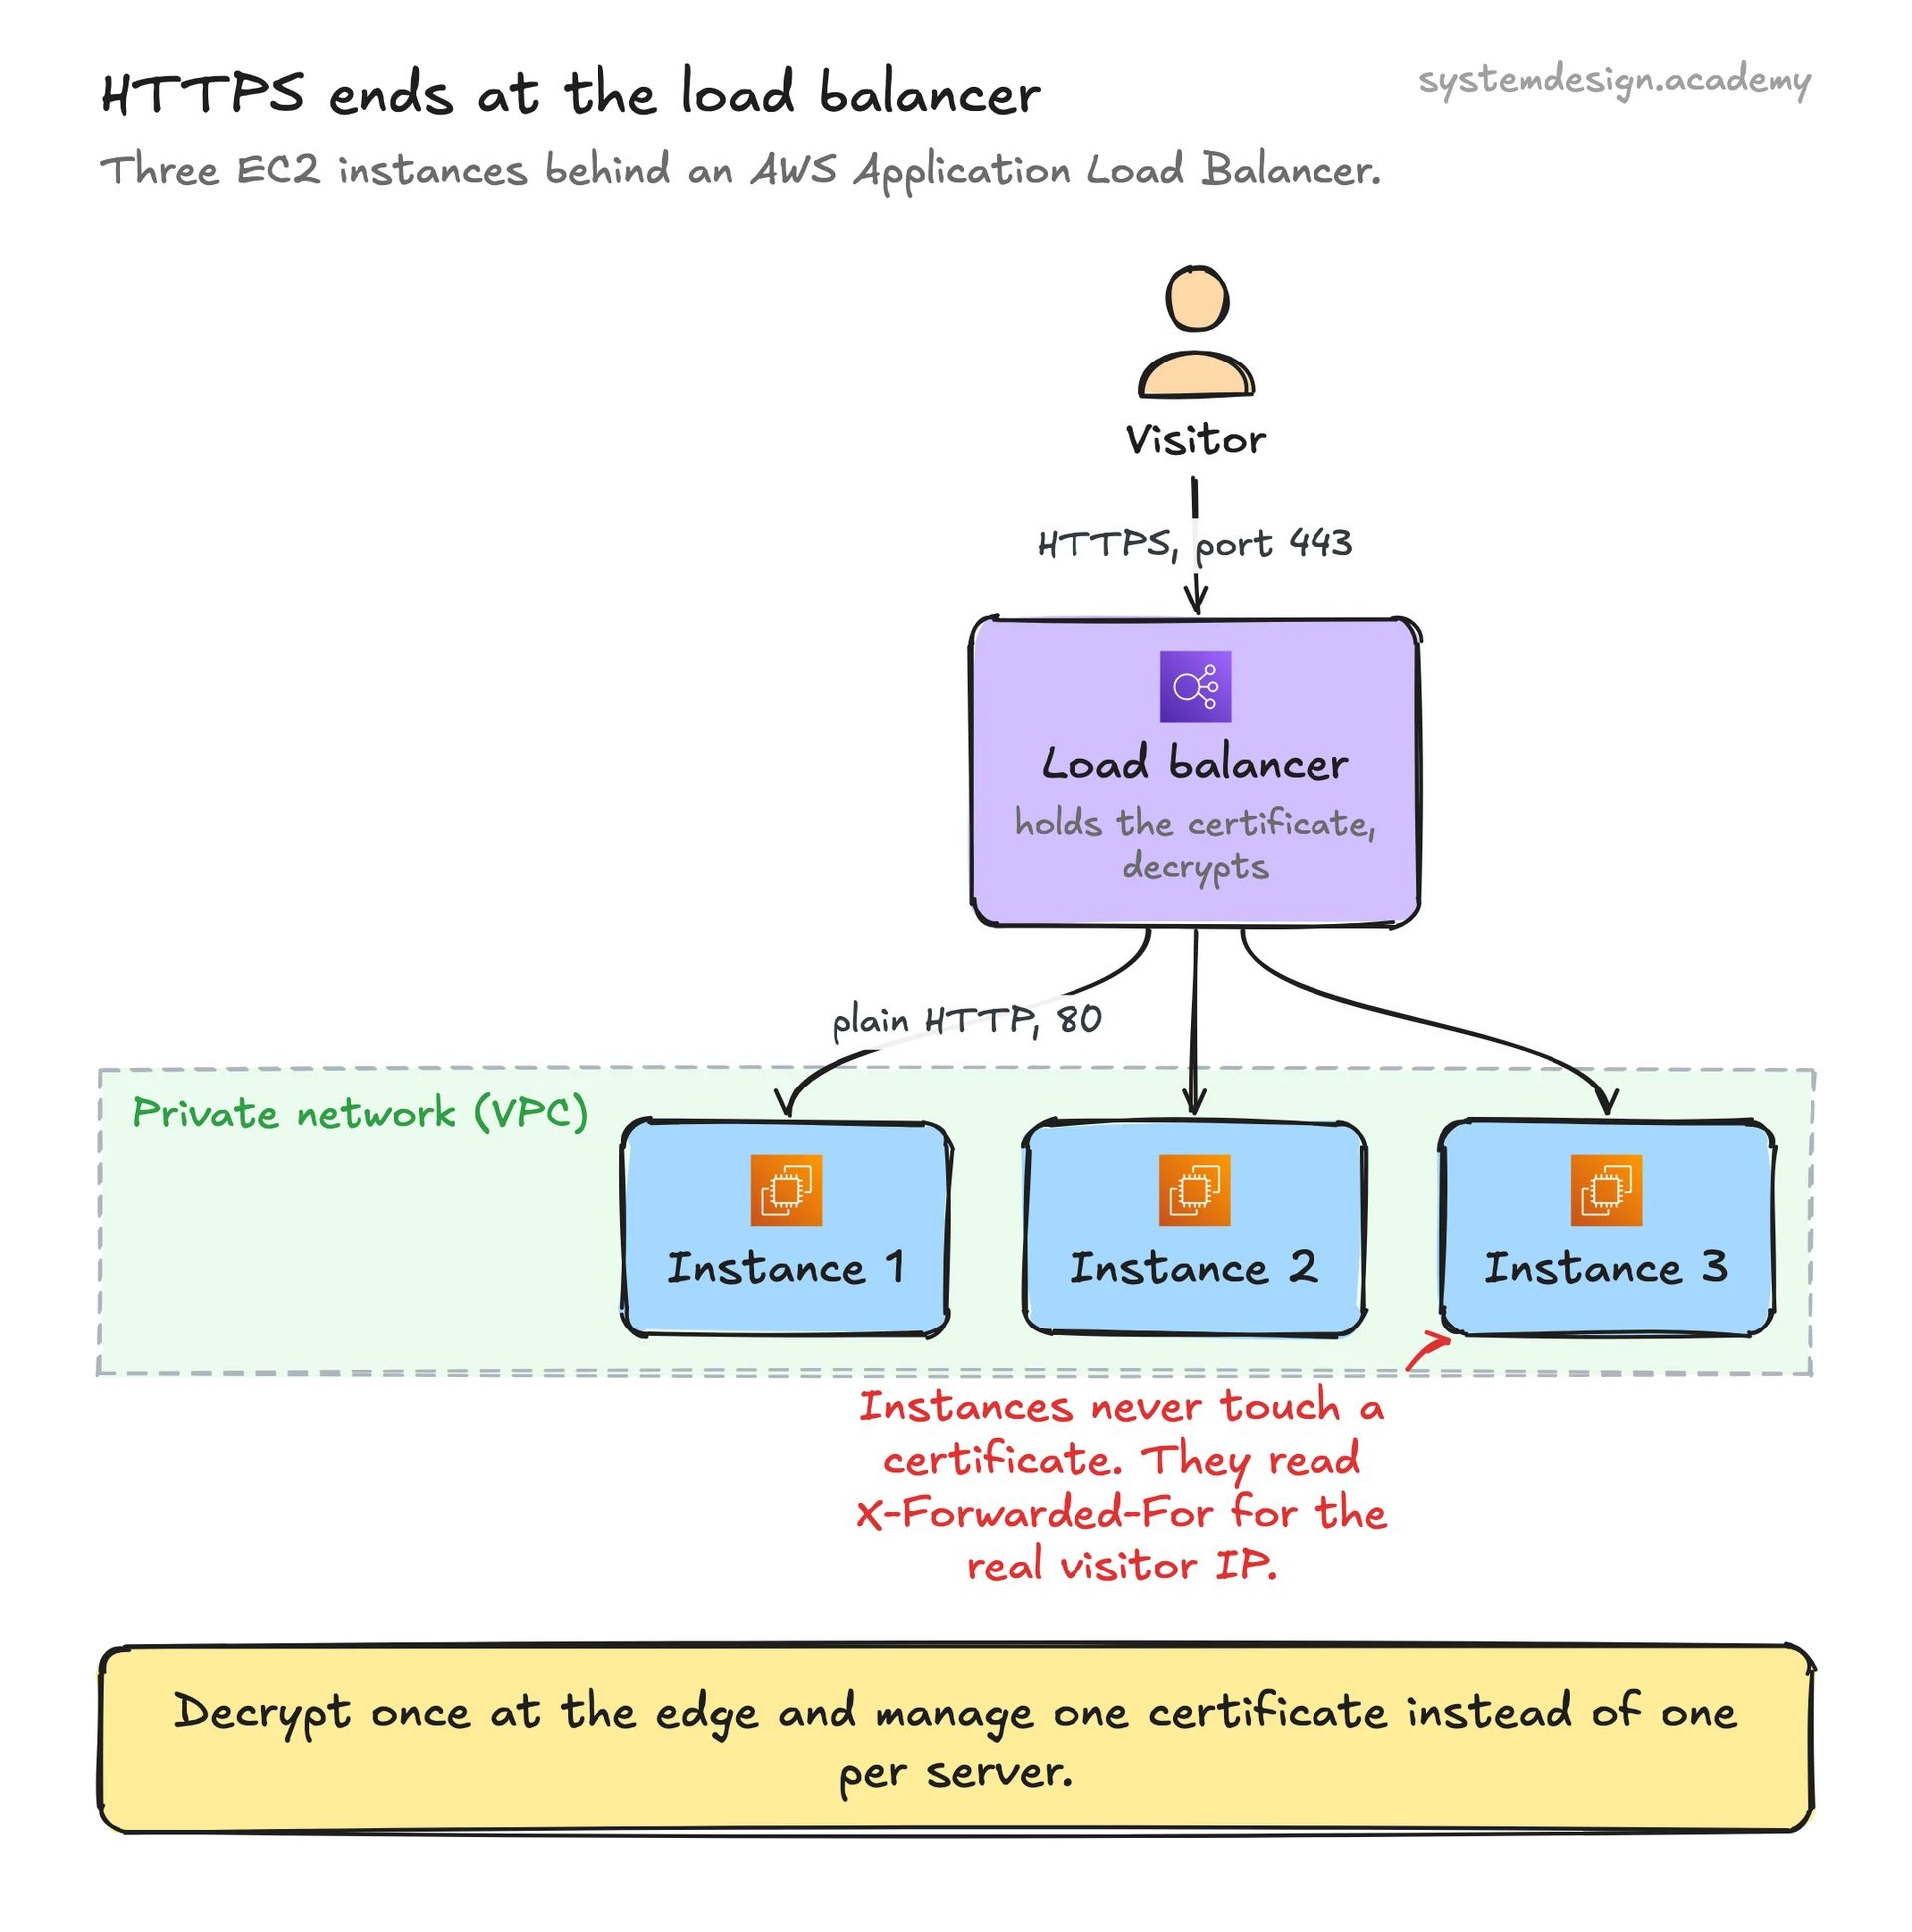
You install the TLS certificate and private key on the proxy (Nginx, HAProxy, an AWS ALB, Cloudflare, and so on). When a client connects, the proxy runs the TLS handshake: it presents the certificate, negotiates a cipher, and derives session keys. This handshake involves expensive public-key operations, which is the part you are trying to move off your application servers.
Once the session is established, the proxy decrypts each request into plain HTTP bytes. Because it now sees the unencrypted request, it can read the Host header, the path, and cookies, which lets it route, load balance, cache, rate limit, and add headers like X-Forwarded-For and X-Forwarded-Proto. A pure TCP passthrough cannot do any of that because it never sees inside the encryption.
From the proxy to the backend, the traffic is plain HTTP by default. That is fine if the link is a trusted private network. If you also encrypt the proxy-to-backend hop, you have TLS re-encryption (sometimes called SSL bridging): the proxy terminates the client TLS, inspects the request, then opens a fresh TLS connection to the backend. Compliance regimes like PCI DSS often require this so traffic is never in plaintext on the wire, even internally.