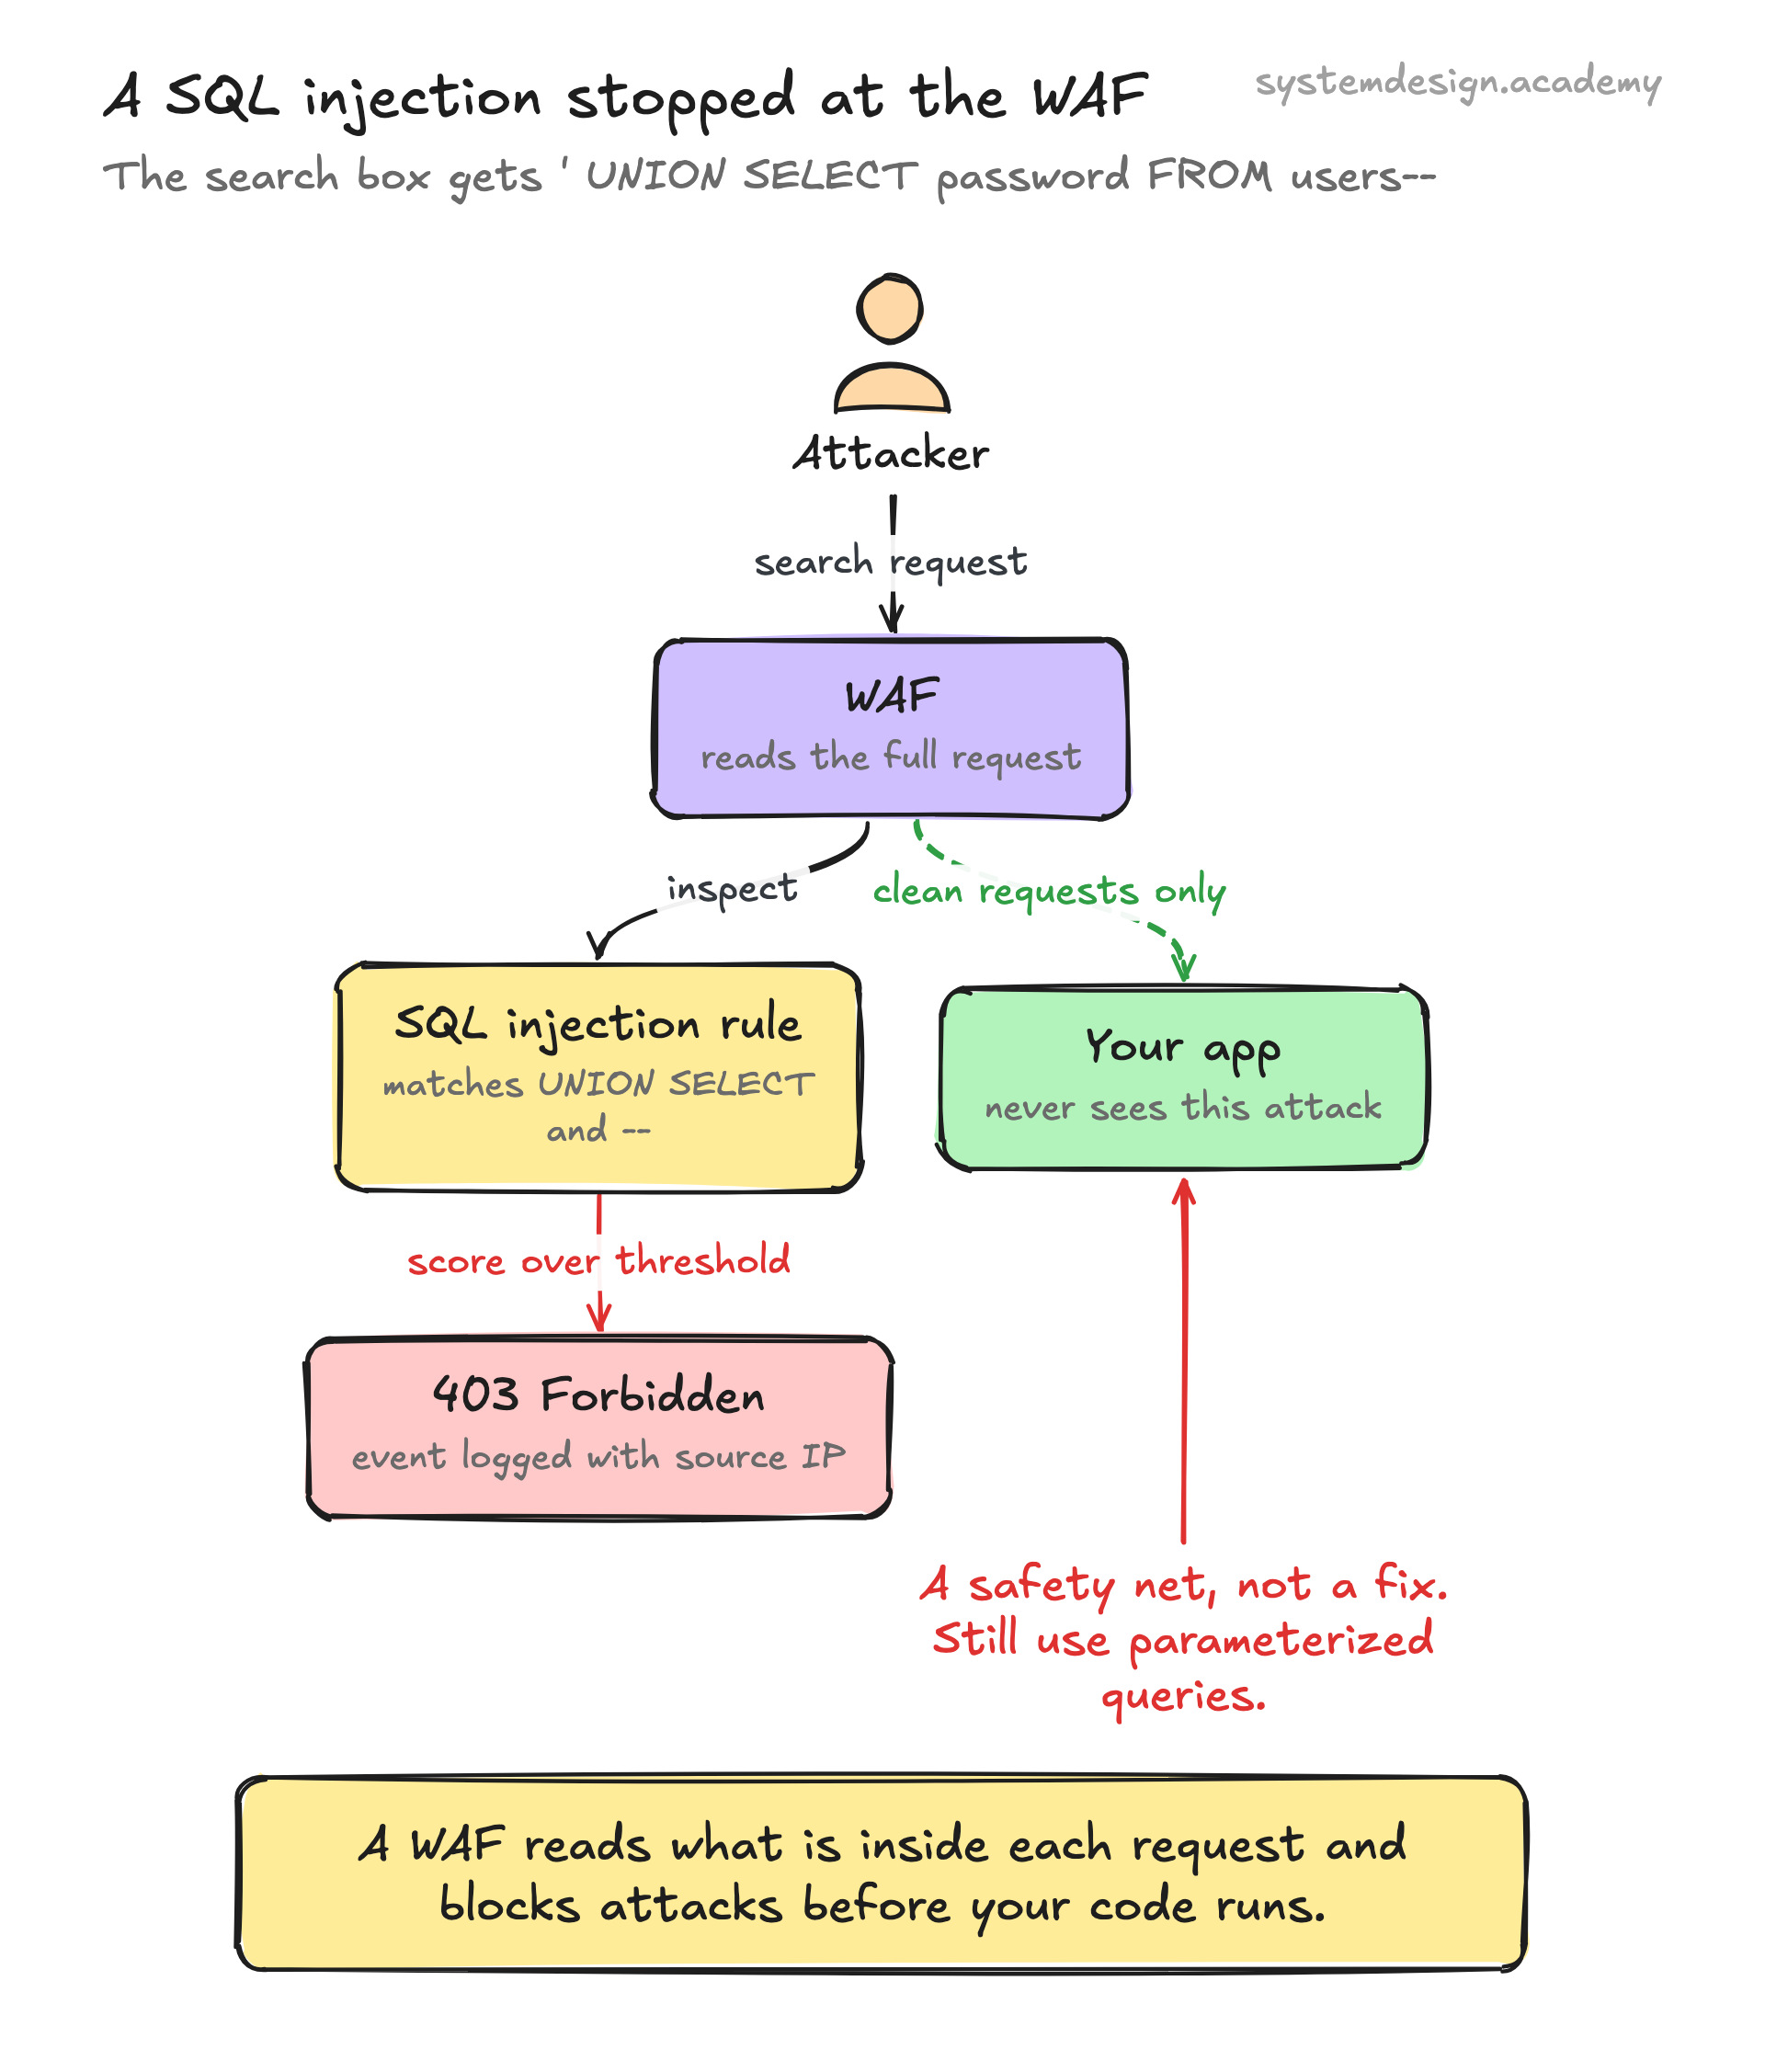
A WAF is a reverse proxy that every request to your application passes through. It reads the full HTTP request (URL, headers, cookies, query string, and body) and decides whether to allow it, block it, or flag it before the request ever touches your application code.
The key difference from a normal network firewall is the layer it works at. A network firewall operates at layers 3 and 4, so it only sees IP addresses, ports, and protocols. A WAF operates at layer 7, the application layer, so it can read that a form field contains the string ' OR 1=1-- and recognize it as a SQL injection attempt.
WAFs are most often described in terms of the OWASP Top 10, the industry list of the most common web vulnerabilities. A good WAF ships with rules that cover injection, broken access patterns, XSS, and similar categories out of the box, then lets you add your own rules on top.