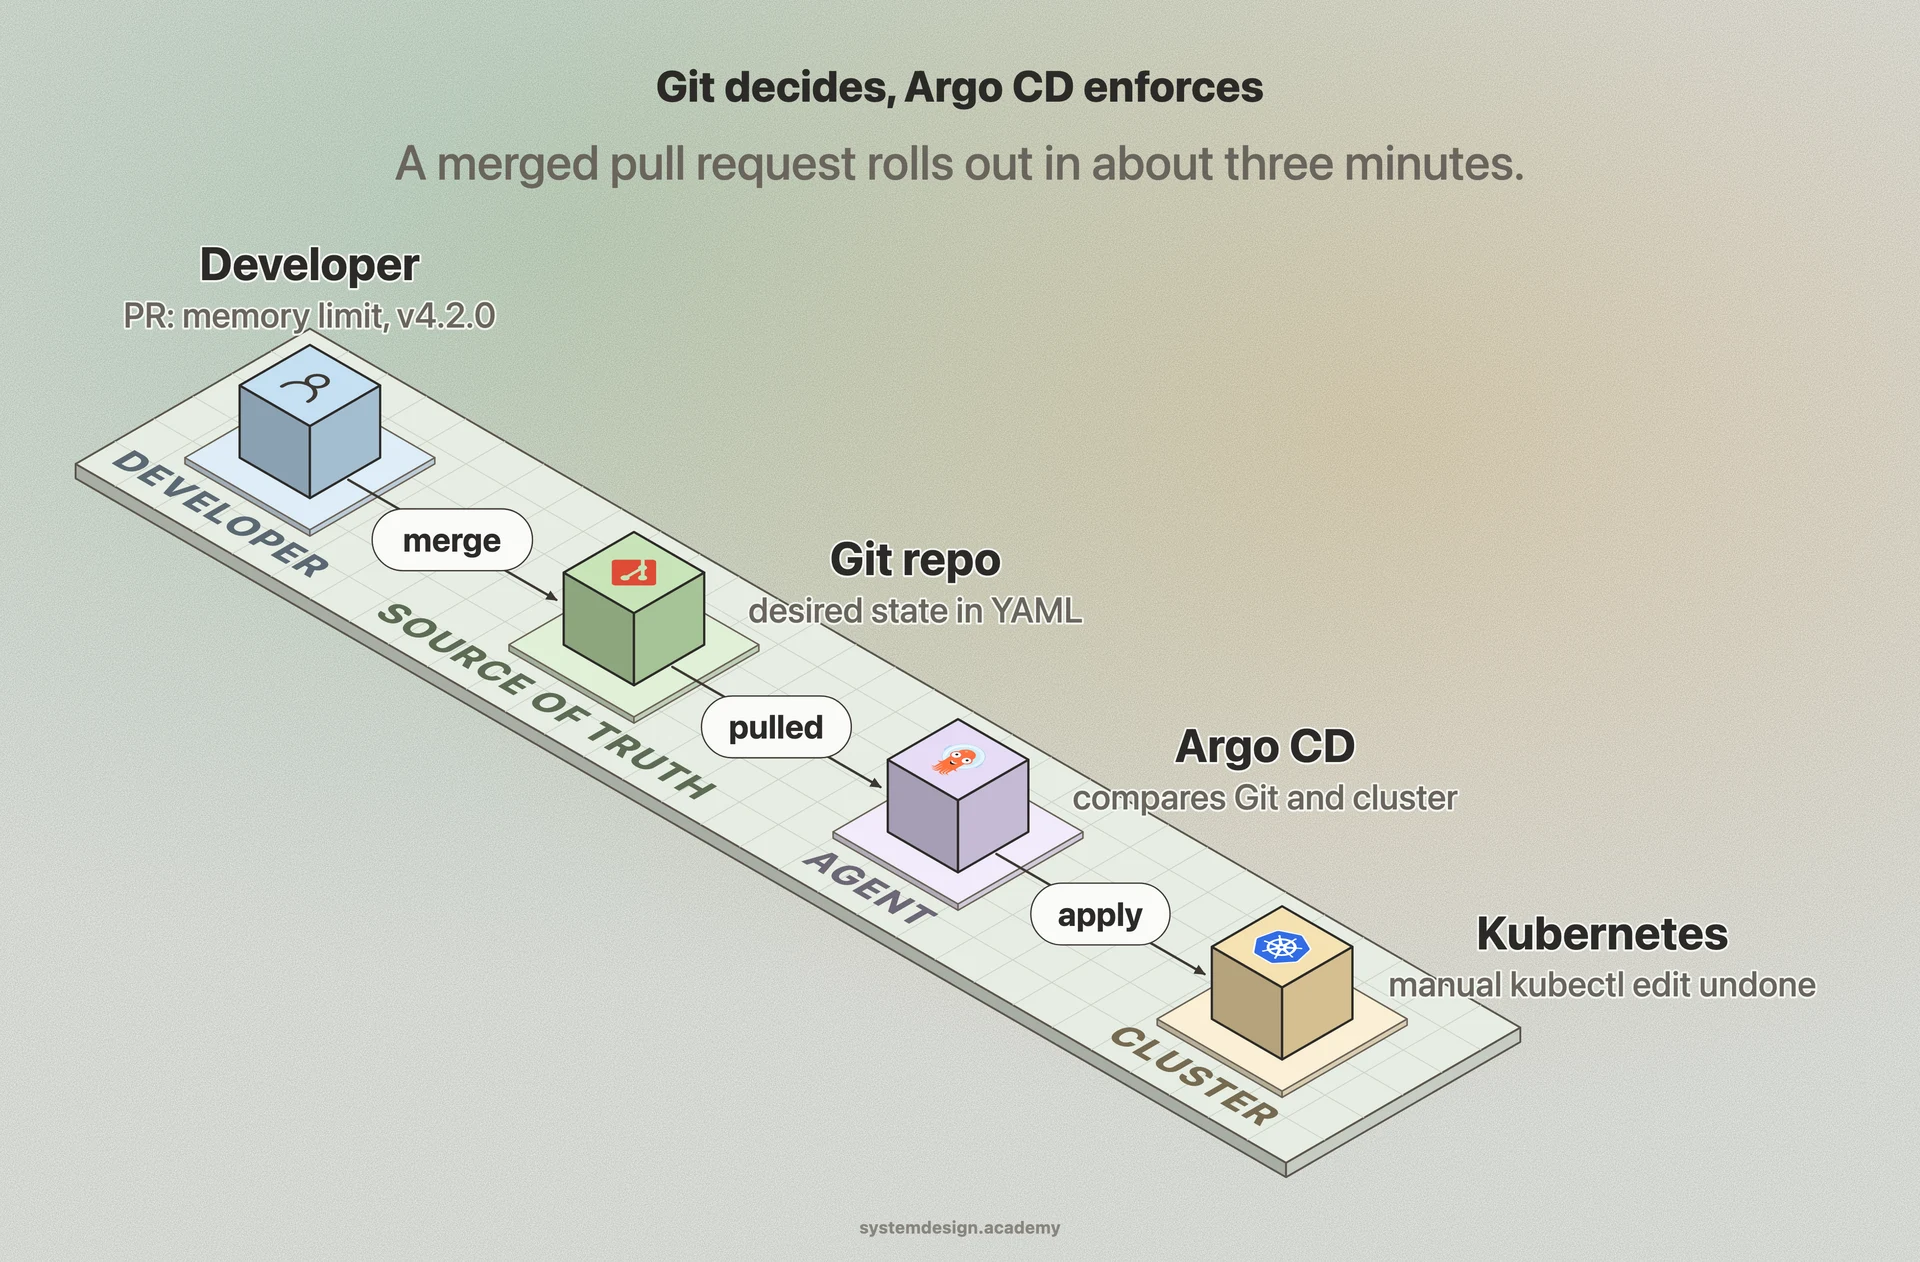
A GitOps agent runs inside the target environment, most often a Kubernetes cluster. The two dominant agents are Argo CD and Flux. The agent is given a Git repository and a path, and it watches for commits.
On a loop, usually every few minutes, the agent does three things. It reads the desired state from Git. It reads the actual state from the cluster API. It computes the difference. If the two match, it does nothing. If they differ, either because someone pushed a new commit or because something drifted in the cluster, it applies the changes to bring the cluster back in line with Git. This is the reconciliation loop, and it is the same control-loop pattern Kubernetes itself uses internally.
A key detail is pull versus push. In a traditional CI pipeline, the pipeline reaches into the cluster and pushes changes, which means the pipeline needs cluster credentials. In GitOps, the agent lives inside the cluster and pulls from Git, so the cluster credentials never leave the cluster and your CI system only needs write access to a Git repo. That separation is a big part of why GitOps is considered more secure.
Image updates are handled the same way. When CI builds a new container image and pushes it to a registry, a small automation commits the new image tag back into the Git repository. The agent then sees the commit and rolls it out. The deploy is just another reconciliation.