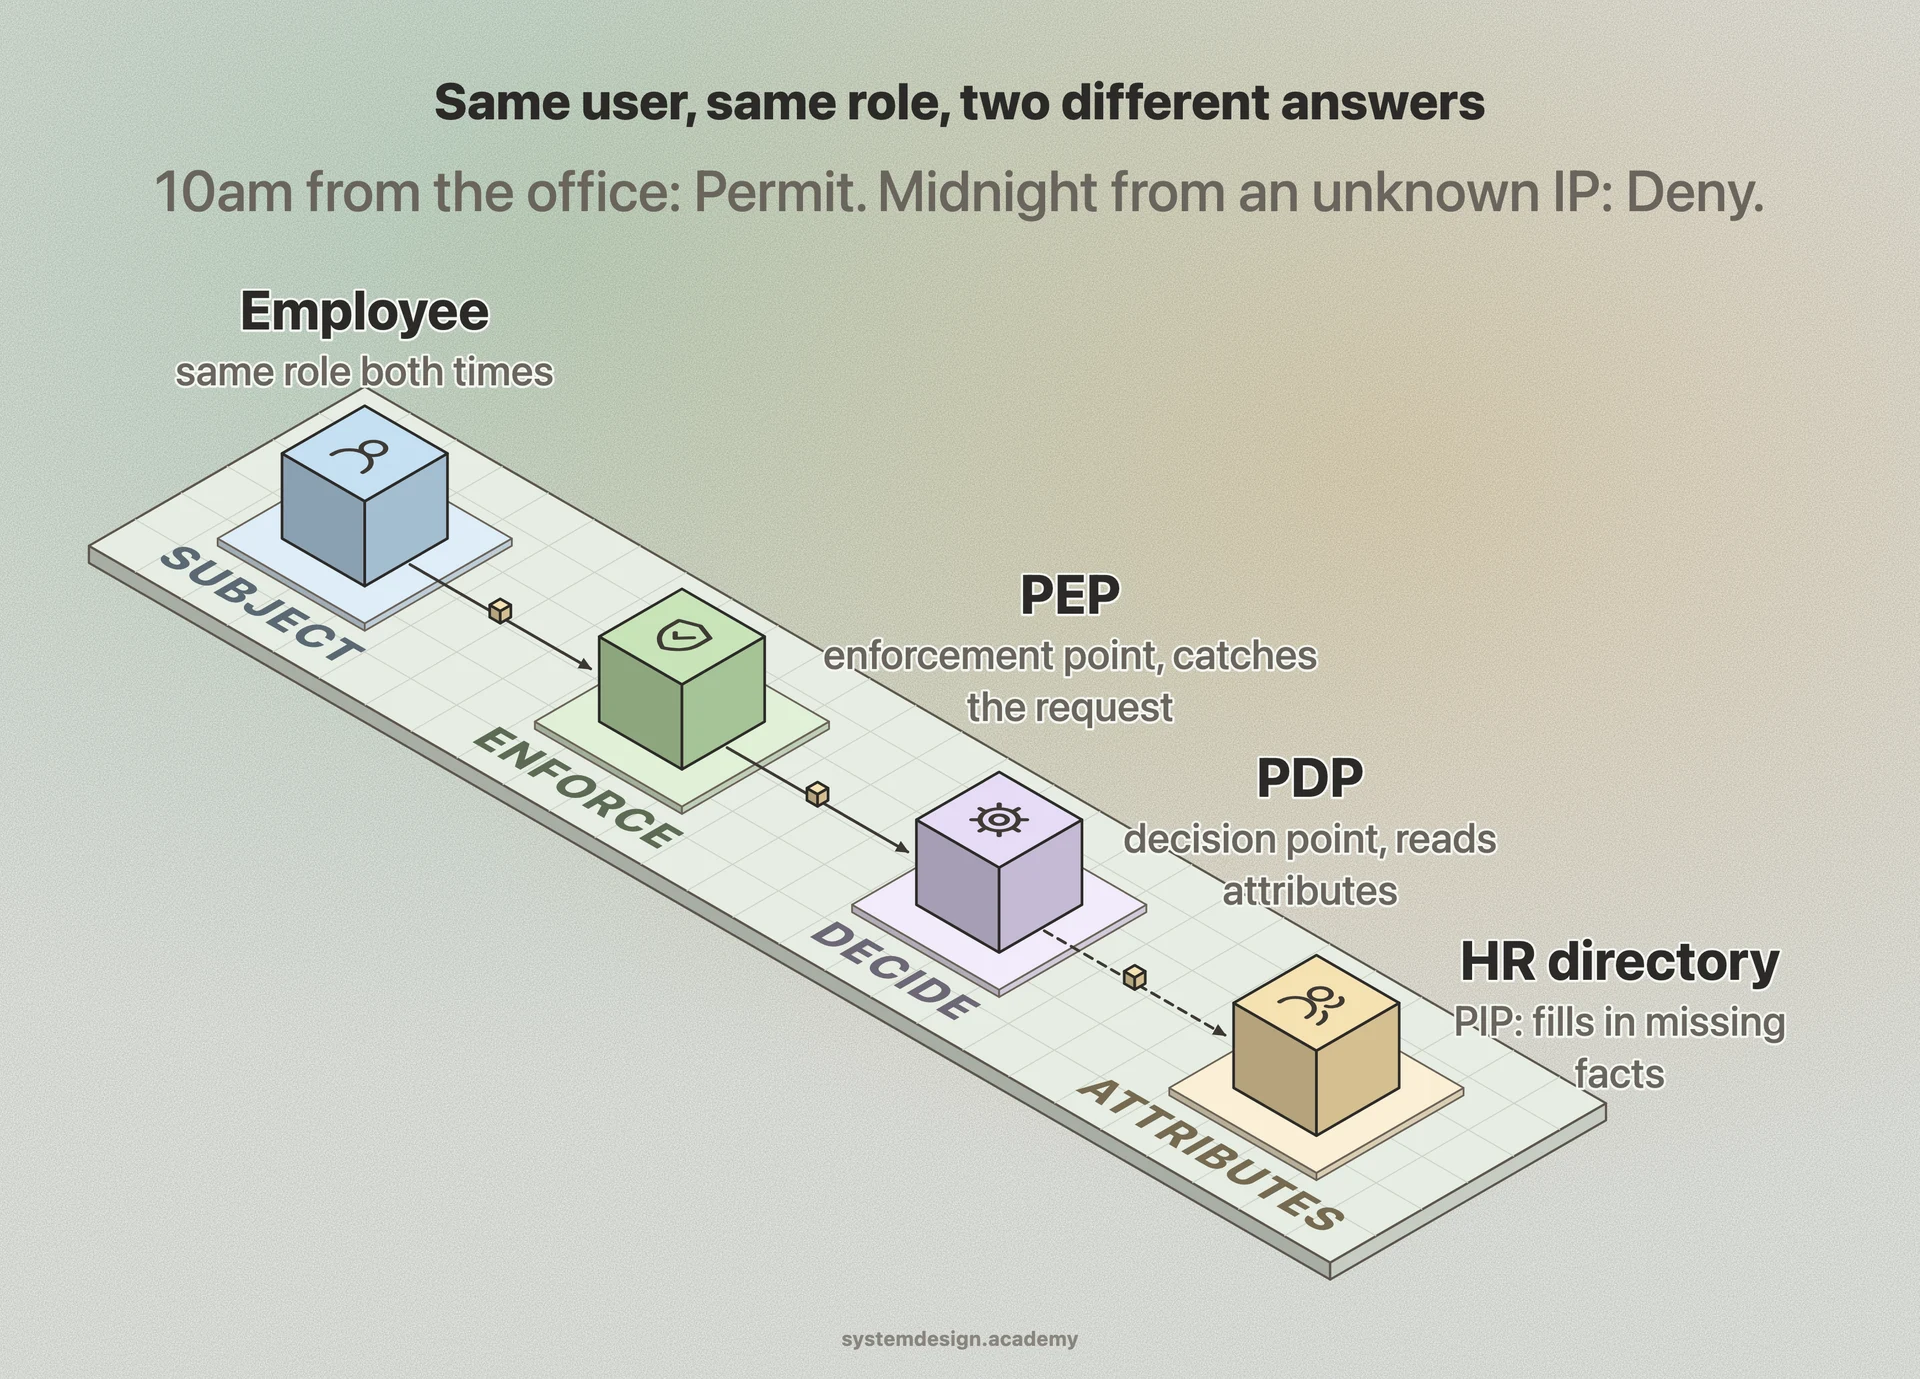
Attribute-Based Access Control is a way to answer one question: should this subject be allowed to perform this action on this resource right now? Instead of looking up a role and a static permission table, ABAC looks at attributes (key-value facts) about four things and runs them through policy rules.
The four attribute categories are: subject attributes (the user's department, clearance level, team, employment status), resource attributes (the file's classification, owner, project, region), action attributes (read, write, delete, approve), and environment attributes (time of day, source IP, device posture, MFA status).
A policy is a rule that combines those attributes with boolean logic. A classic example: allow read if subject.clearance >= resource.classification AND subject.country == resource.dataResidency. Nothing is hardcoded to a named role, so the same engine can express very fine-grained decisions.