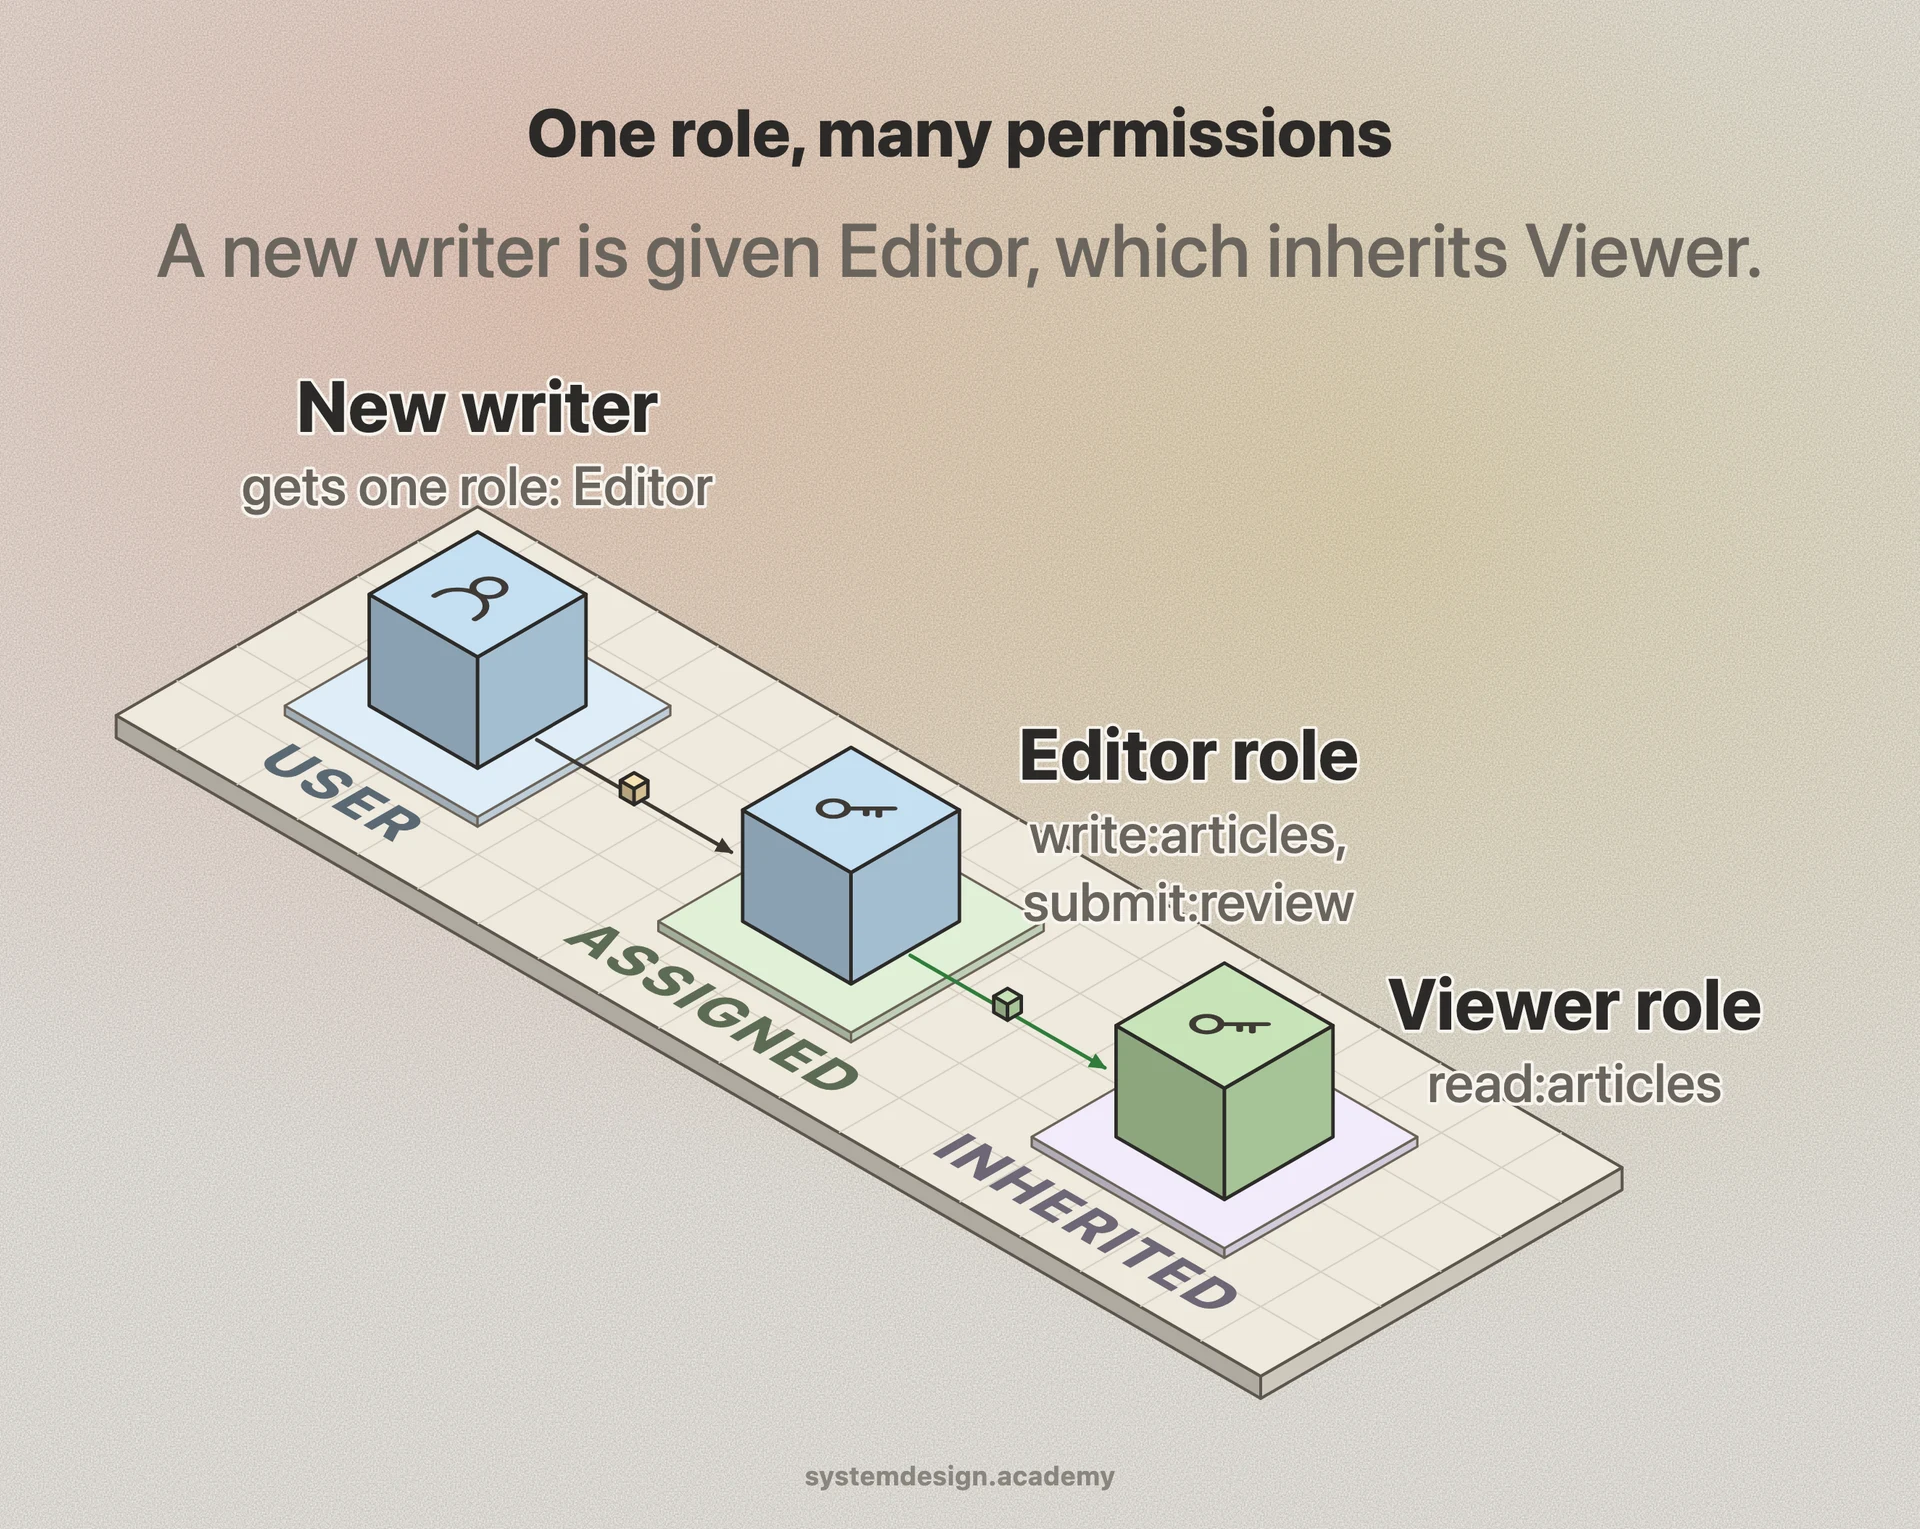
Use RBAC when access maps cleanly to job functions and the same access applies to everyone in that function. Internal tools, admin dashboards, SaaS team accounts, and Kubernetes clusters all fit this shape well. It is simple to reason about, easy to audit, and reviewers can answer who can do what by reading a short list of roles.
The classic failure mode is role explosion. The moment access depends on context, like region, department, or ownership of a specific record, teams start creating roles like editor_us_west_finance. You can end up with more roles than users, which defeats the purpose.
When you need per-record or contextual rules, RBAC alone is the wrong tool. Attribute-Based Access Control (ABAC) makes decisions from attributes such as the user's department and the document's owner, and policy engines like Open Policy Agent express this directly. A common production pattern is RBAC for the coarse layer (can this user reach the billing area at all) plus ABAC or ownership checks for the fine layer (can they see this specific invoice).