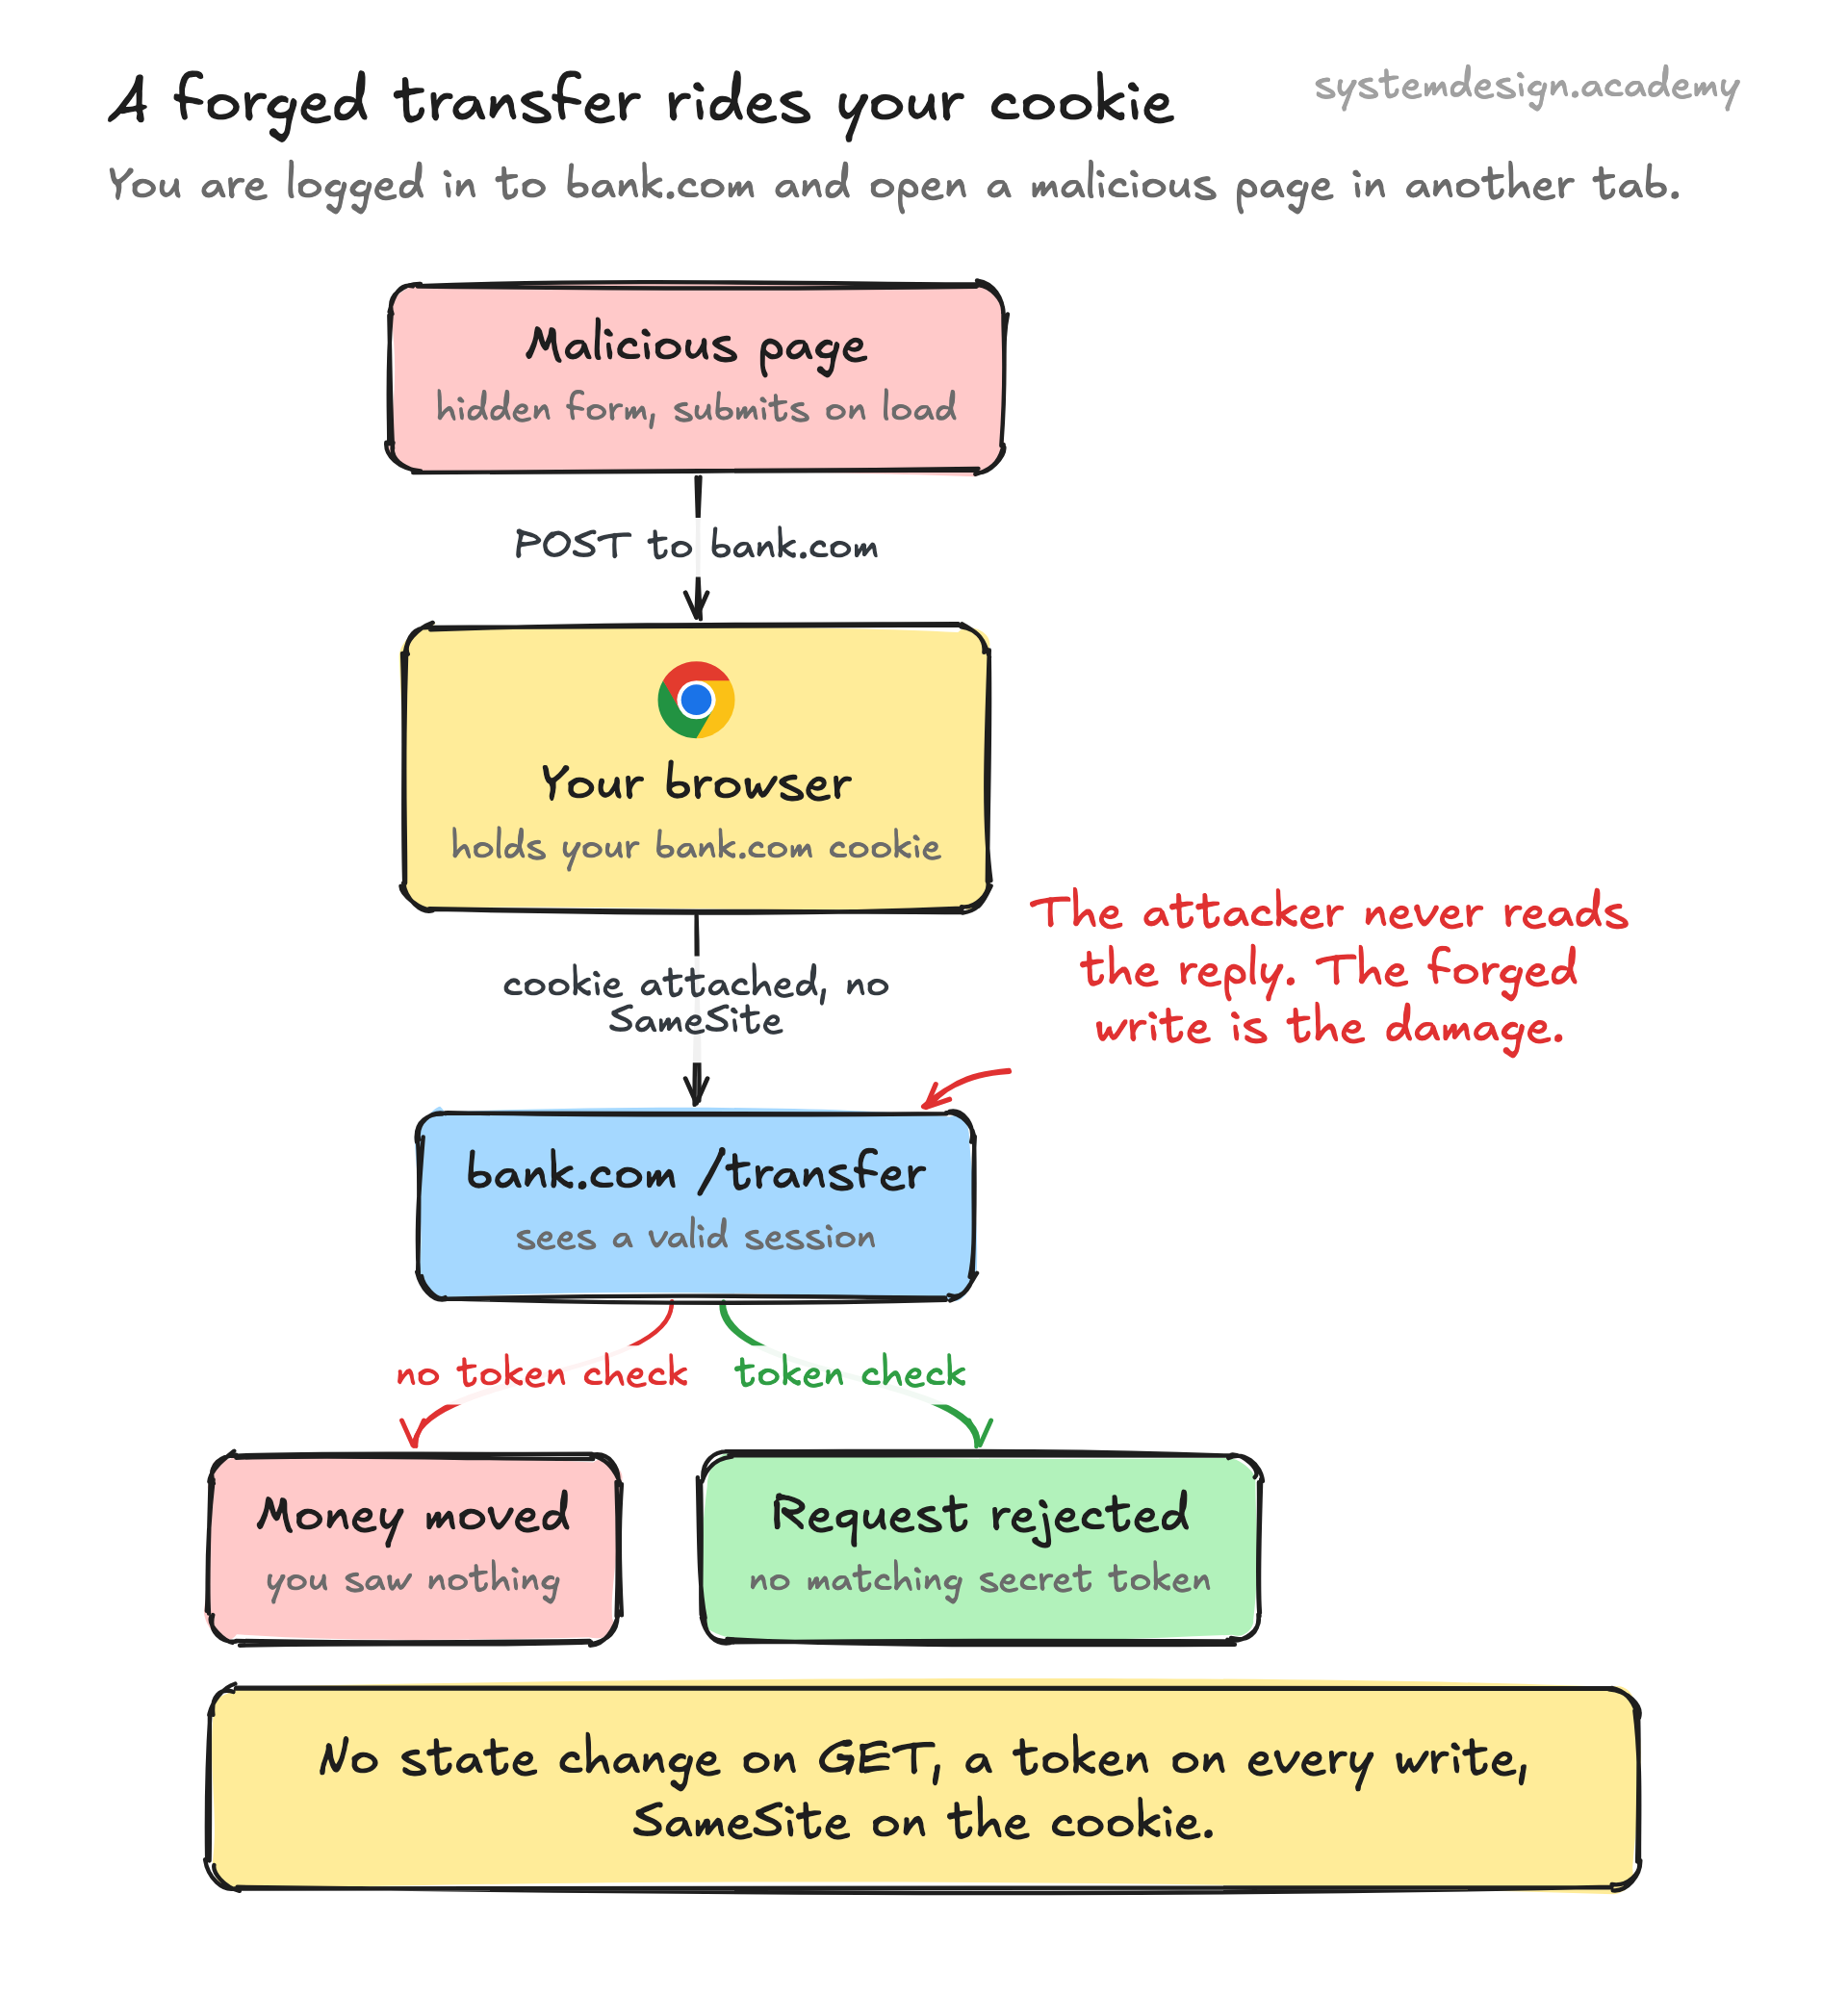
CSRF abuses the fact that browsers automatically send cookies for a domain on every request to that domain, no matter who triggered the request. If you are logged into your bank at bank.com, your browser holds a session cookie. When any page in any tab makes a request to bank.com, the browser attaches that cookie for you.
An attacker exploits this by getting your browser to fire a request to bank.com while you are logged in. They do not steal your cookie and they cannot read the response. They only need the request to reach the server with your cookie attached, so the server treats it as a legitimate action from you.
The classic targets are state-changing endpoints: transfer money, change password, change account email, delete data, add an admin. Read-only pages are not the prize. CSRF is about forcing a write, not stealing data, which separates it from XSS.