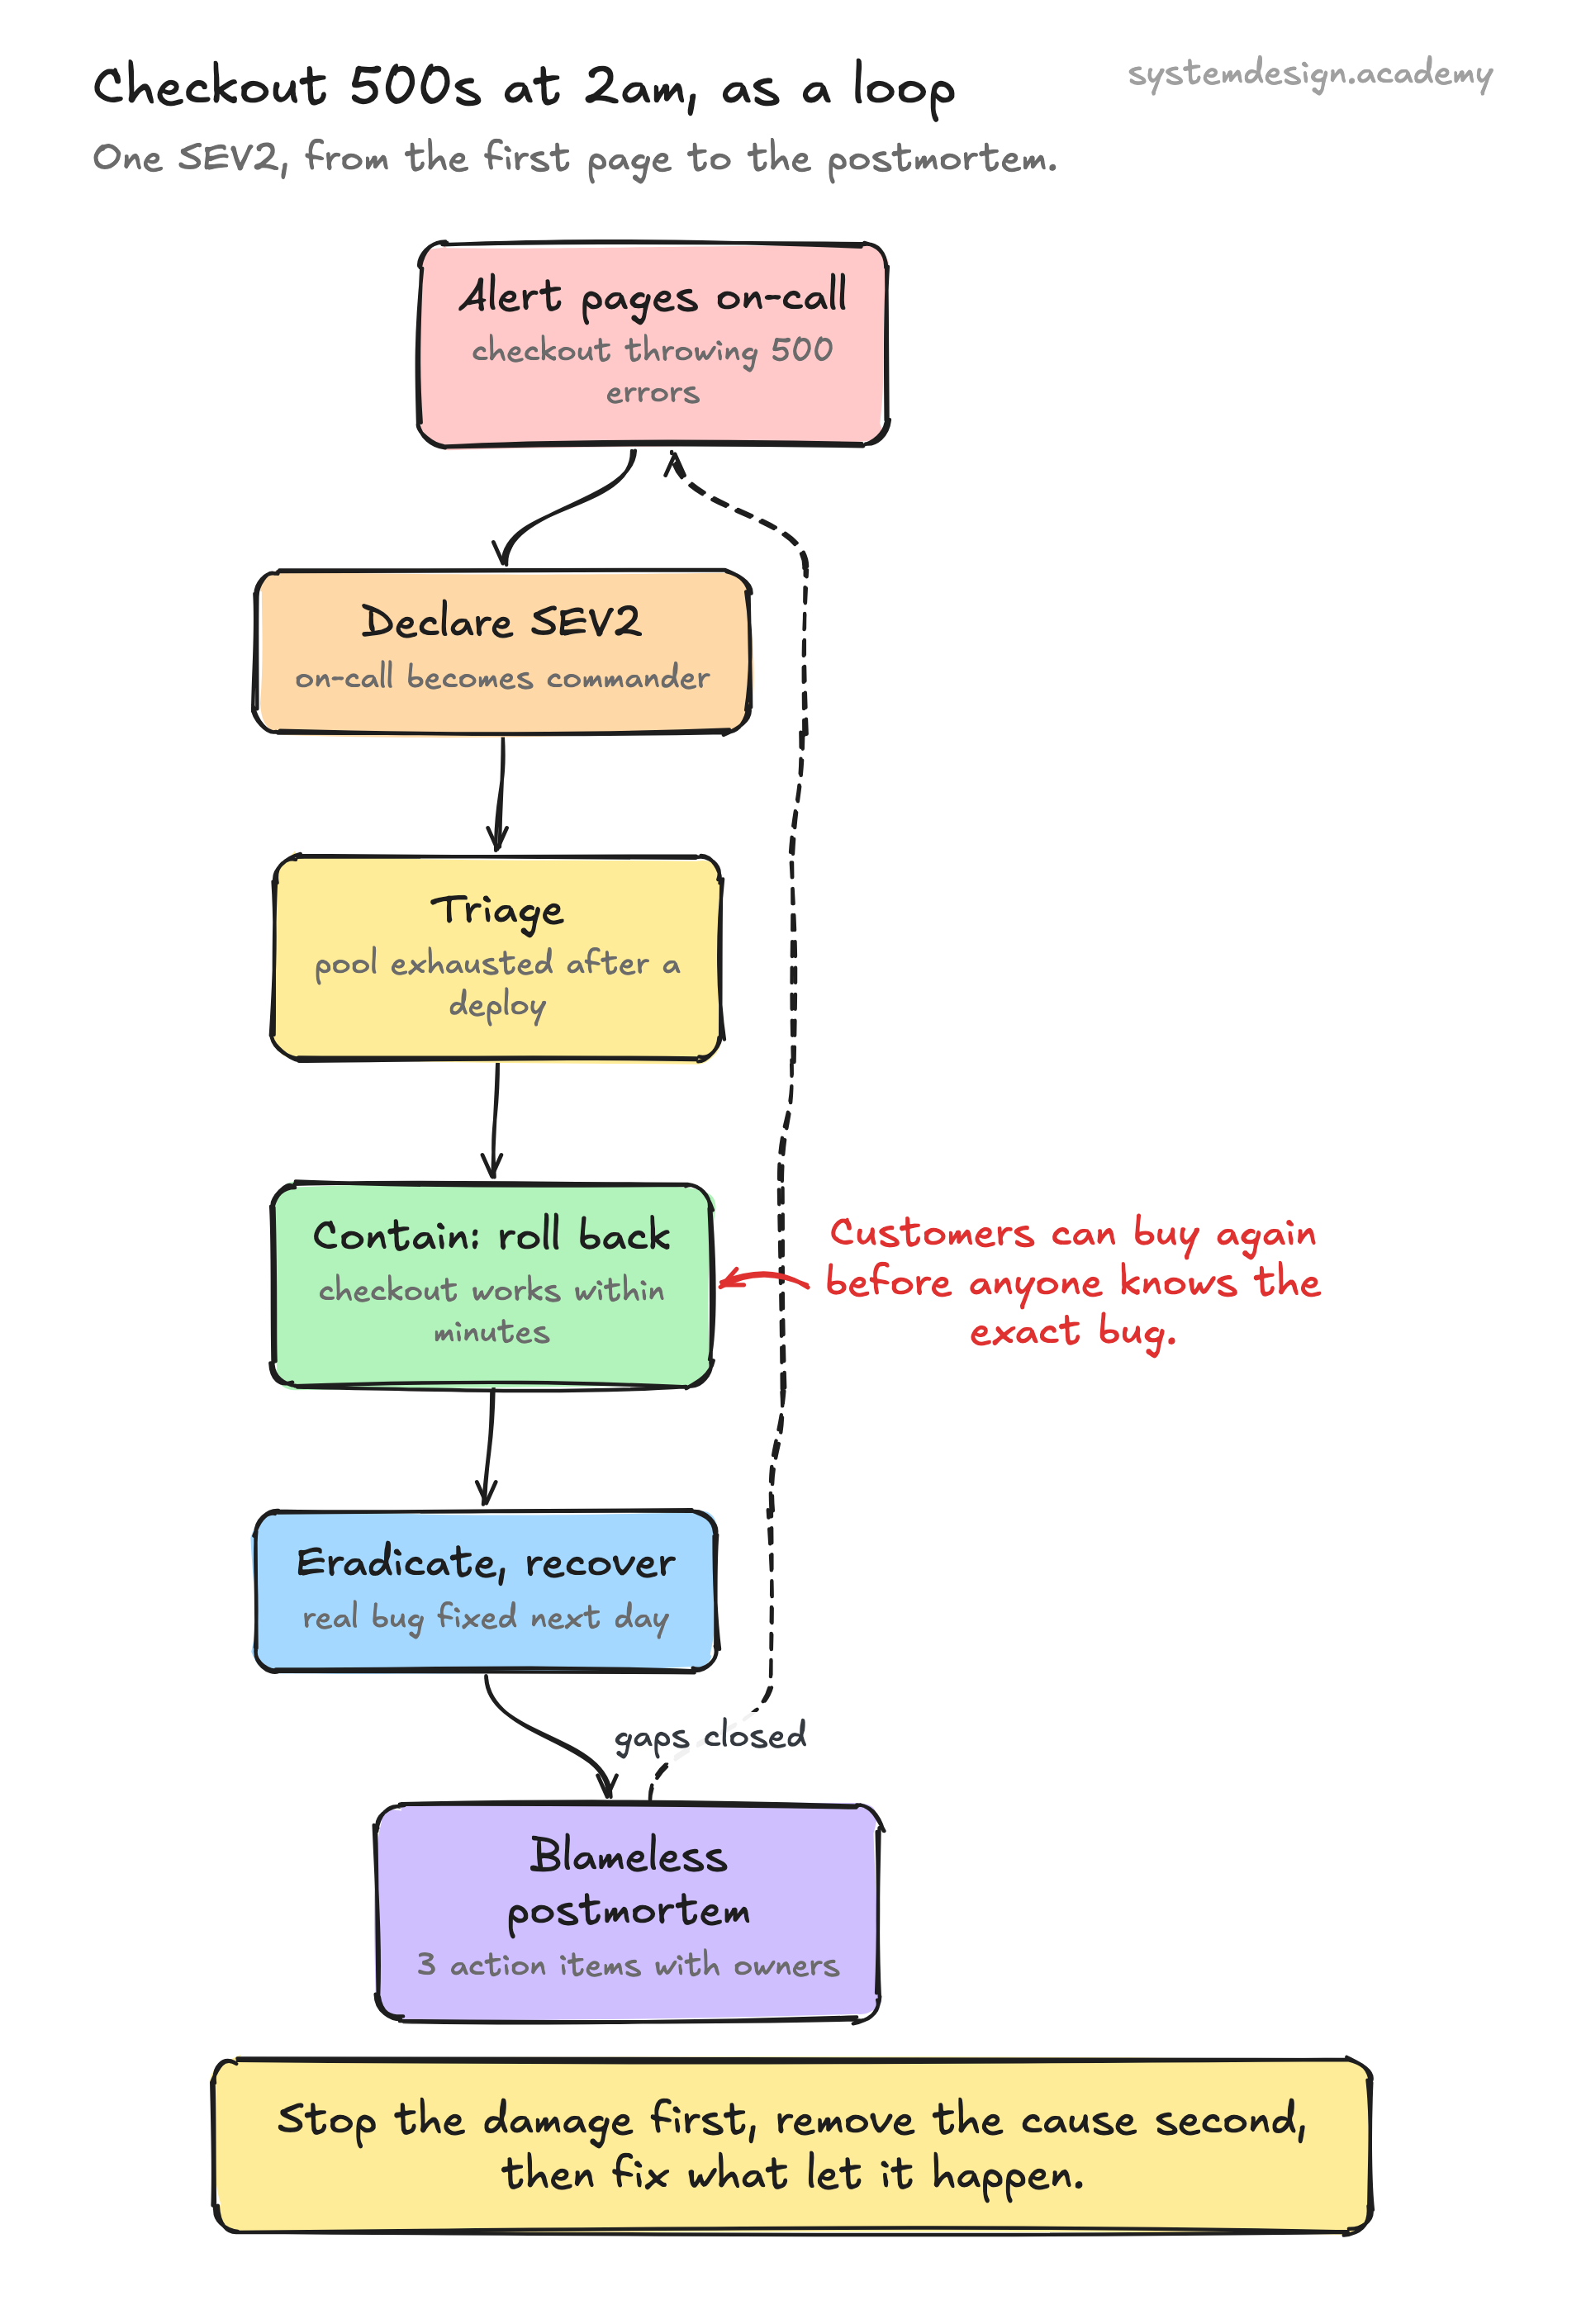
Preparation happens before anything breaks. You write runbooks for likely scenarios, set up logging and alerting, define who the incident commander is, and run game days where you simulate a breach. If you have no logs you cannot investigate, so preparation is where most of the real work lives.
Detection and triage come next. An alert fires from something like a SIEM (Splunk, Elastic, or a cloud tool like AWS GuardDuty), a customer reports an outage, or a monitor catches an error spike. Someone declares an incident and assigns a severity. A SEV1 page that wakes people up is different from a SEV3 that waits until morning.
Containment stops the bleeding. You isolate a compromised host from the network, revoke a stolen token, fail over to a healthy region, or rate-limit an abusive client. Containment is deliberately separate from eradication because you often want to keep evidence intact for forensics before you wipe the box.
Eradication removes the root cause, recovery restores service and confirms it is healthy, and the final phase is the postmortem. You write a blameless timeline of what happened, why detection was slow or fast, and concrete action items so the same gap does not reopen.