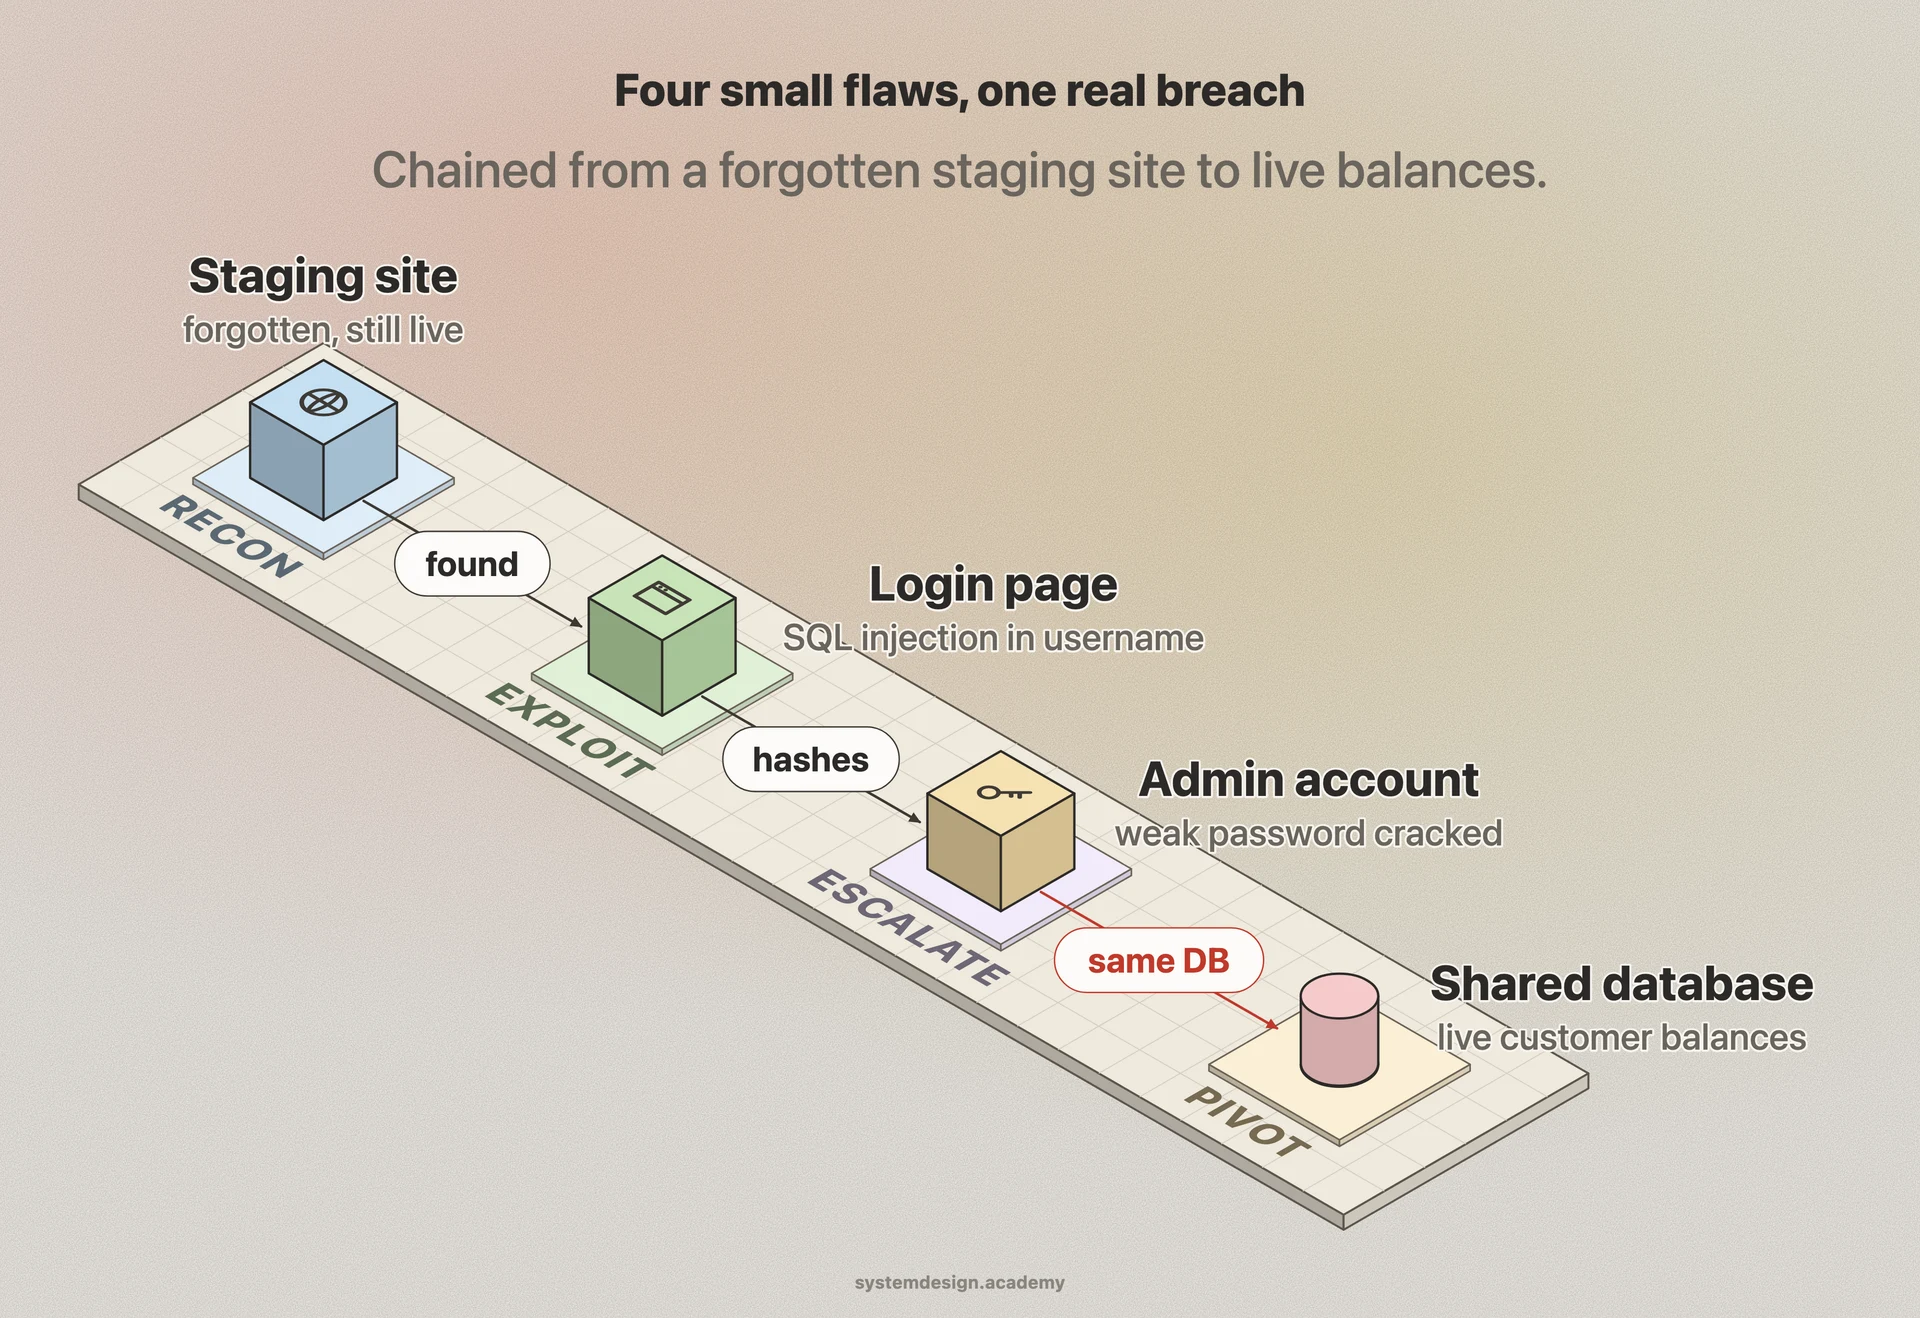
Most engagements follow a repeatable cycle. First comes reconnaissance, where the tester gathers public data: subdomains, exposed S3 buckets, employee emails, leaked credentials, and open ports found with tools like nmap. Then comes scanning and enumeration to map services, versions, and likely entry points.
Next is exploitation. The tester turns a finding into access using frameworks like Metasploit, custom scripts, or hand-crafted payloads for things like SQL injection, server-side request forgery, or broken authentication. The Burp Suite proxy is the standard tool for attacking web apps because it lets you intercept and tamper with every request.
After the first foothold comes post-exploitation: privilege escalation to admin or root, lateral movement to other machines, and persistence to survive a reboot. This stage answers the question that matters to the business: once in, how far can the attacker go? The engagement closes with a report that ranks each finding by severity, usually with CVSS scores, and gives concrete remediation steps.