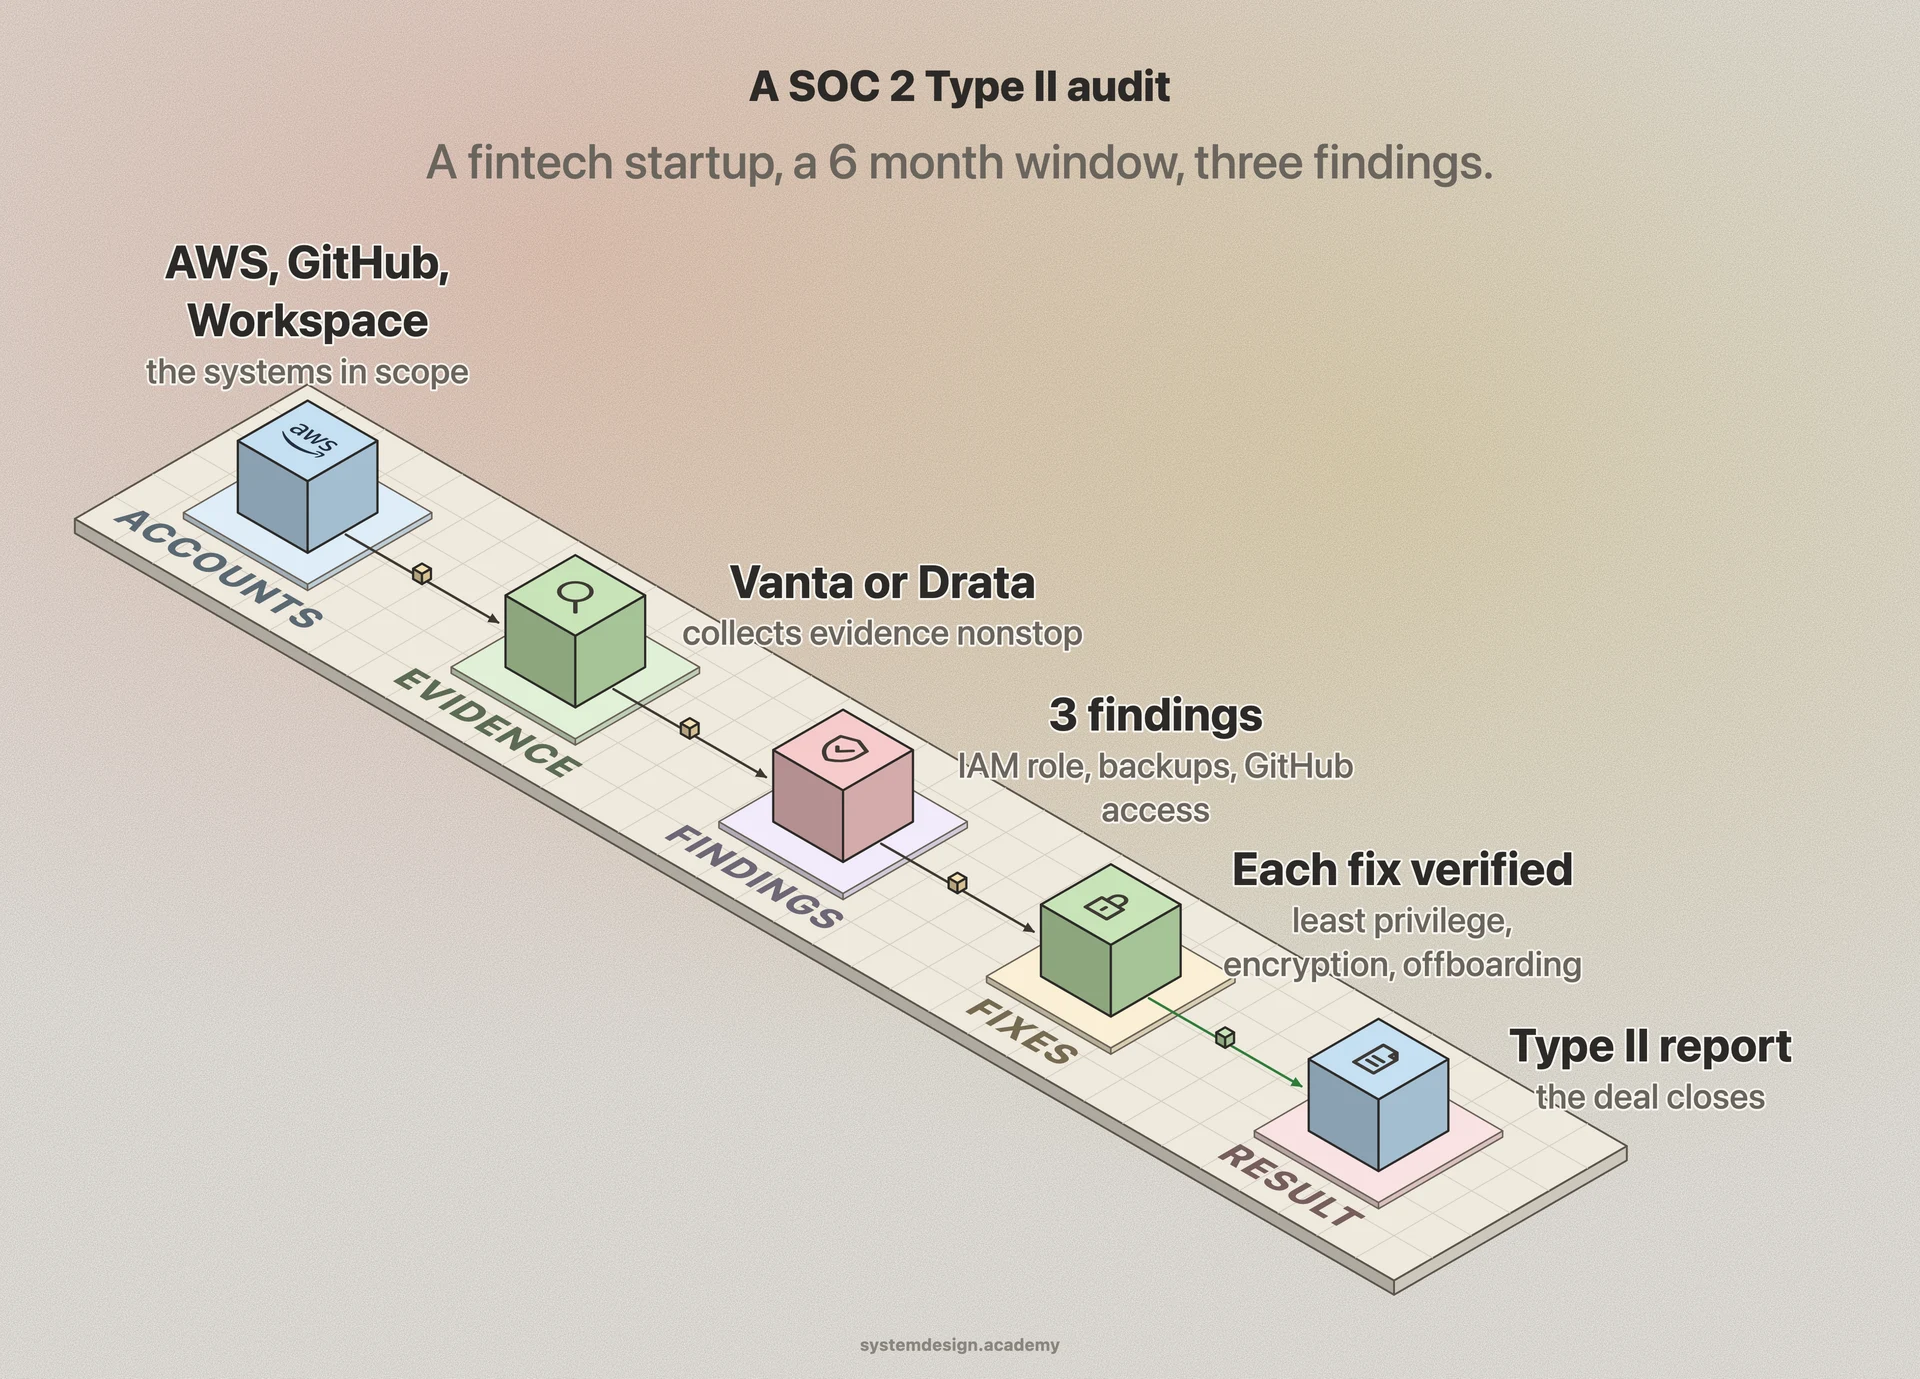
Scoping comes first. You define the systems, accounts, data stores, and time window being audited. For PCI DSS this is the cardholder data environment; for SOC 2 it is whatever processes customer data over the audit period, often 6 to 12 months.
Evidence collection mixes interviews, configuration exports, and automated scans. Auditors pull IAM policies, firewall rules, encryption settings, and access logs. Tools like AWS Config, Prowler, Scout Suite, or Nessus dump the current state of cloud accounts and flag misconfigurations against CIS Benchmarks. For code-heavy scopes, SAST and dependency scanners feed in too.
Testing has two flavors. Design testing checks that a control exists, for example MFA is required for admin access. Operating effectiveness testing checks that it held up over time, for example sampling 25 access requests across the year and confirming each had manager approval. A control that exists on paper but was bypassed twice in production fails the second test.
The output is graded findings plus a remediation timeline. Auditors map severity using something like CVSS or a simple high/medium/low scheme tied to data sensitivity and exposure.