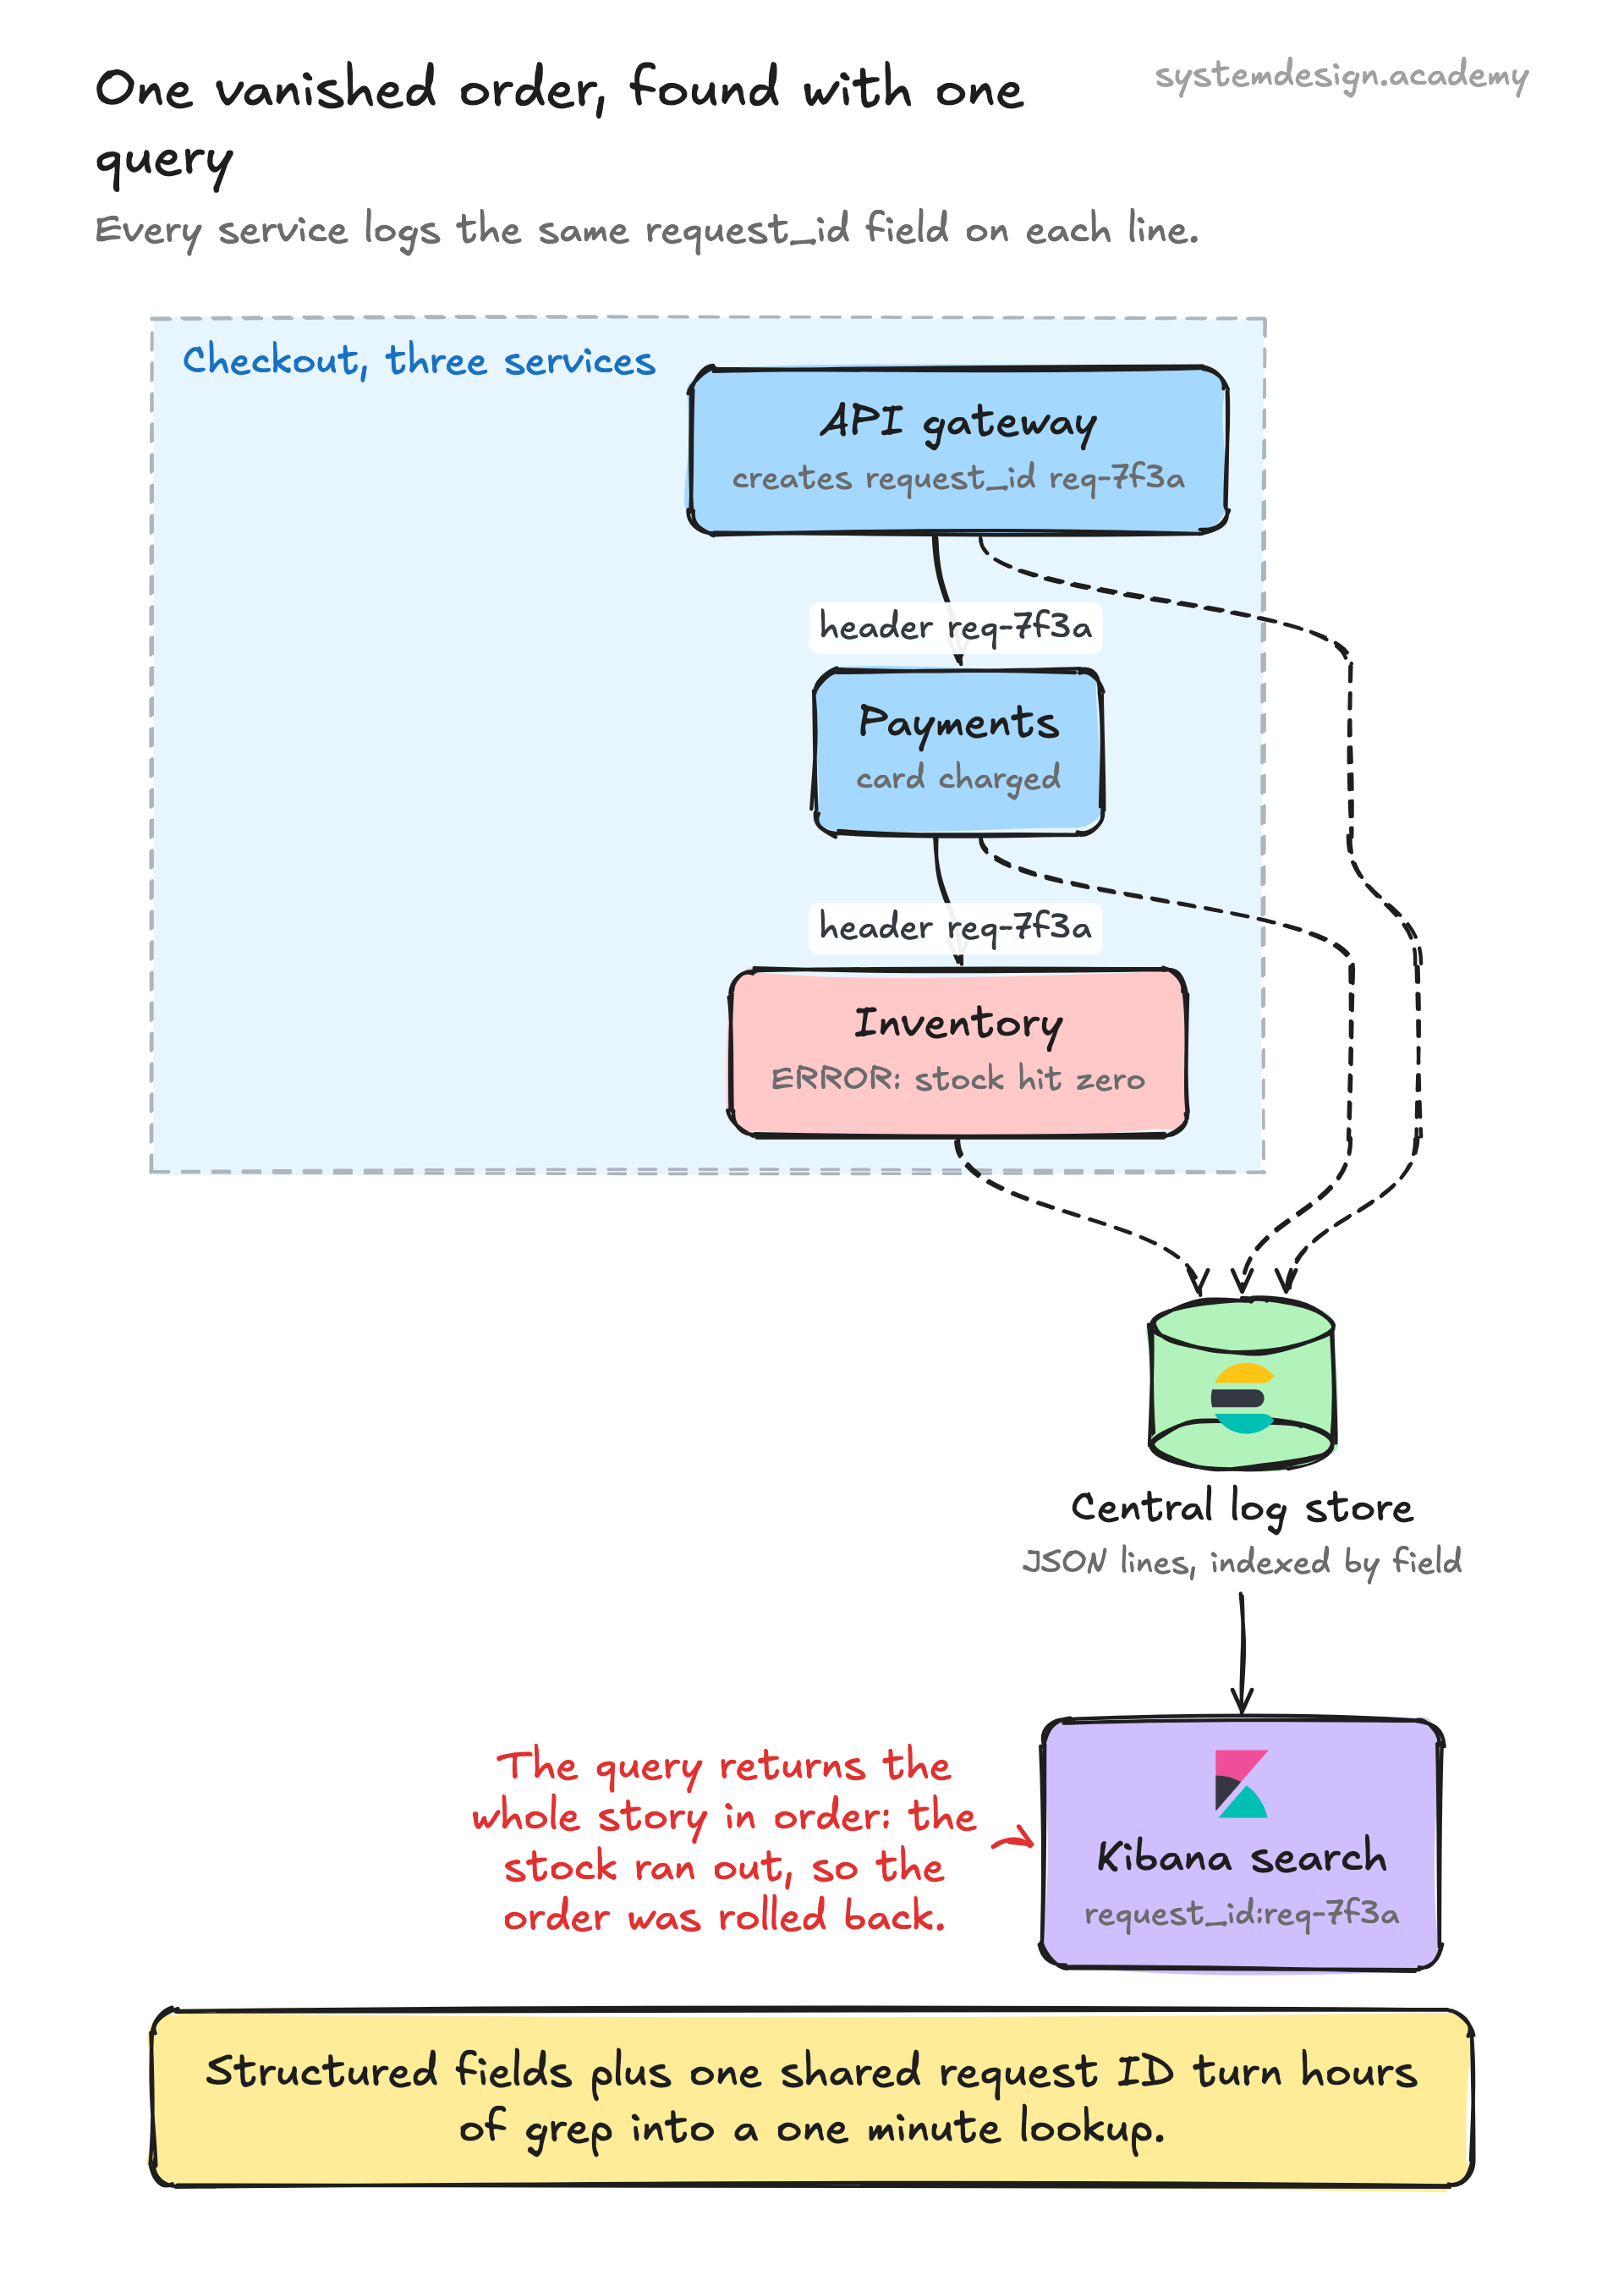
Application code calls a logging library such as Logback or SLF4J in Java, Winston or Pino in Node.js, or the standard logging module in Python. The library formats the event, attaches the severity and timestamp, and writes it to a destination. In containers the destination is almost always stdout, which the platform captures.
A log shipper or agent then collects those lines and forwards them. Fluent Bit, Filebeat, Vector, and the OpenTelemetry Collector are common agents. They tail files or read the container runtime stream, parse and enrich the events, batch them, and send them over the network to a central store. This decouples the app from the storage so a slow backend never blocks the request path.
The central system indexes the logs for search and retention. Elasticsearch with Kibana, Loki with Grafana, Splunk, and managed services like Datadog or CloudWatch Logs all do this. Because volume is enormous, teams set log levels per service, sample high frequency events, and apply retention windows such as 7 days hot and 90 days in cold storage to control cost. A single busy service can produce gigabytes per hour.