Regular TLS, the thing behind HTTPS, only authenticates one side. When your browser connects to a bank, the bank presents a certificate that proves it is really that bank, but the bank has no cryptographic proof of who you are. You log in with a password later, at the application layer. mTLS pushes identity down to the transport layer for both parties.
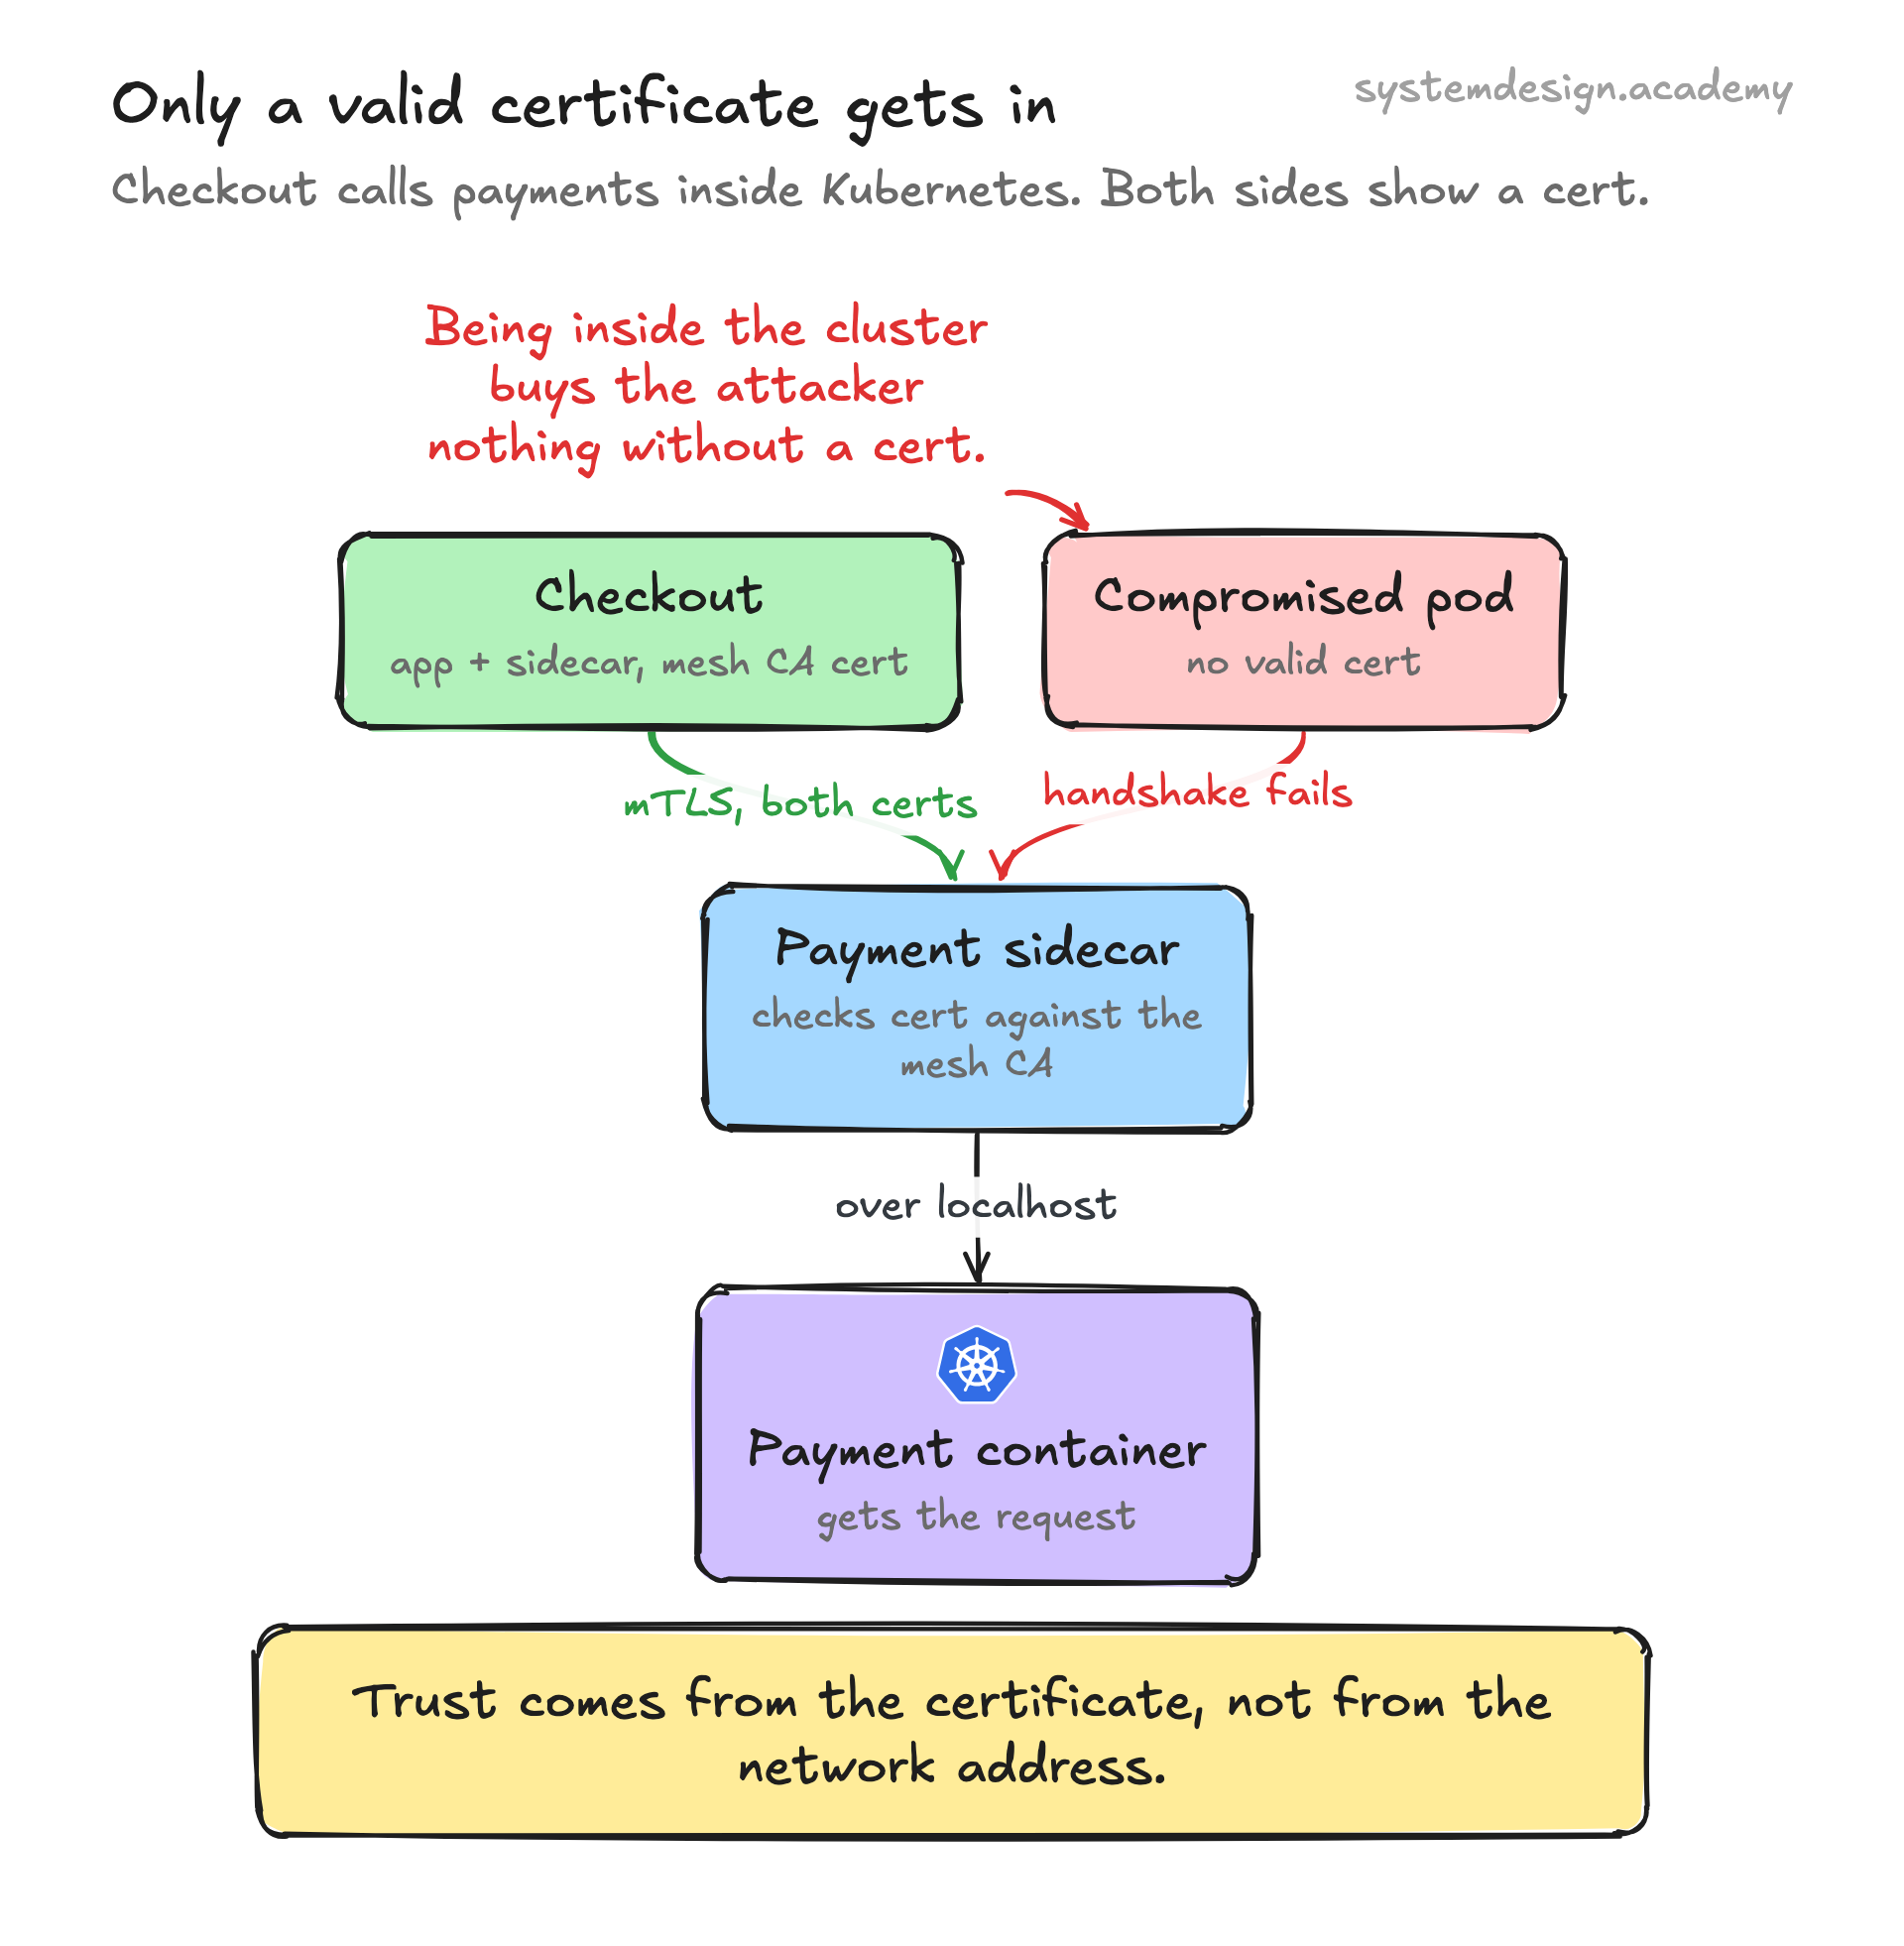
In mTLS, the server still presents its certificate, and on top of that it demands one from the client. The client sends its own X.509 certificate, and the server checks that the certificate is signed by a certificate authority it trusts, that it has not expired, and that it has not been revoked. Both sides walk away with proof of who they are talking to before a single byte of application data flows.
The key idea is that identity becomes the certificate, not the network location. A service is trusted because it holds a valid cert issued by your internal CA, not because it happens to have an IP address inside the VPC. That is the foundation of zero-trust networking.