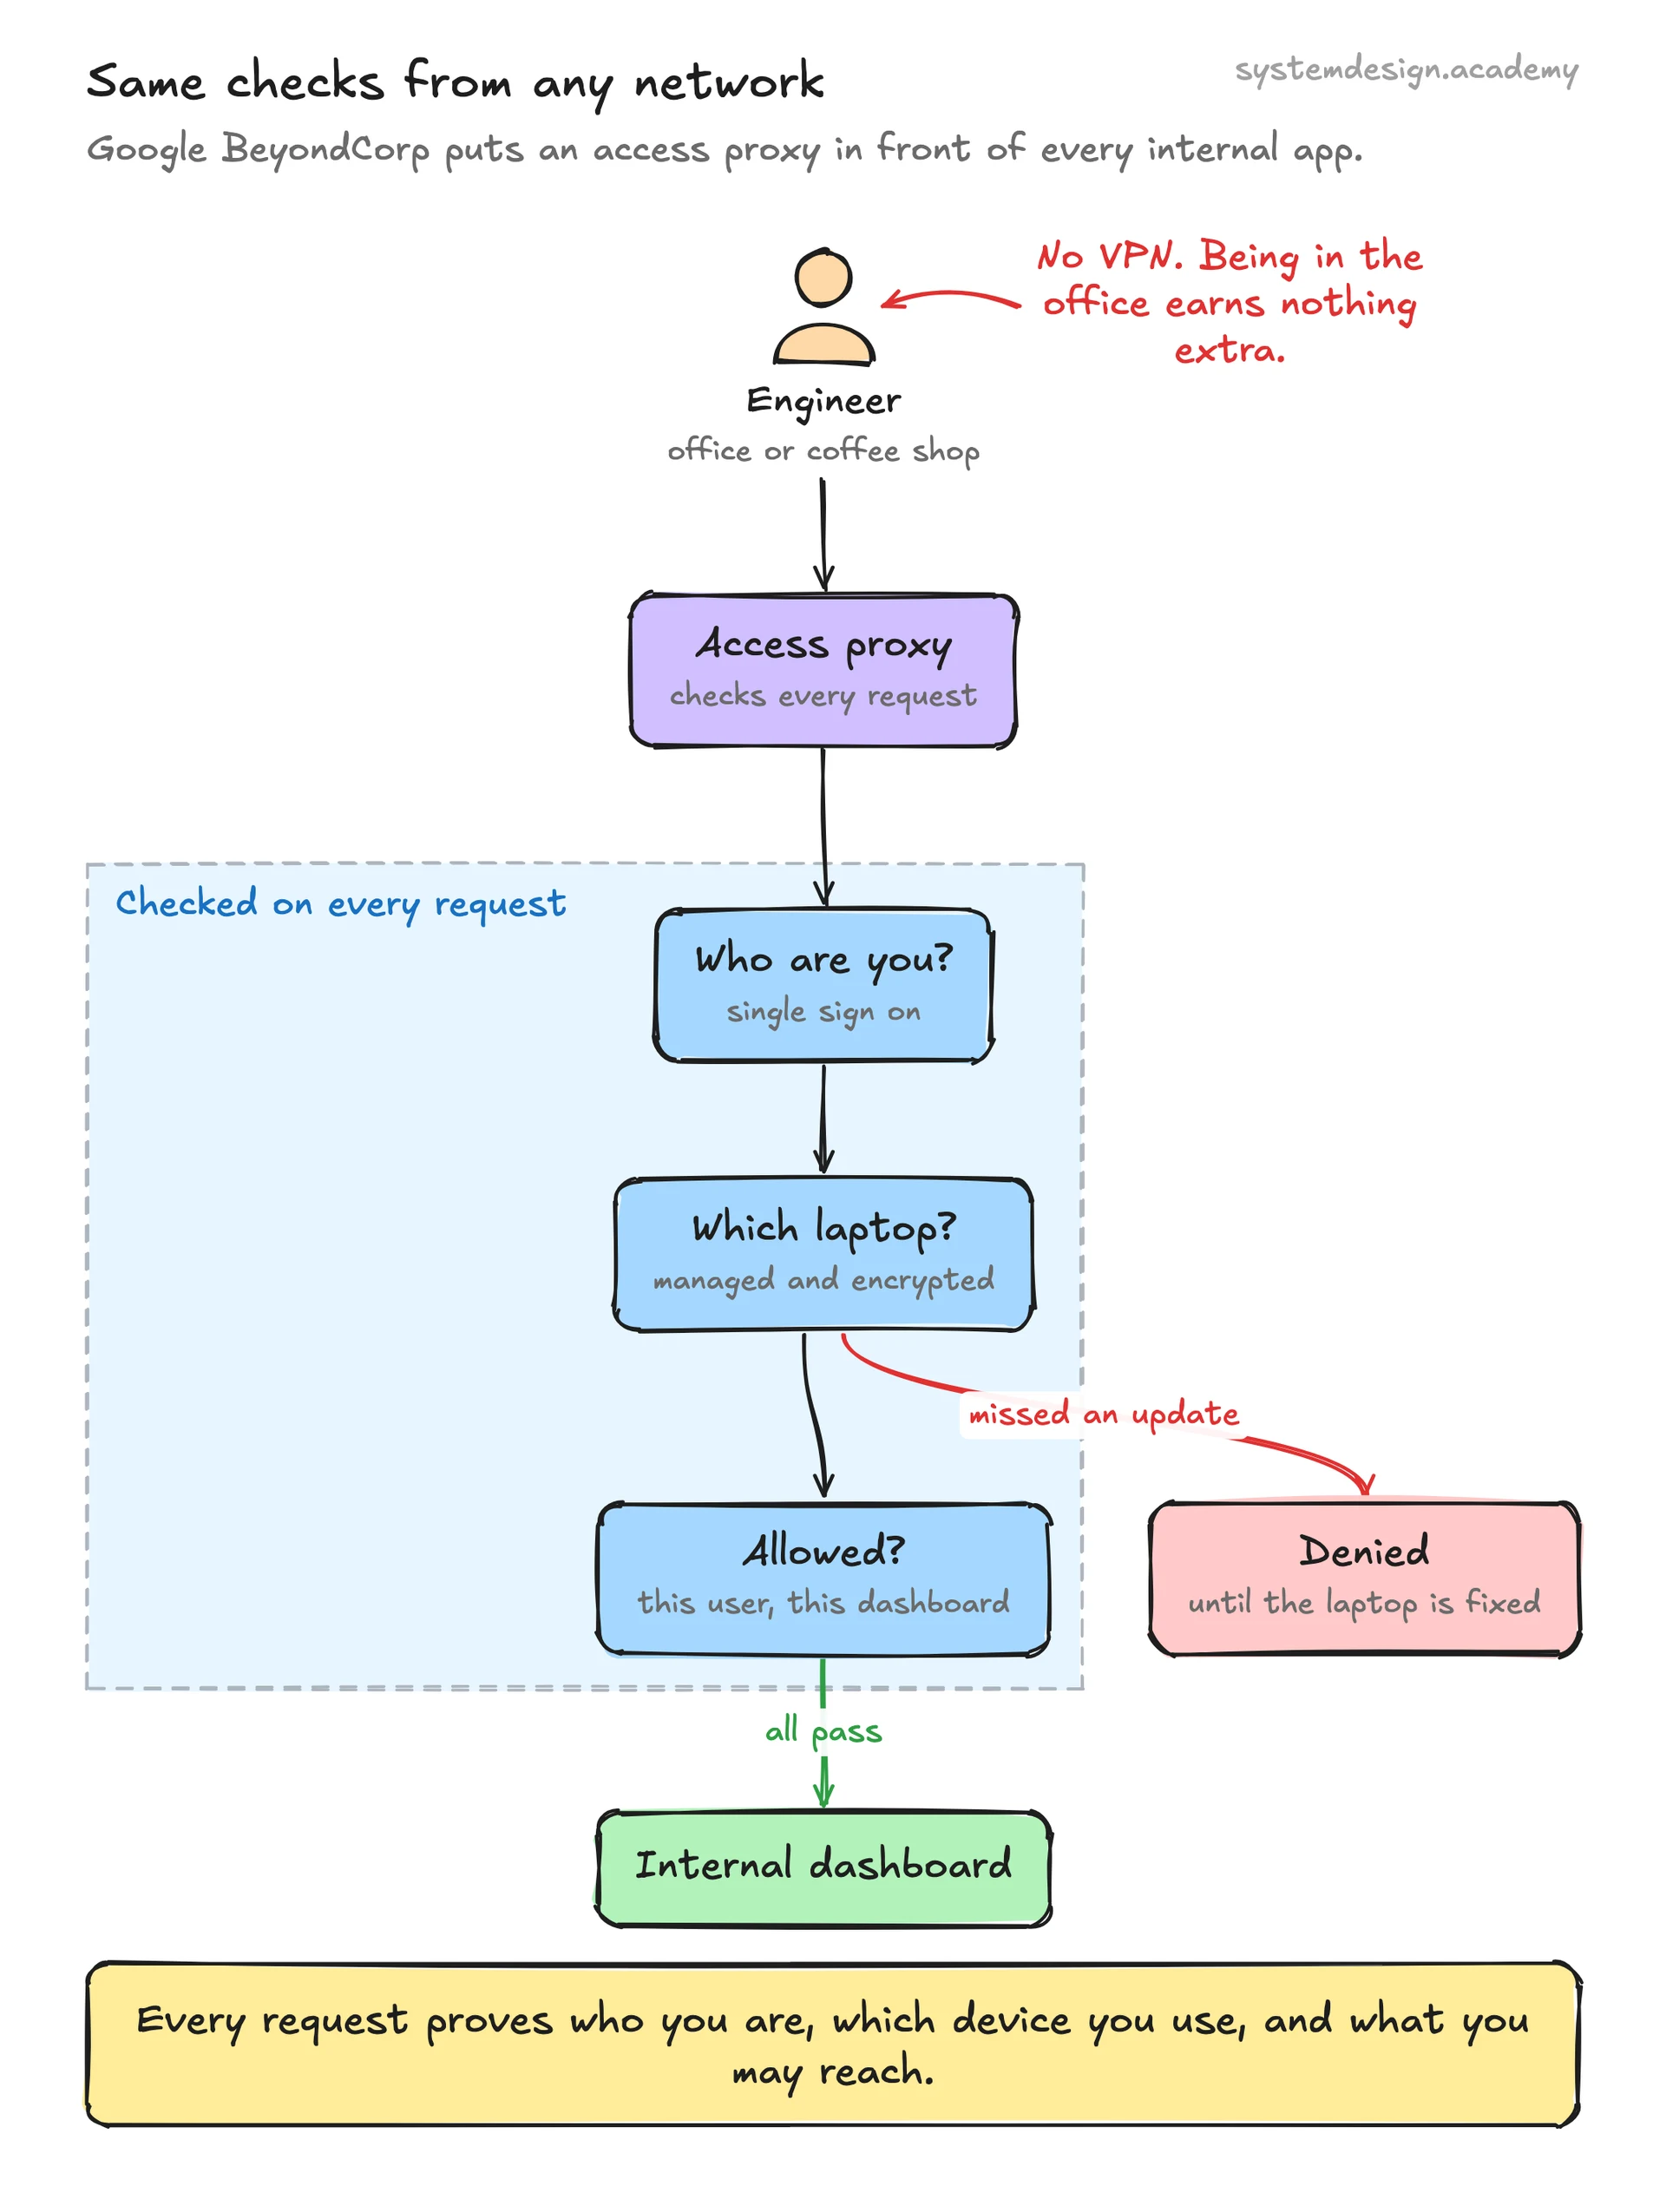
The old model was a hard shell with a soft center. You built a firewall around the corporate network, and once a request got inside, it was treated as friendly. Anyone on the office VPN could reach internal databases, admin panels, and other servers with little extra checking. That perimeter approach falls apart the moment an attacker gets a foothold, because one stolen laptop or one compromised server gives them free movement across everything inside the wall.
Zero Trust throws out the idea that the network location tells you anything about trust. A request from a laptop in the office and a request from a random IP on the internet get the same scrutiny. The guiding phrase is never trust, always verify. Identity, device health, and context decide access, not which subnet you happen to be on.
The term was popularized by Forrester analyst John Kindervag around 2010, and the US government formalized it in NIST Special Publication 800-207. Google built one of the first large production versions, called BeyondCorp, after the 2009 Aurora attacks showed how dangerous flat internal trust can be.