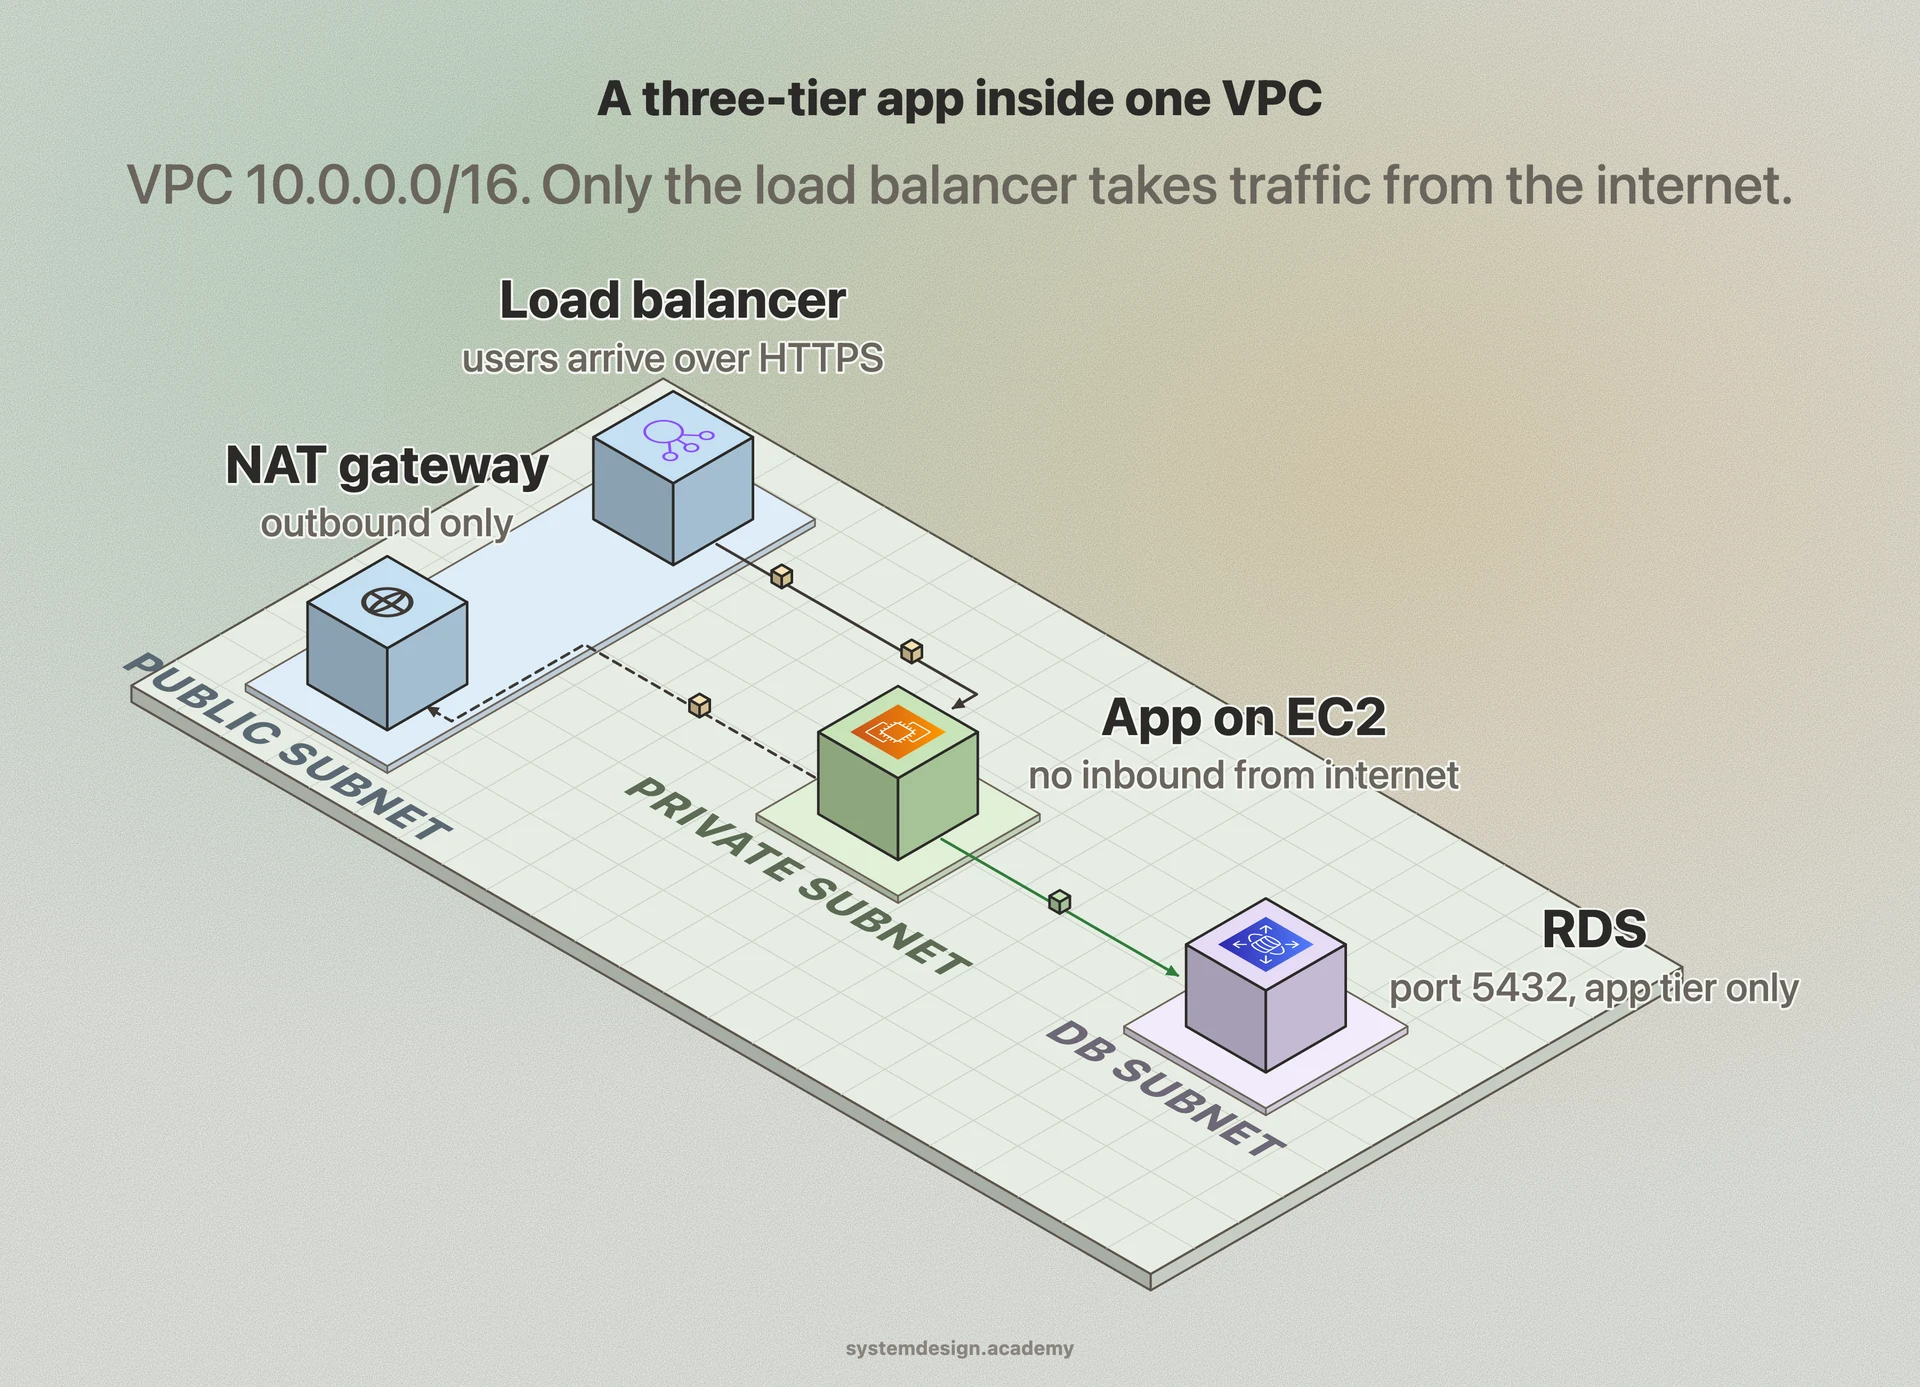
You get a default VPC the moment you create a cloud account, so the real question is how much you customize. For a hobby project a single public subnet is fine. For anything handling real user data or money, you separate tiers: load balancers in public subnets, application servers and databases in private subnets with no internet route, and tightly scoped security groups between them. This is how you keep a database off the public internet, which removes an entire class of attacks.
The cost is complexity. CIDR ranges are hard to change after the fact, so picking 10.0.0.0/16 versus 10.0.0.0/24 up front matters; too small and you run out of IPs, too overlapping and you cannot peer with another network later. NAT gateways are not free either, often costing a few cents per gigabyte processed plus an hourly charge, which surprises teams that route all private traffic through one.
The main trade-off is isolation versus reachability. The more locked down the VPC, the more deliberate plumbing (peering, endpoints, bastion hosts, VPNs) you need to let legitimate traffic through. Most outages in cloud networking come from a missing route or an over-tight security group, not from the VPC concept itself.