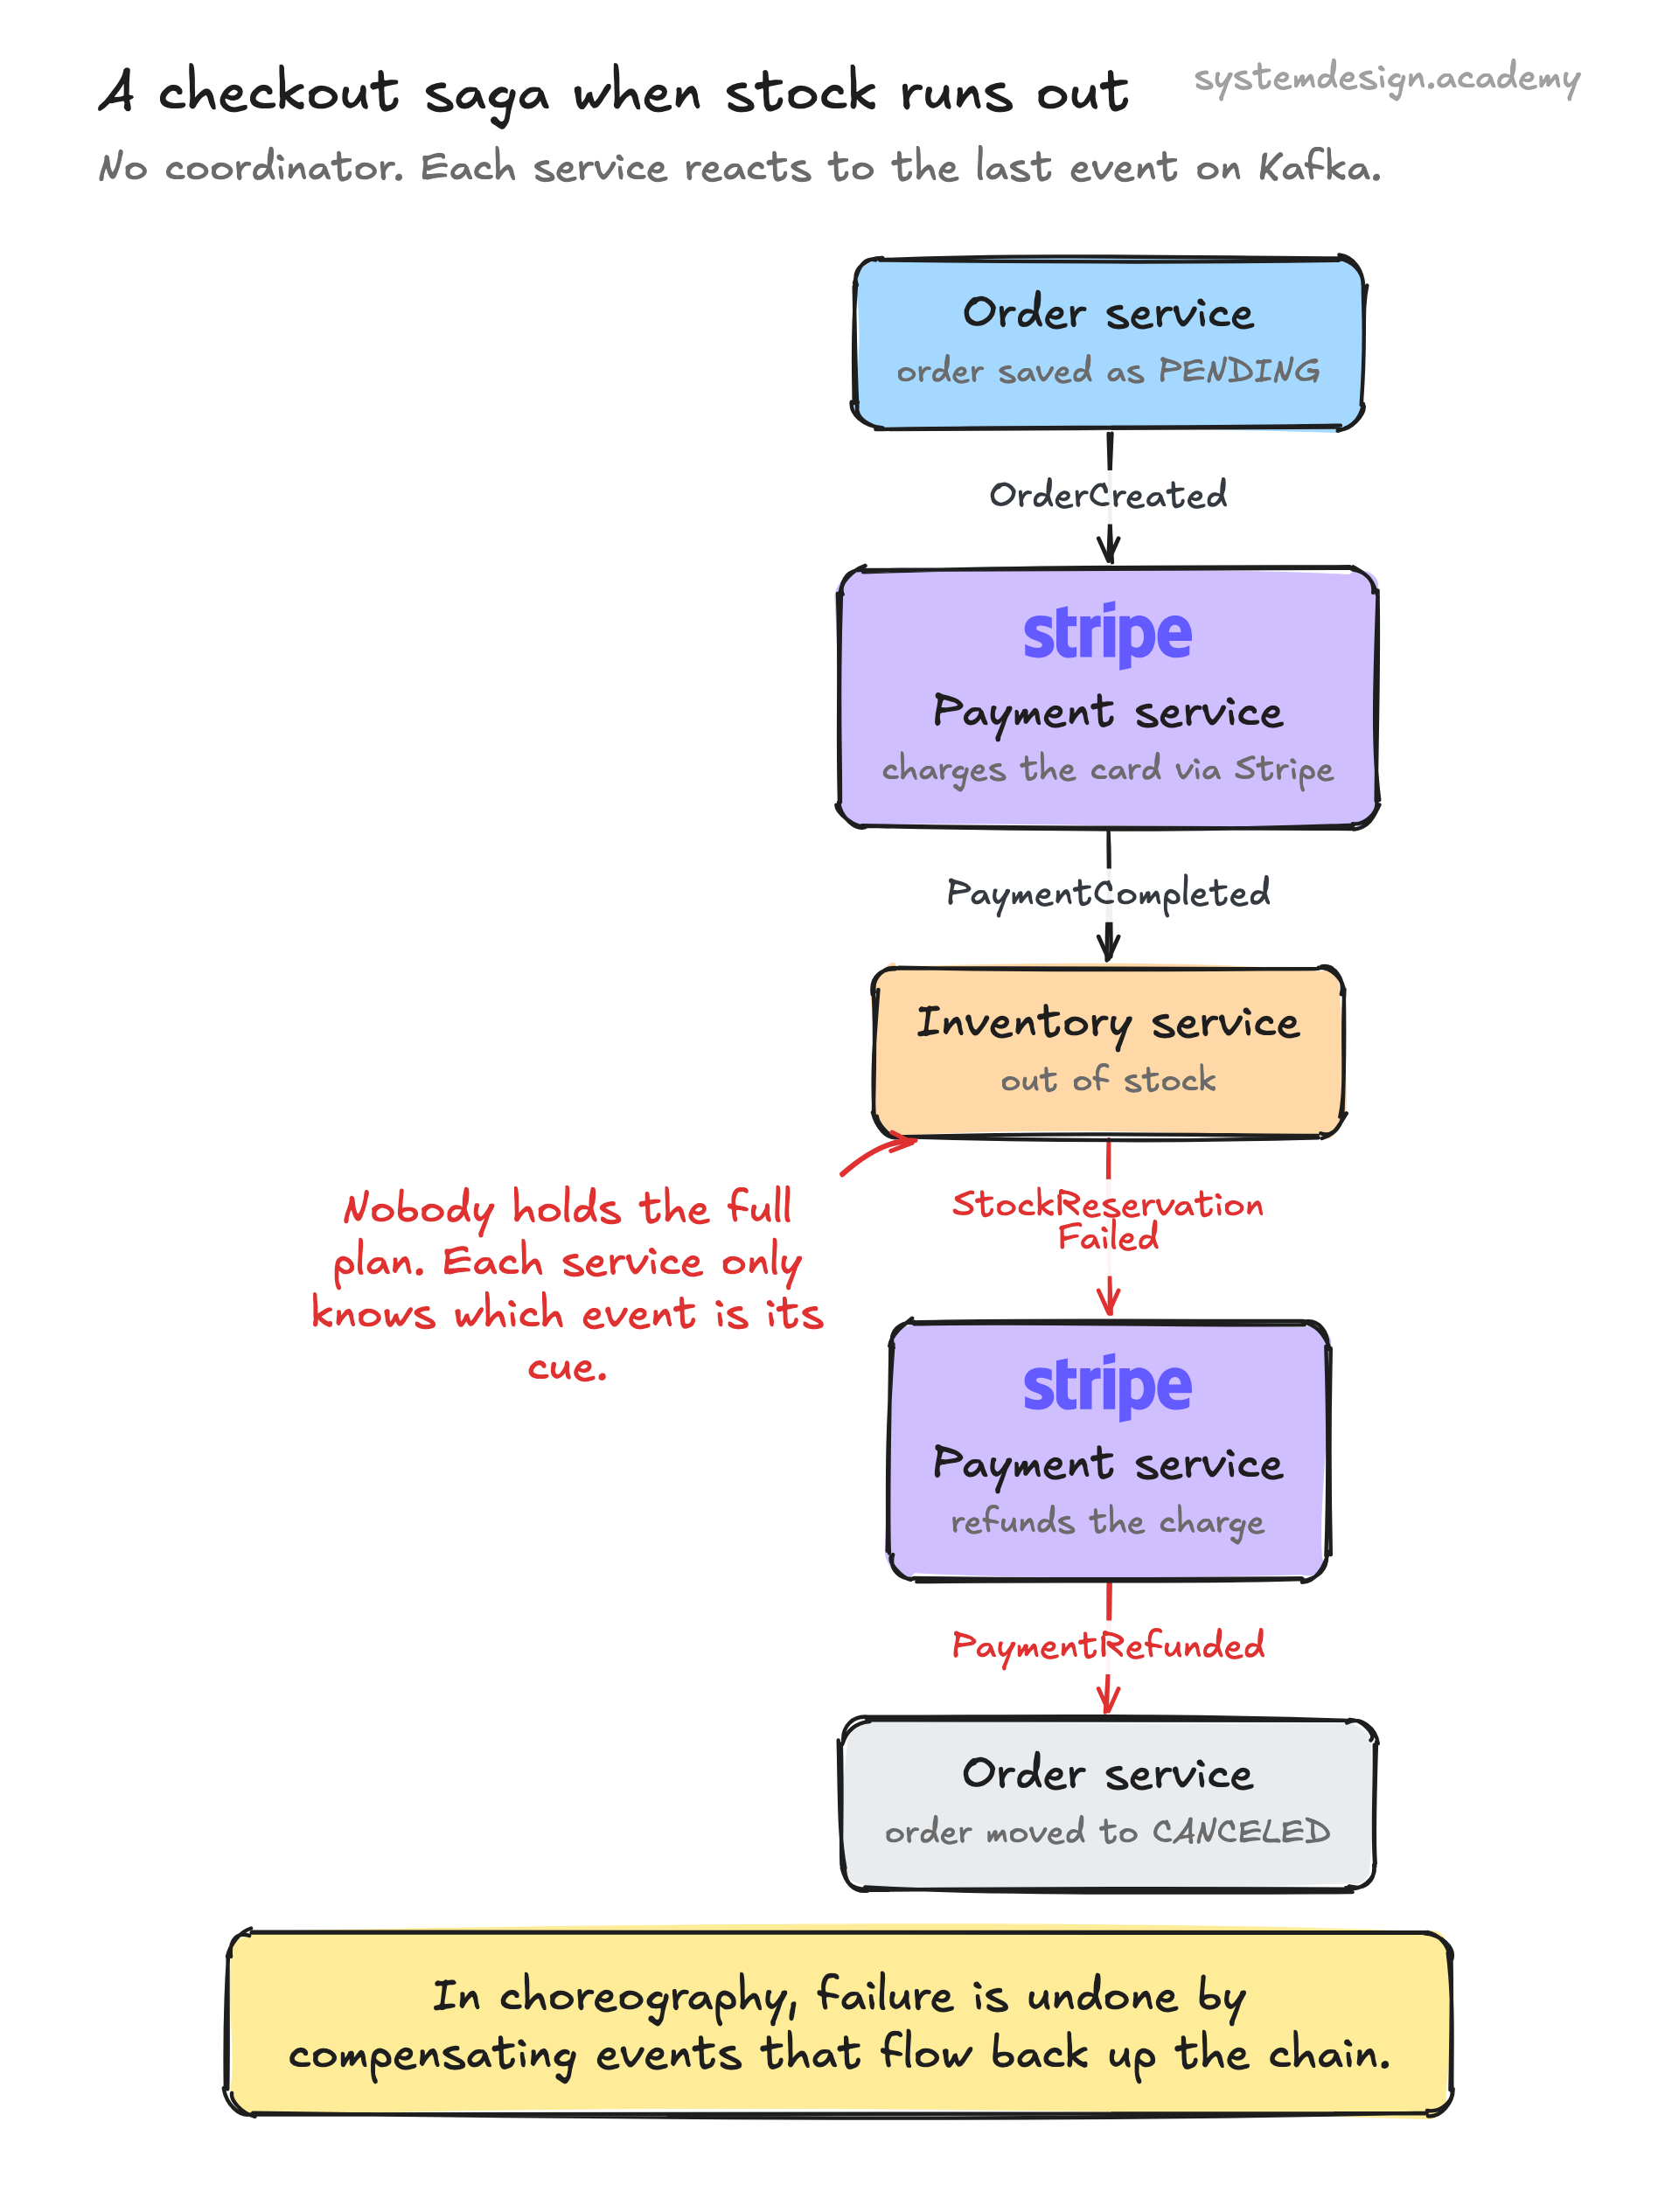
It runs on an event broker such as Kafka, RabbitMQ, or AWS SNS plus SQS. The first service commits its local transaction and publishes a domain event, for example OrderCreated. Payments subscribes to OrderCreated, charges the card, and publishes PaymentCompleted. Inventory subscribes to PaymentCompleted, reserves stock, and publishes StockReserved, and so on down the chain.
Failures are handled by compensating events flowing backward. If Inventory cannot reserve stock it publishes StockReservationFailed. Payments subscribes to that and issues a refund, then publishes PaymentRefunded, which the Orders service uses to mark the order canceled. Each service owns both its forward action and its undo action.
Two properties make this safe in practice. Events must be delivered reliably, usually with the transactional outbox pattern so the database write and the event publish cannot diverge. And every handler must be idempotent, because at-least-once brokers will redeliver, so charging the same OrderCreated twice has to be a no-op the second time. Correlation IDs on every event let you stitch the steps back together for debugging.