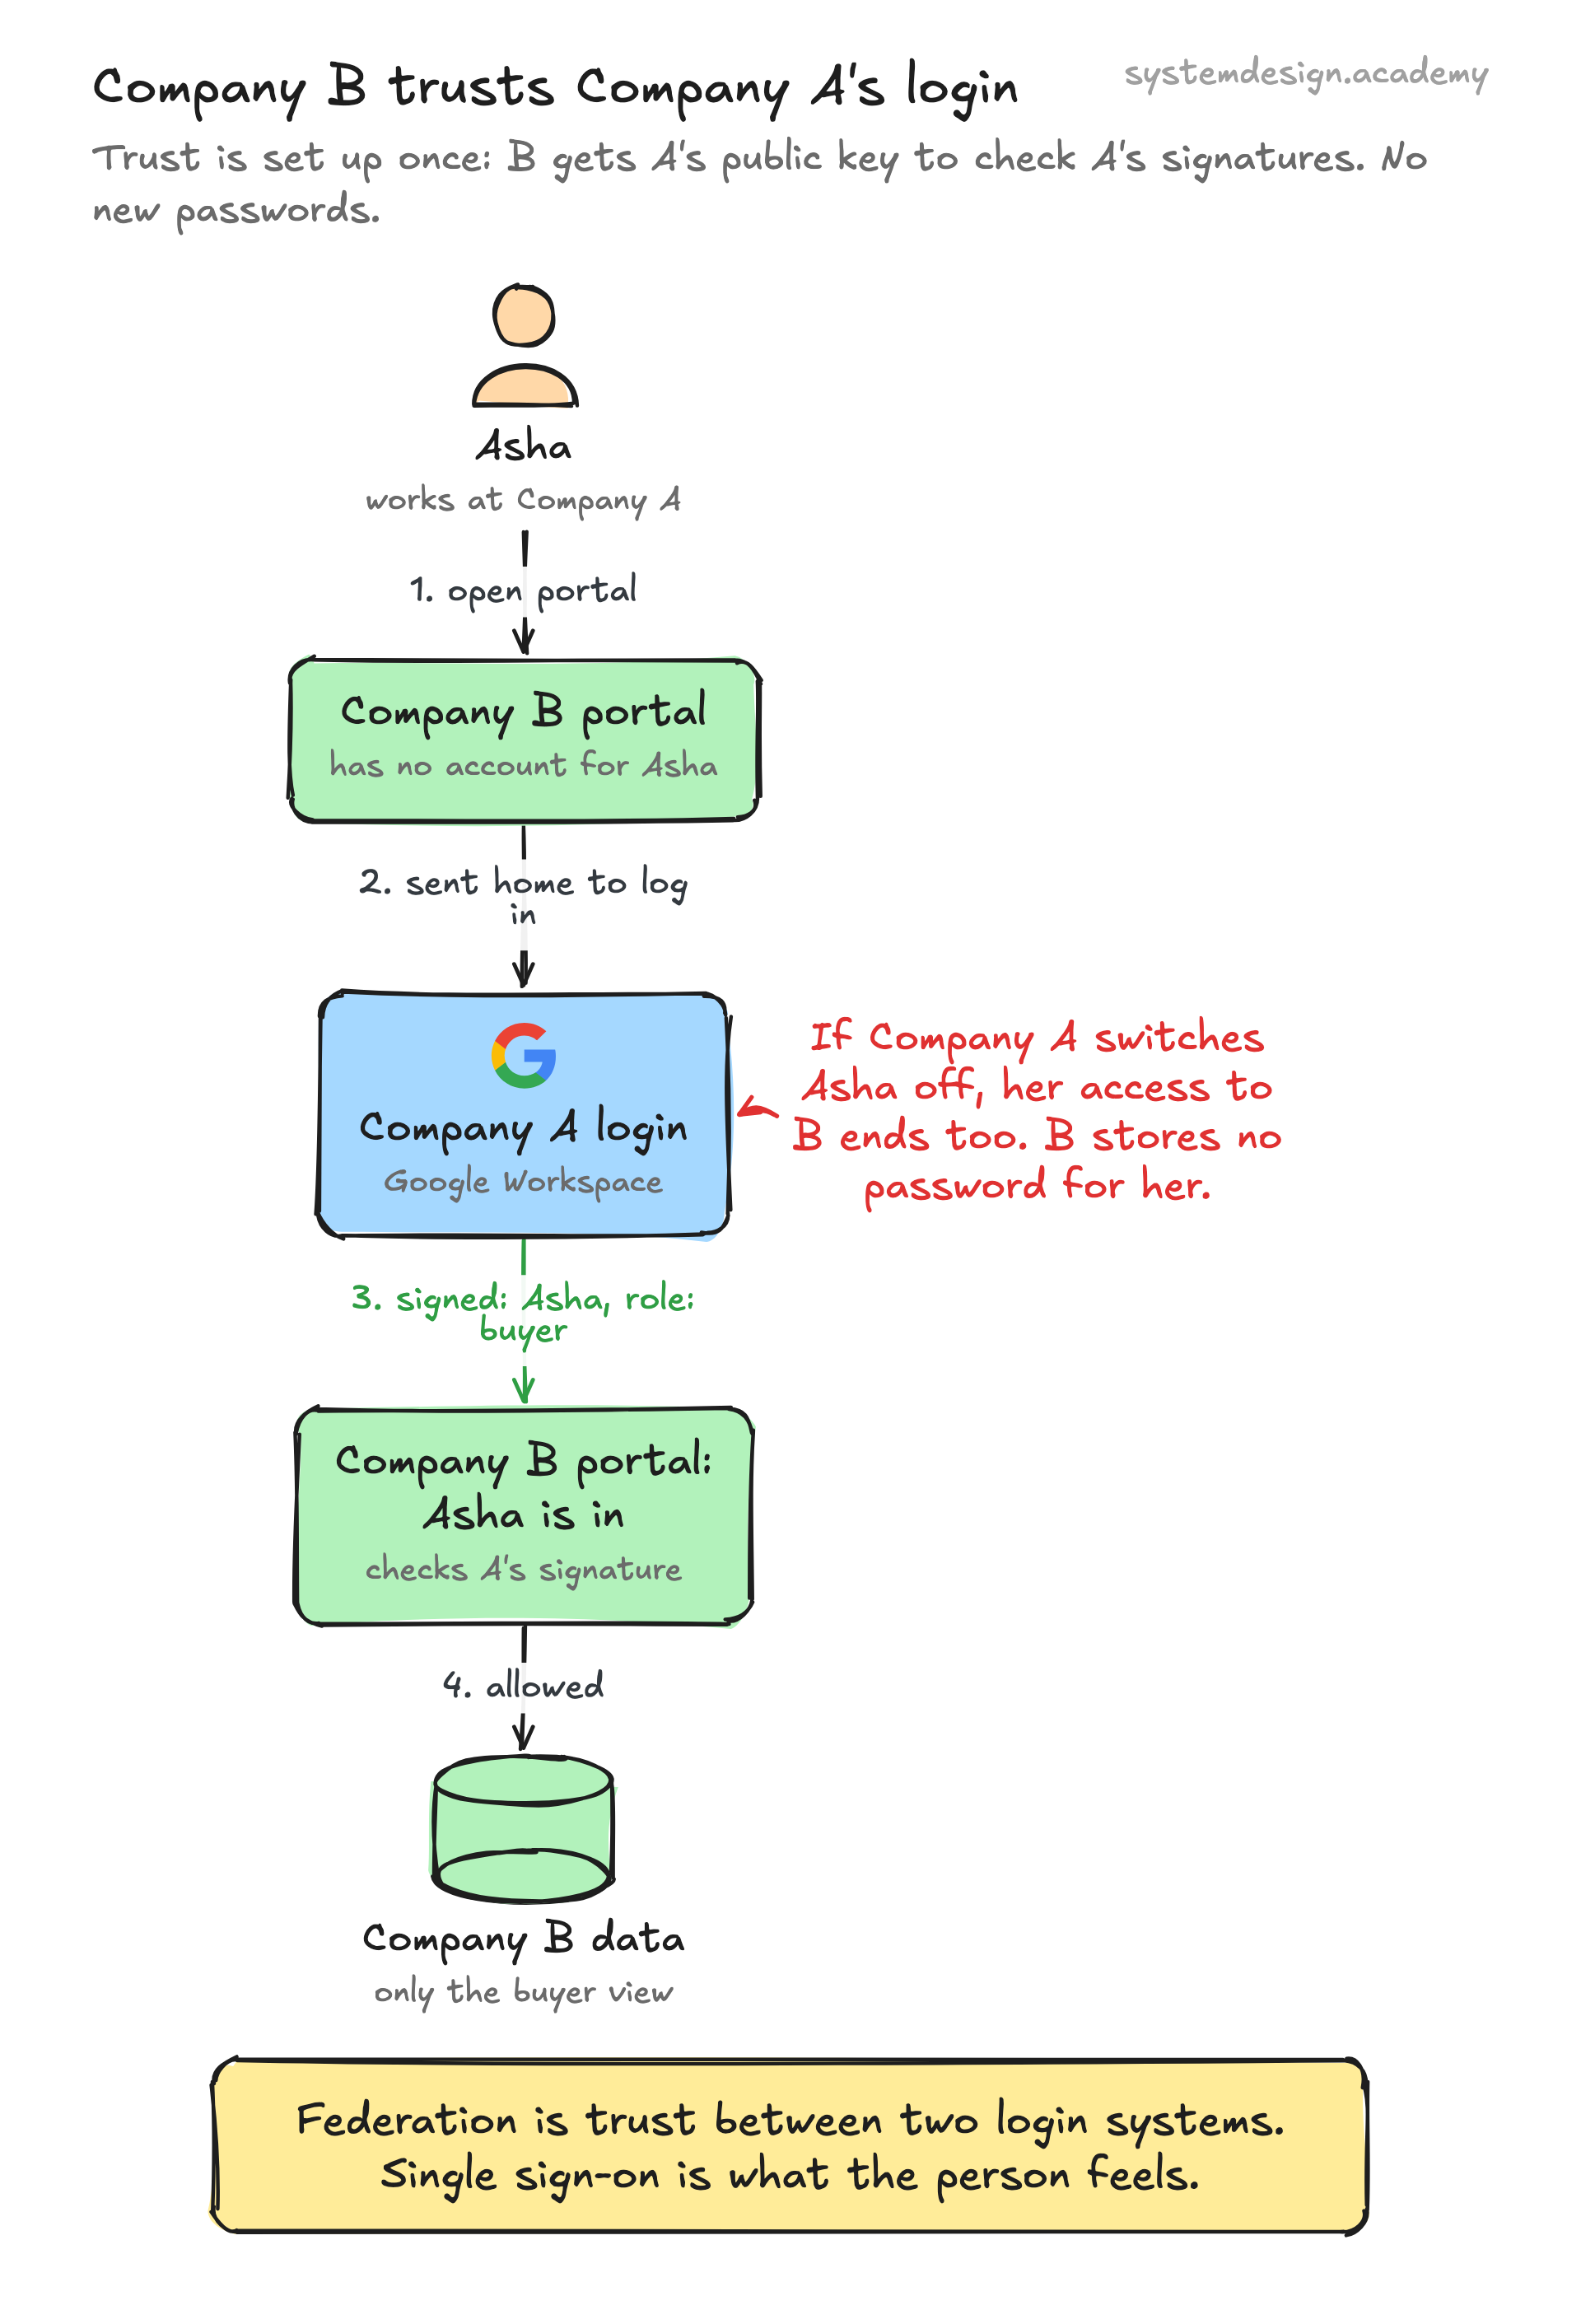
Think of a passport. You get it from your own country. When you land in another country, they do not make you a new identity card. They check that the passport is real, because the two countries agreed to trust each other's passports. Federation is that agreement, for logins.
Every login system is an identity domain: a place that knows a set of people or programs and can prove who they are. Your company's login (an identity provider, or IdP) is one domain. AWS is another. A partner company's portal is a third.
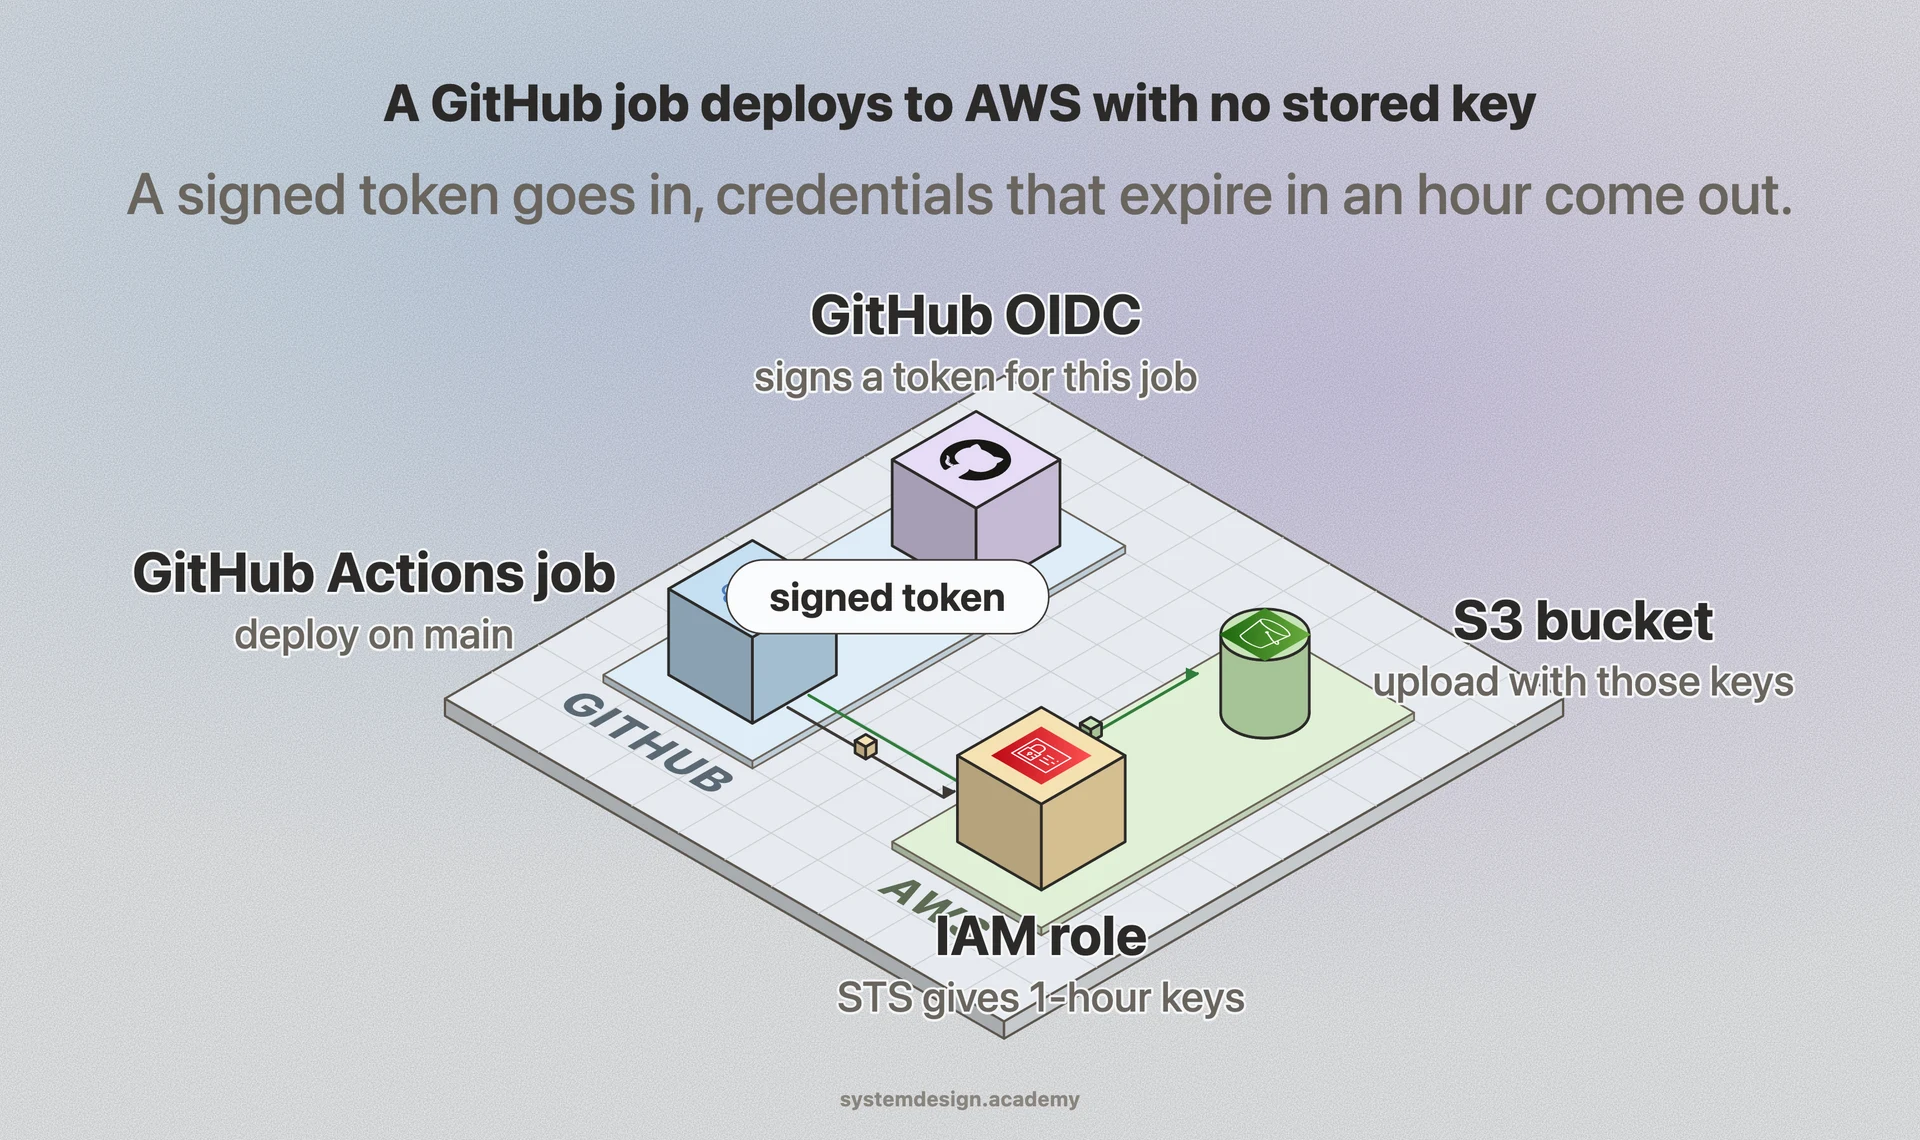
Without federation, each domain needs its own account for you, with its own password. With federation, the systems set up trust once. The trusting system gets the identity provider's public key, the half of a key pair that anyone may see, so it can check that provider's signatures. Only the provider holds the private half, so only it can sign. After that, your home IdP signs a short message that says who you are, and the other system checks the signature and lets you in.