Think of a restaurant. The chef is careful, the kitchen is clean, but one supplier's flour is contaminated. Every dish made with it is bad, and the chef did nothing wrong. Software works the same way.
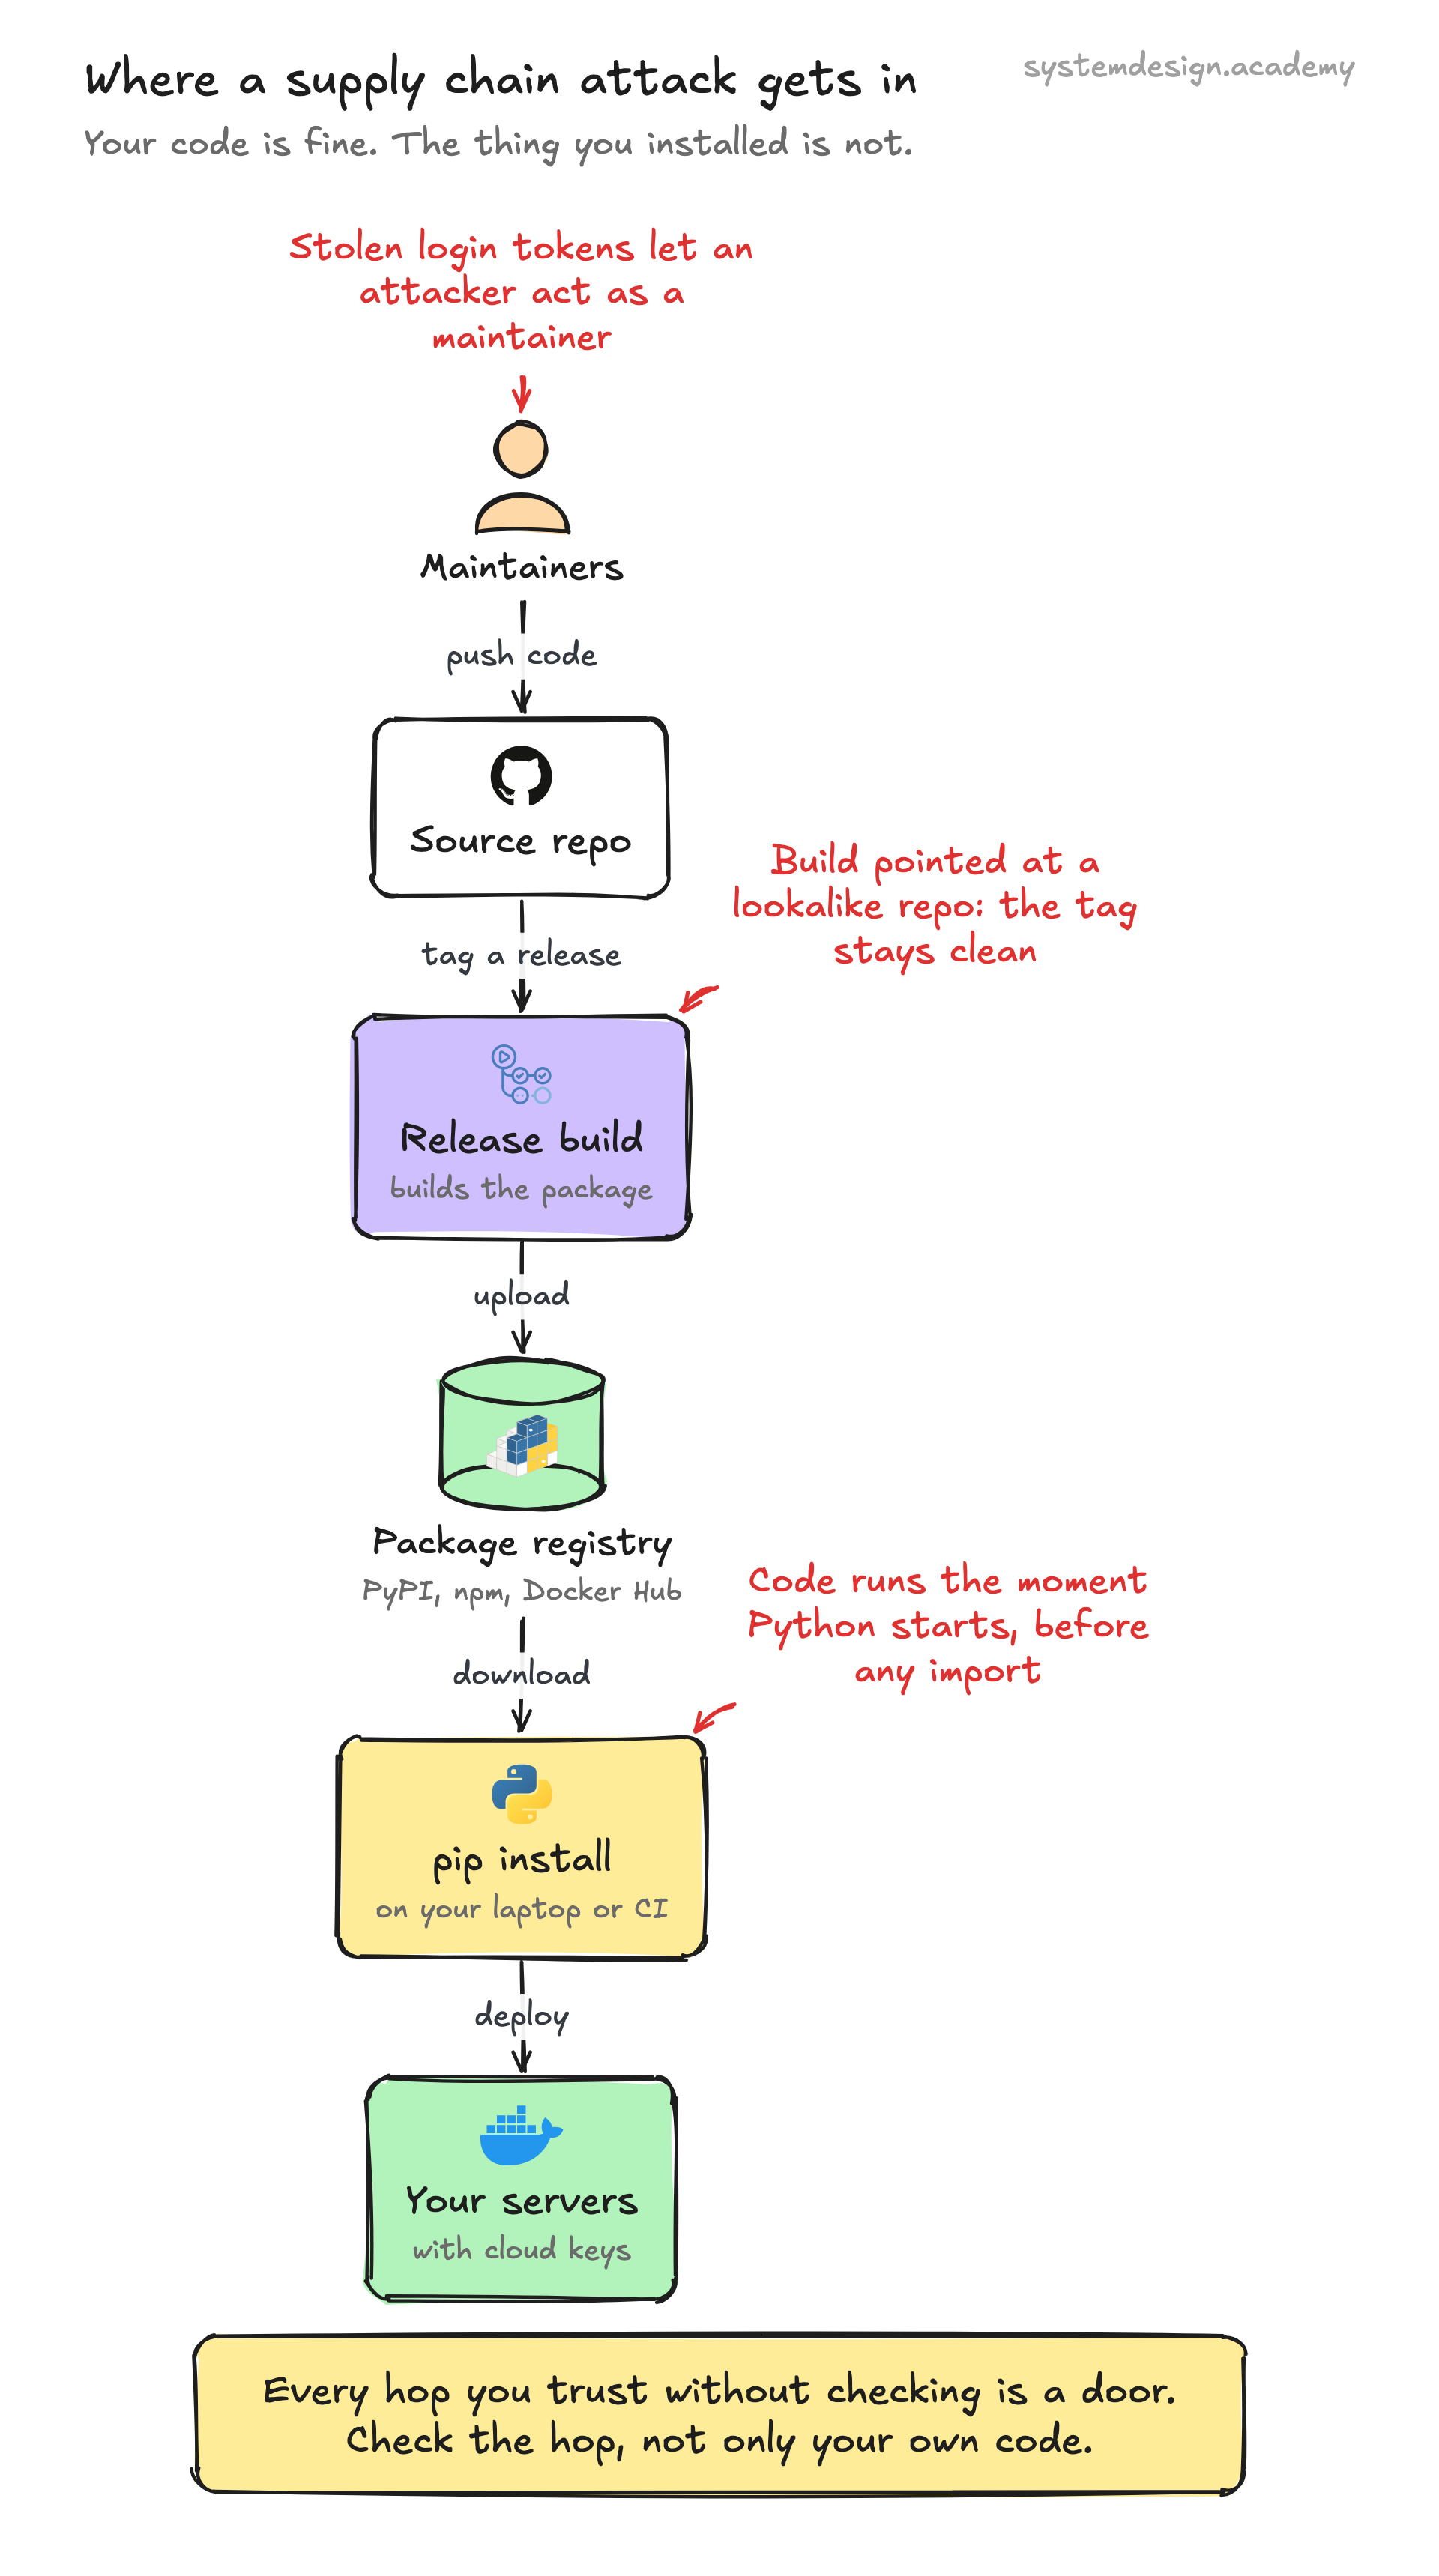
Your app is built from your own code plus hundreds of pieces you did not write: open-source packages, a base container image, build tools, CI actions. CI (continuous integration) is the automated system that builds and tests your code. Each of these comes to you through a chain of people and machines: the maintainers who write it, the source repository, the release build, and the registry you download from, such as PyPI for Python, npm for JavaScript or Docker Hub for images.
A supply chain attack breaks into one link of that chain. Everyone downstream then installs the bad version in good faith.