
Did Lovable apps leak user data?
“We found many clear examples of sensitive data left unprotected.”
Many did expose it, according to a study by Crissy Field, a security firm in Hamburg, carried out with the German business paper Handelsblatt. Handelsblatt first reported it on 2 November 2026, and the firm's English report, with newer figures, was widely shared on 14 November. Lovable is an AI app builder: you describe the app you want in plain words and it writes and hosts the app for you.
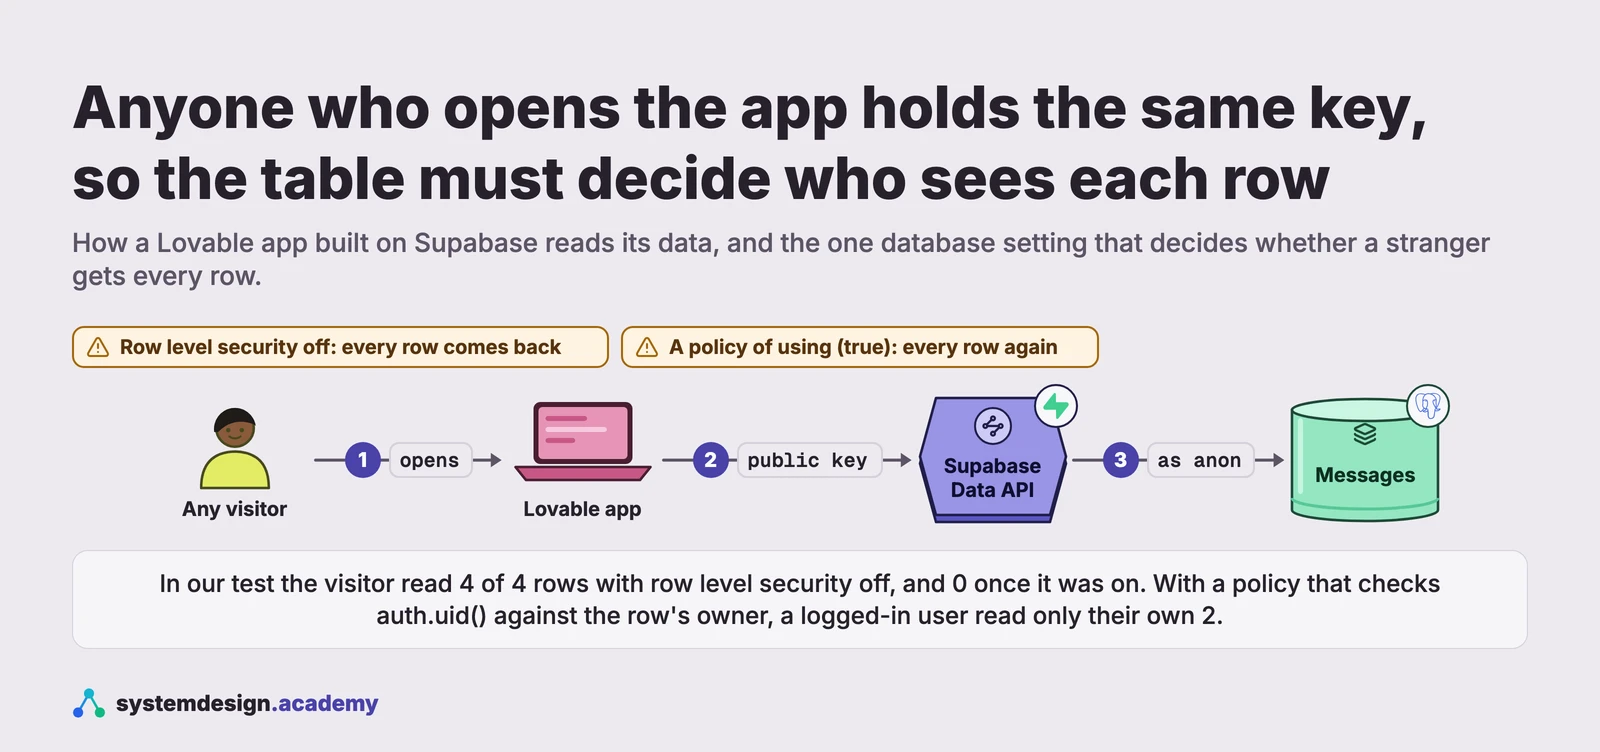
The researchers took Lovable projects from Common Crawl, a public archive of the web, from December 2025 to September 2026. That gave them 159,041 projects. They focused on the 34,545 that used Supabase, a hosted Postgres database that many Lovable apps are built on. They did not examine Lovable's own database feature, which arrived in late 2025.
Of those, 24,664 websites sent records from their database as soon as the page loaded, without anyone logging in. The researchers are careful here: data sent on load is not a problem in itself, because some of it is meant to be public, like a list of products. So they looked for records with email addresses, and found them in 10,560 tables across 7,403 sites, which is 30%. They also made further read-only requests with the same key the page used, and that is where the worst examples came from.
