What happened
“Historically Claude Code has not done secret scrubbing (there are many good tools for that), but we are looking into what we can do to prevent this.”
On 5 November 2026 Apiiro, a company that sells application security tools, published research called "Coding Agents Copy Your Secrets to a Hidden File. Thousands Are on GitHub". It was posted to Hacker News on 7 November as "Claude Code's 'Don't Ask Again' exposes passwords in 1,122 public GitHub files", and had 266 points and 172 comments by the morning of 8 November.
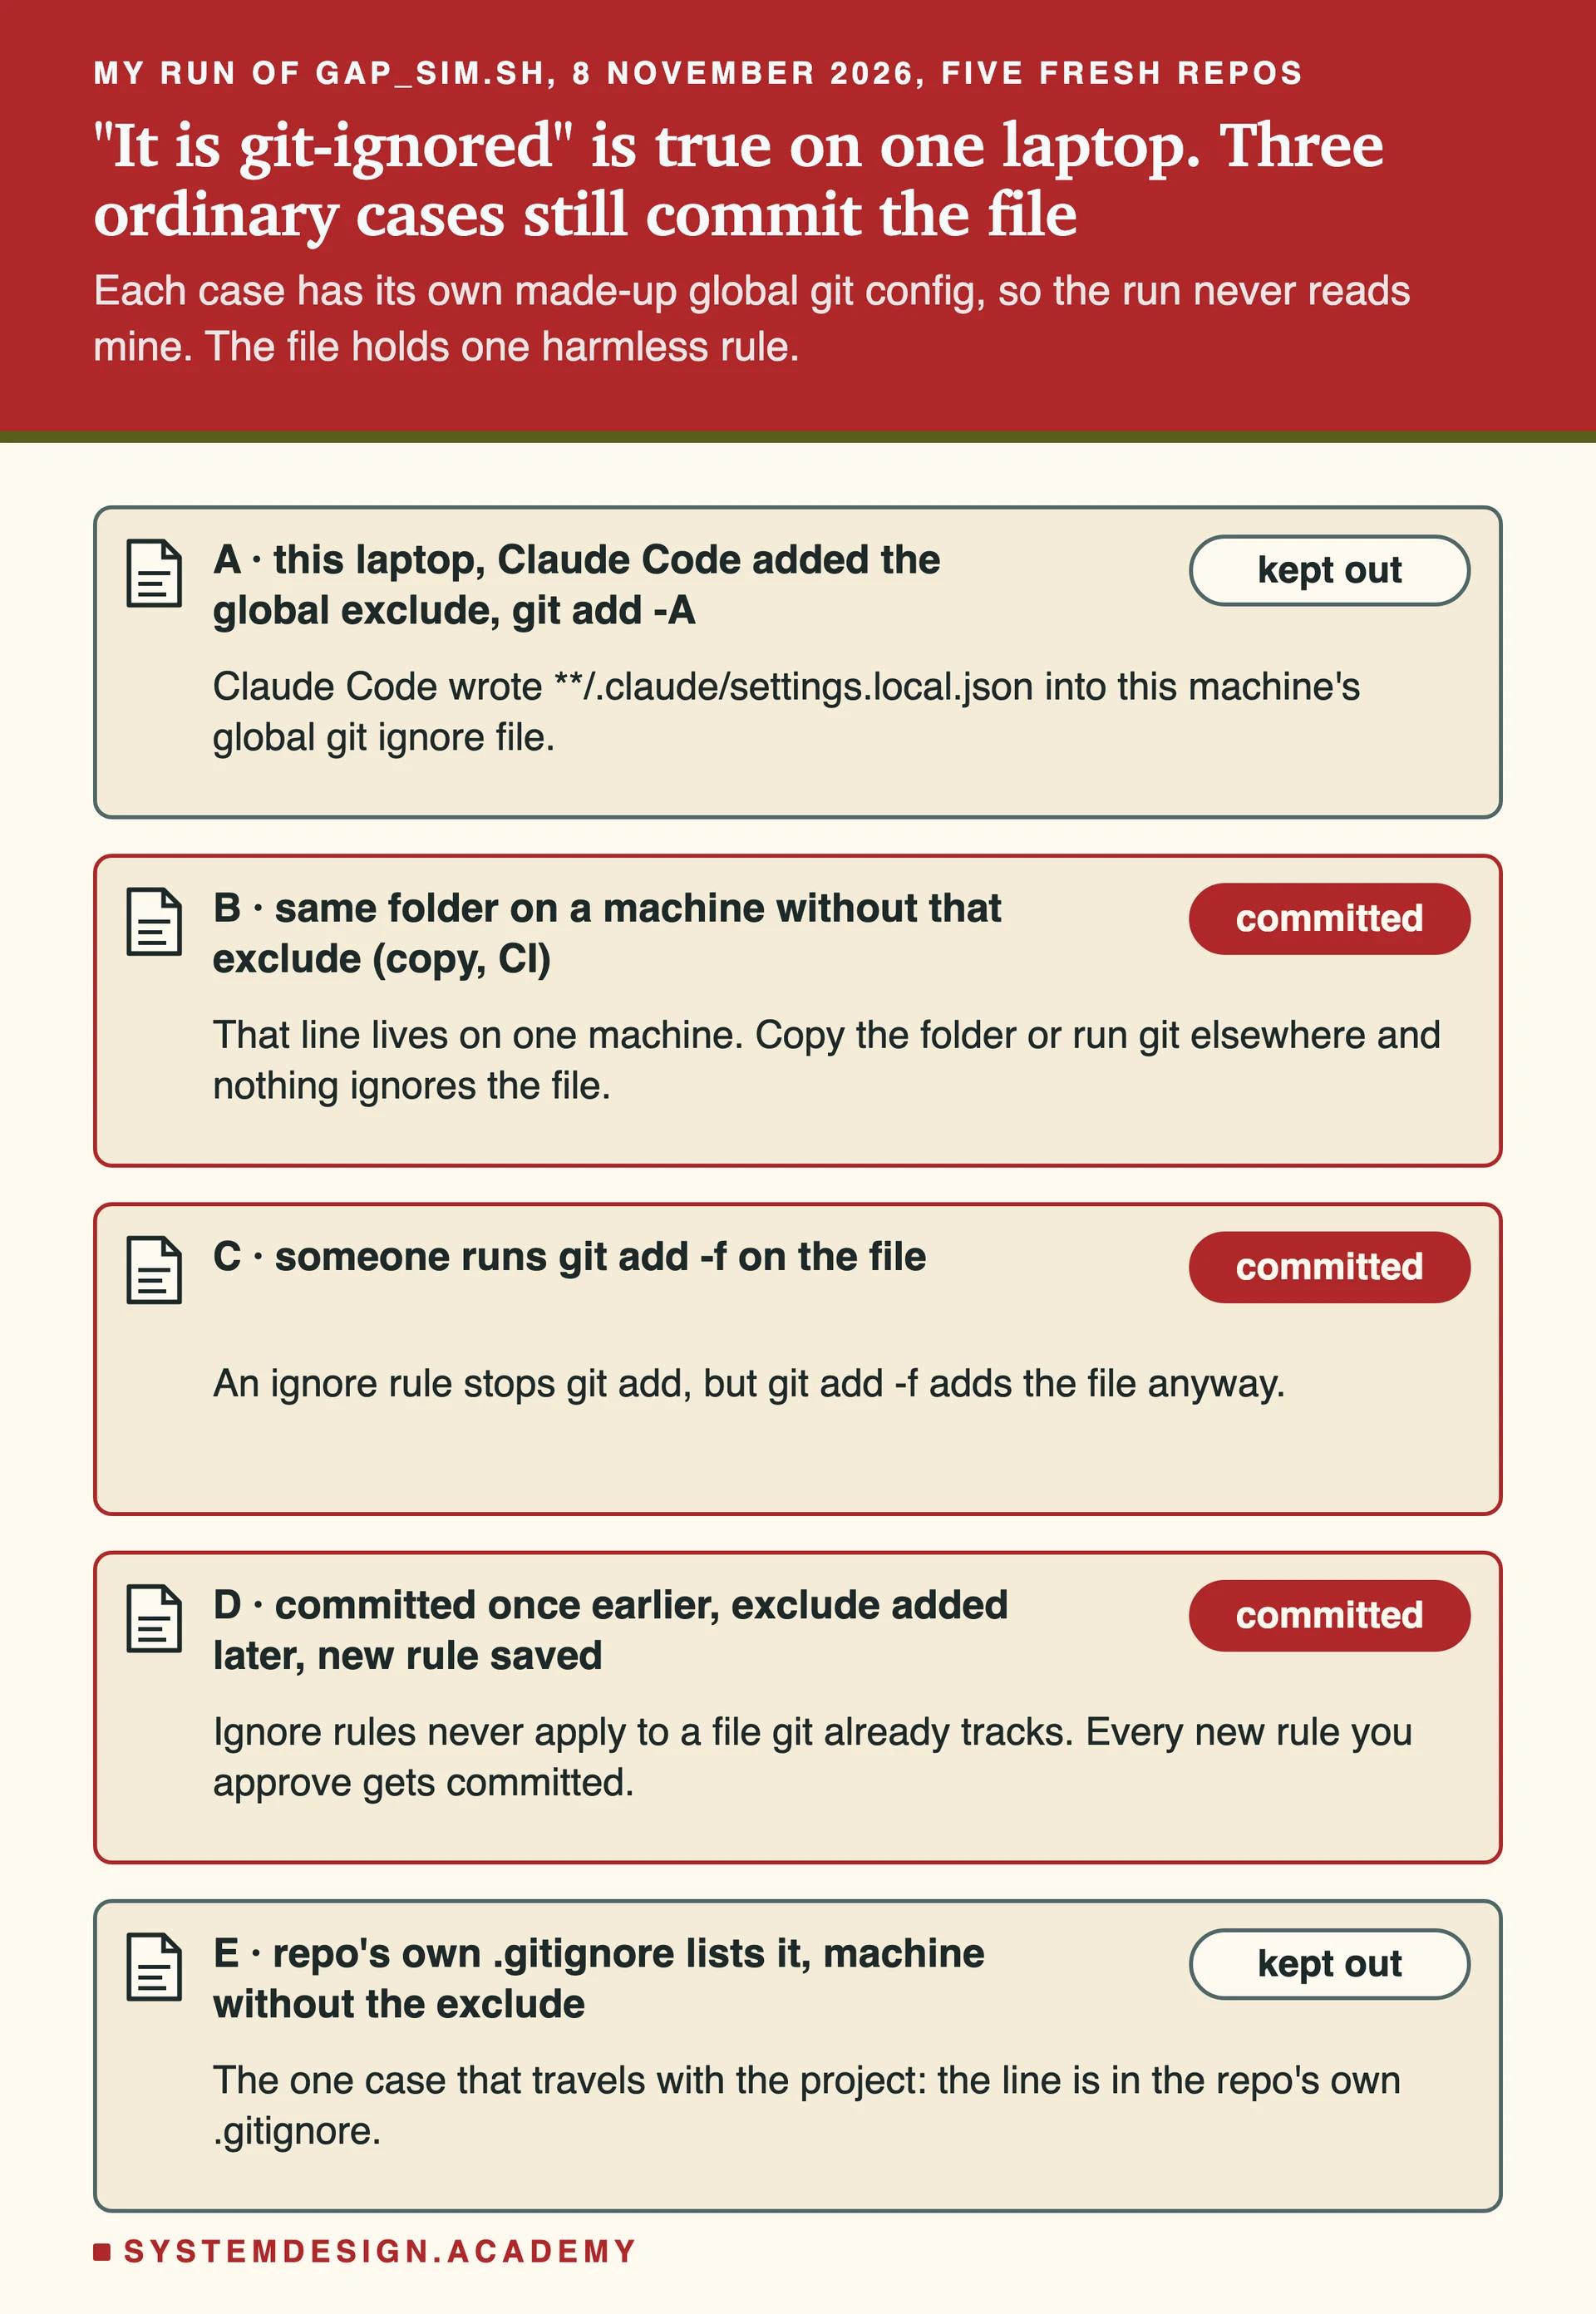
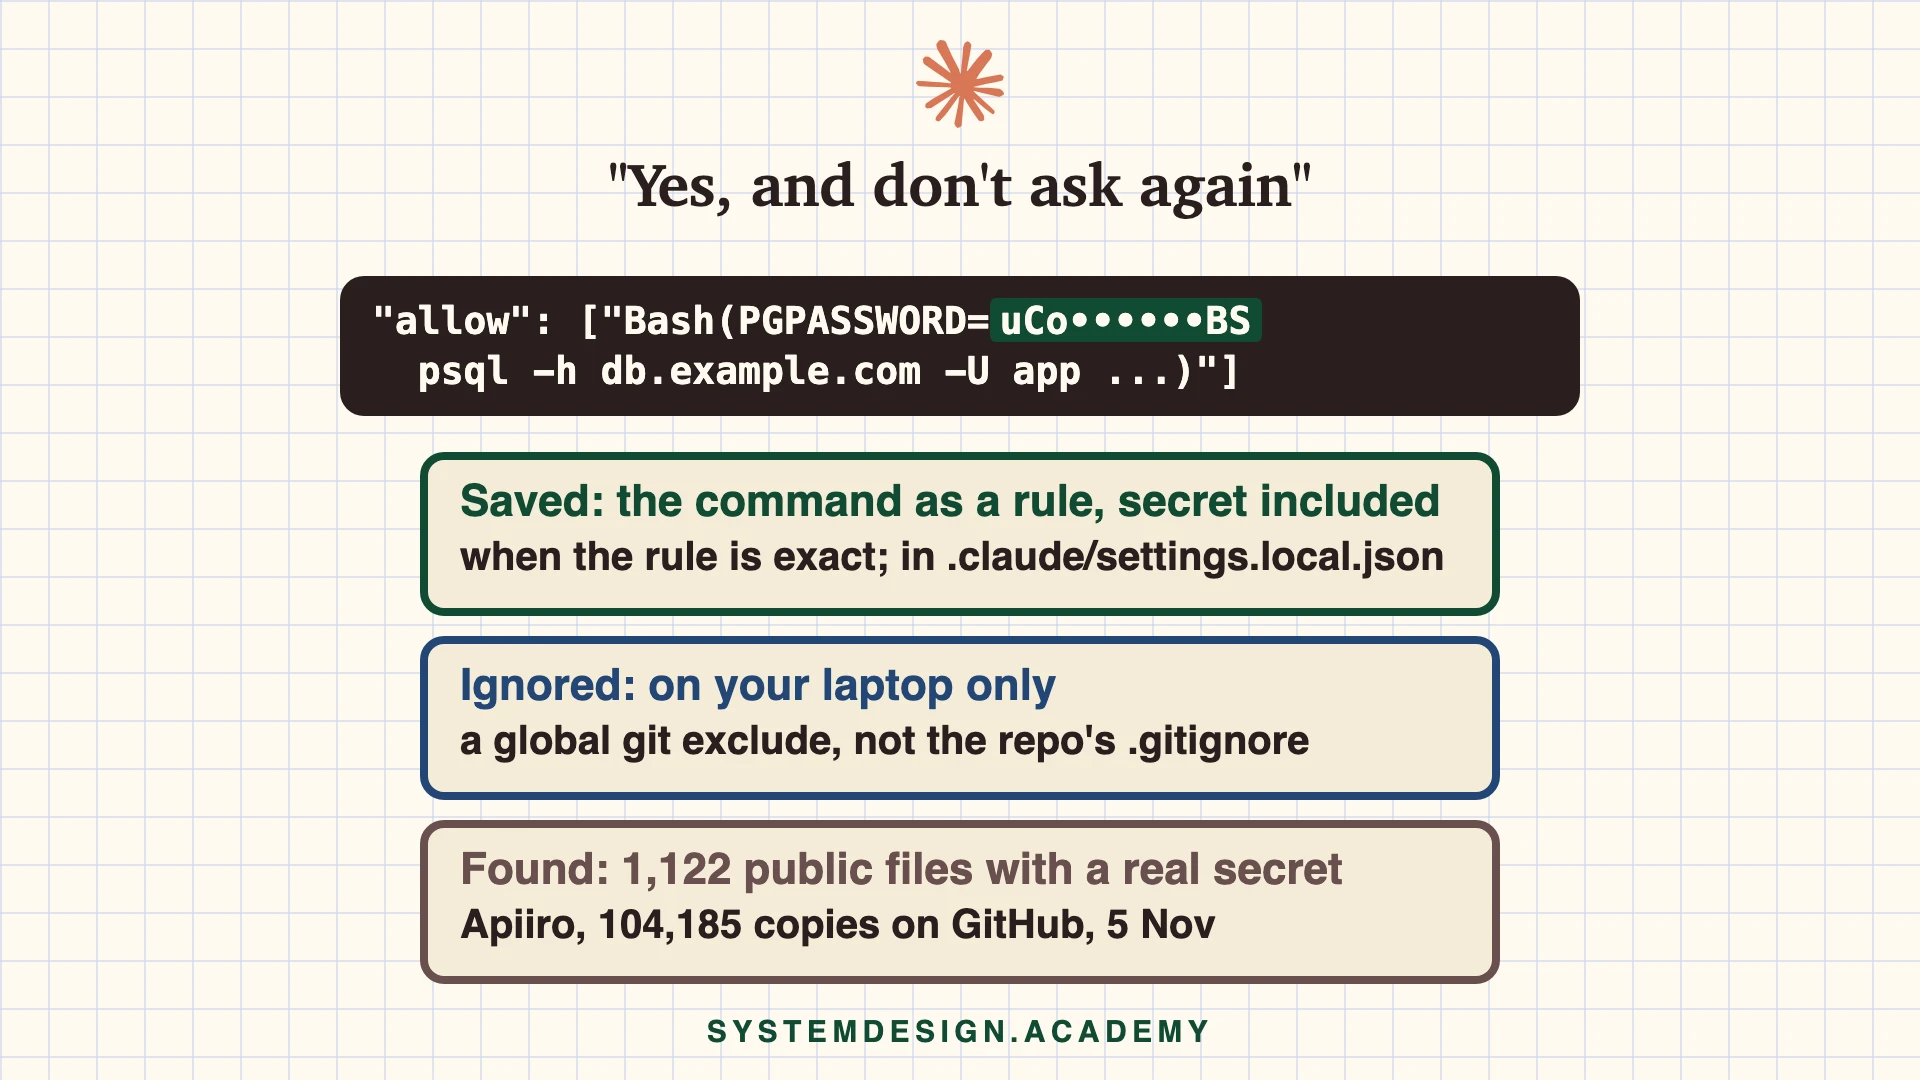
The finding is simple. Claude Code asks before it runs a shell command. One of the answers is "Yes, and don't ask again". Pick it, and Claude Code saves a permission rule so it will not ask about that command again. The rule goes into .claude/settings.local.json, a JSON file inside your project folder. When the rule is the full command, it holds whatever was in the command, and a command that talks to a database or a server often has the password in it.
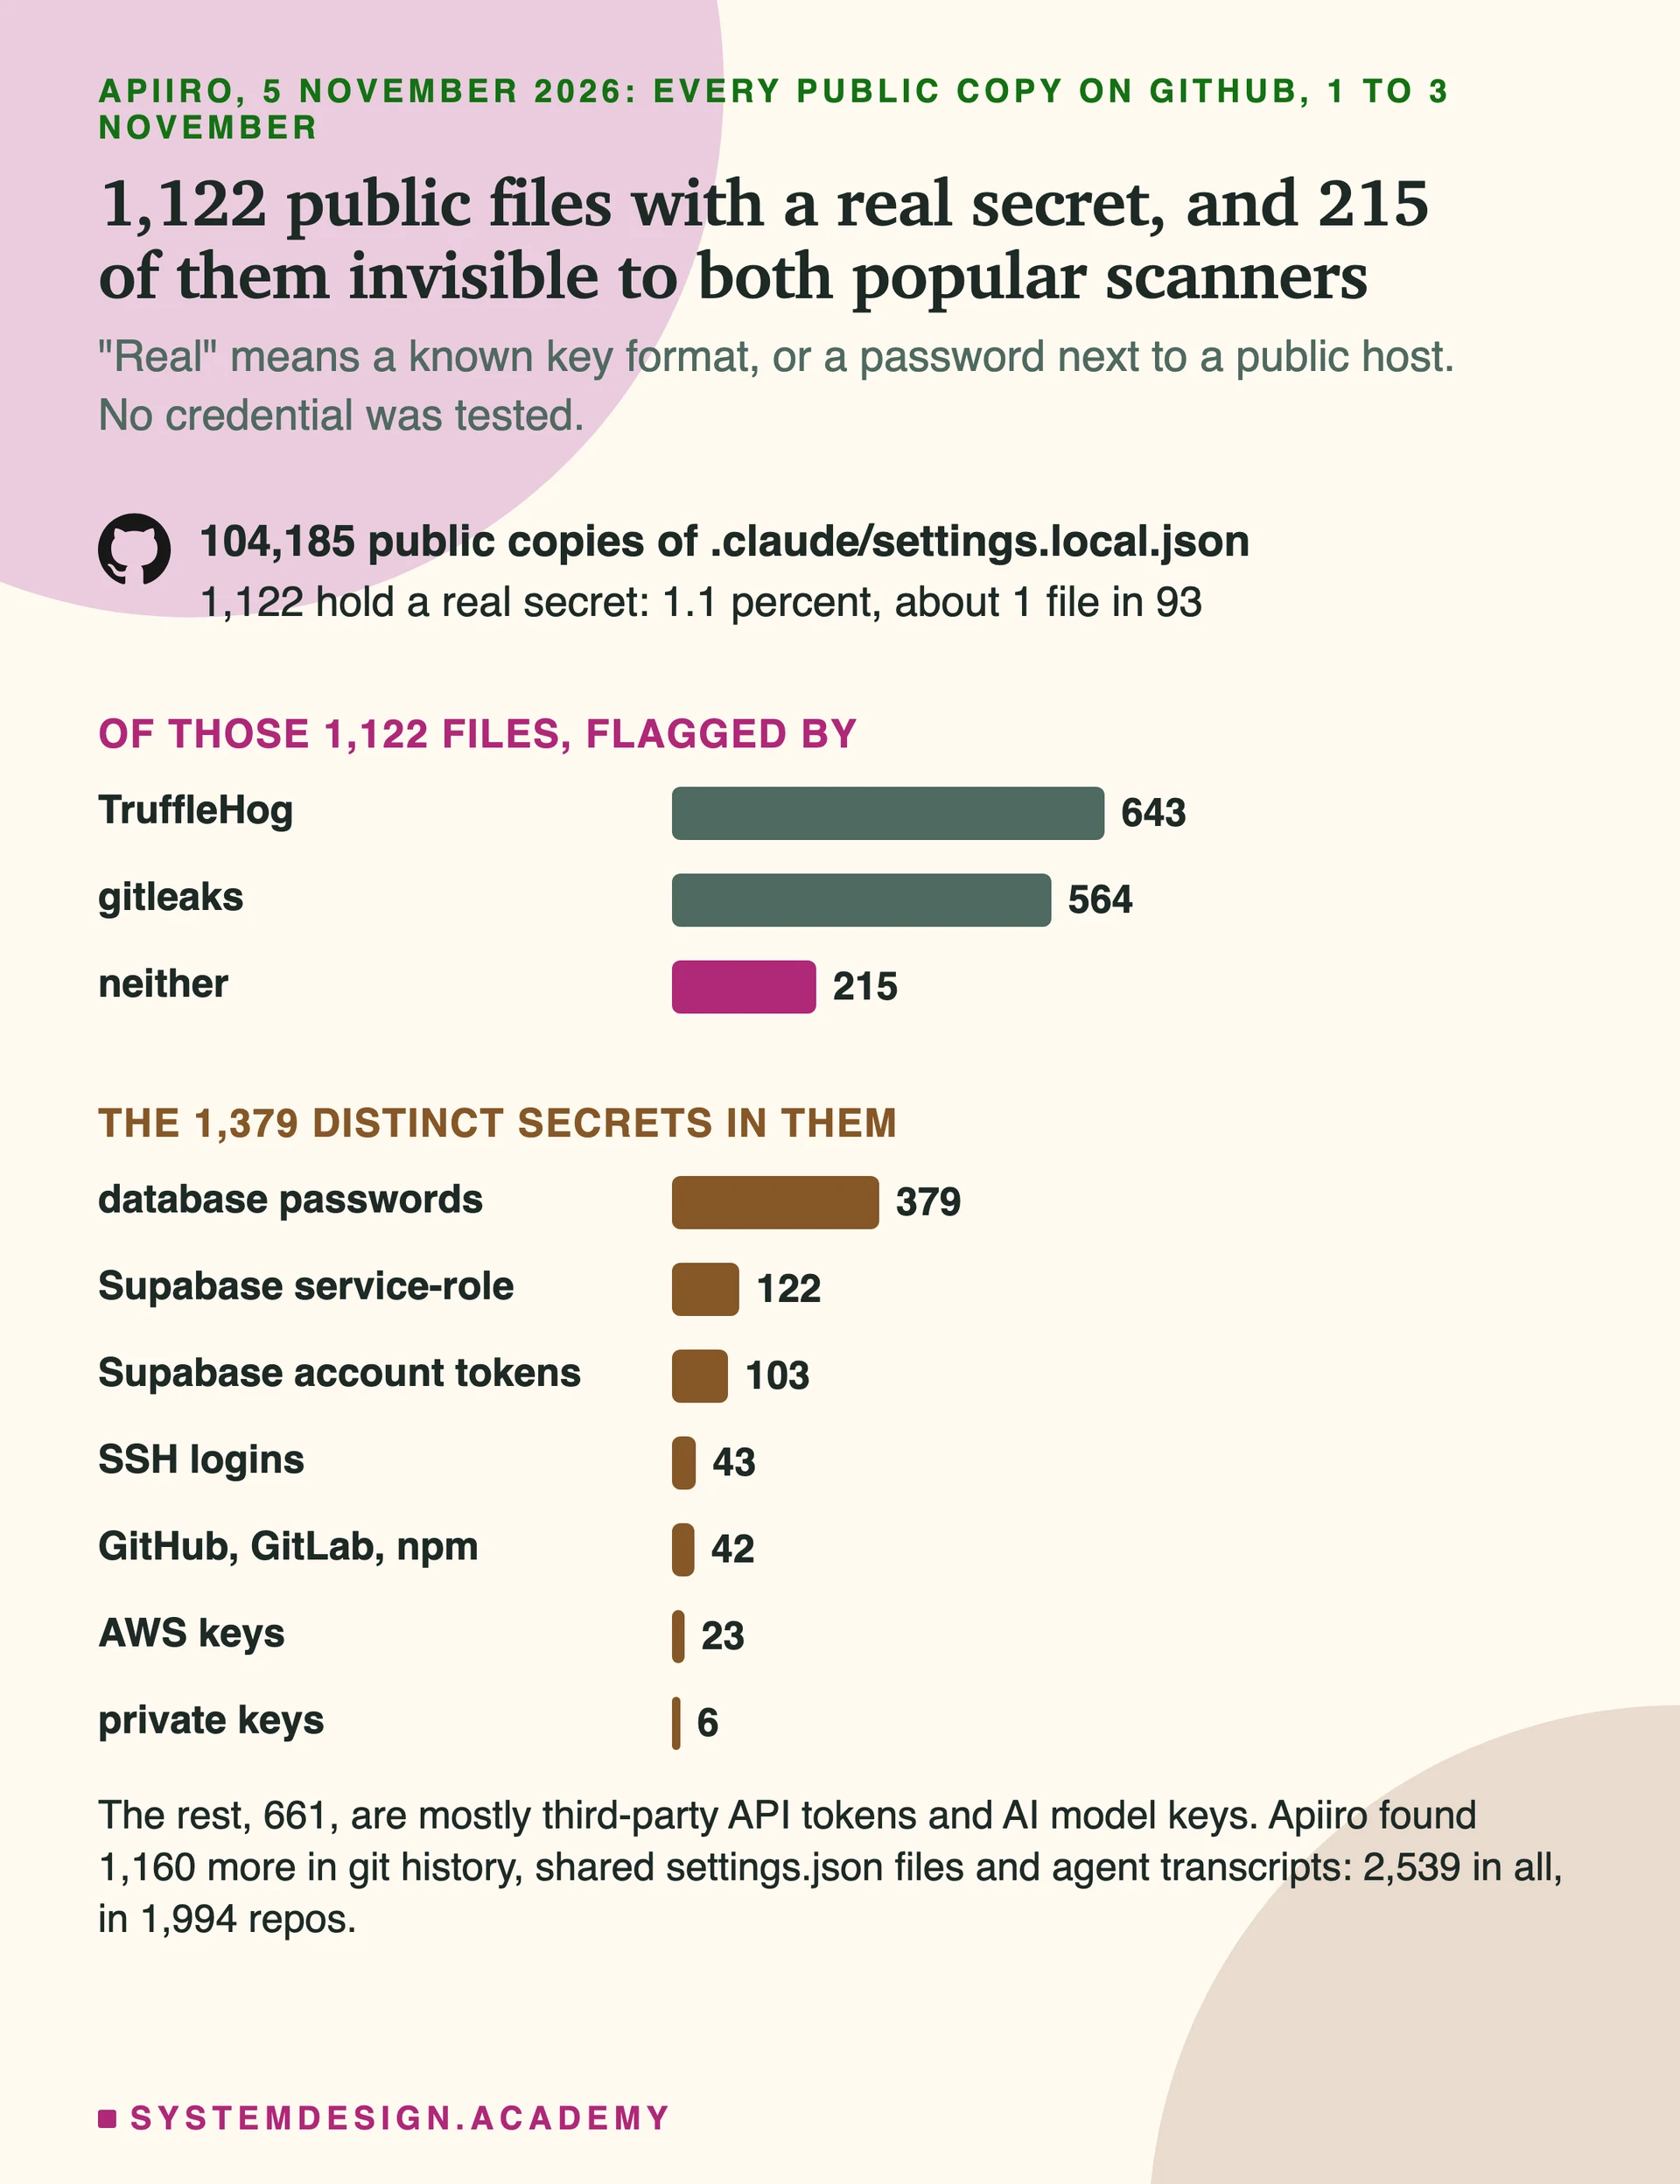
Apiiro counted every public copy of that file on GitHub and checked each for secrets. Among the cases they confirmed: a database vendor's own cloud API key, a production Azure Postgres password, a Square production token, and the owner password of a medical-records app's database. They reported each case to its owner on 2 and 3 November, and one company confirmed its key had been live.