
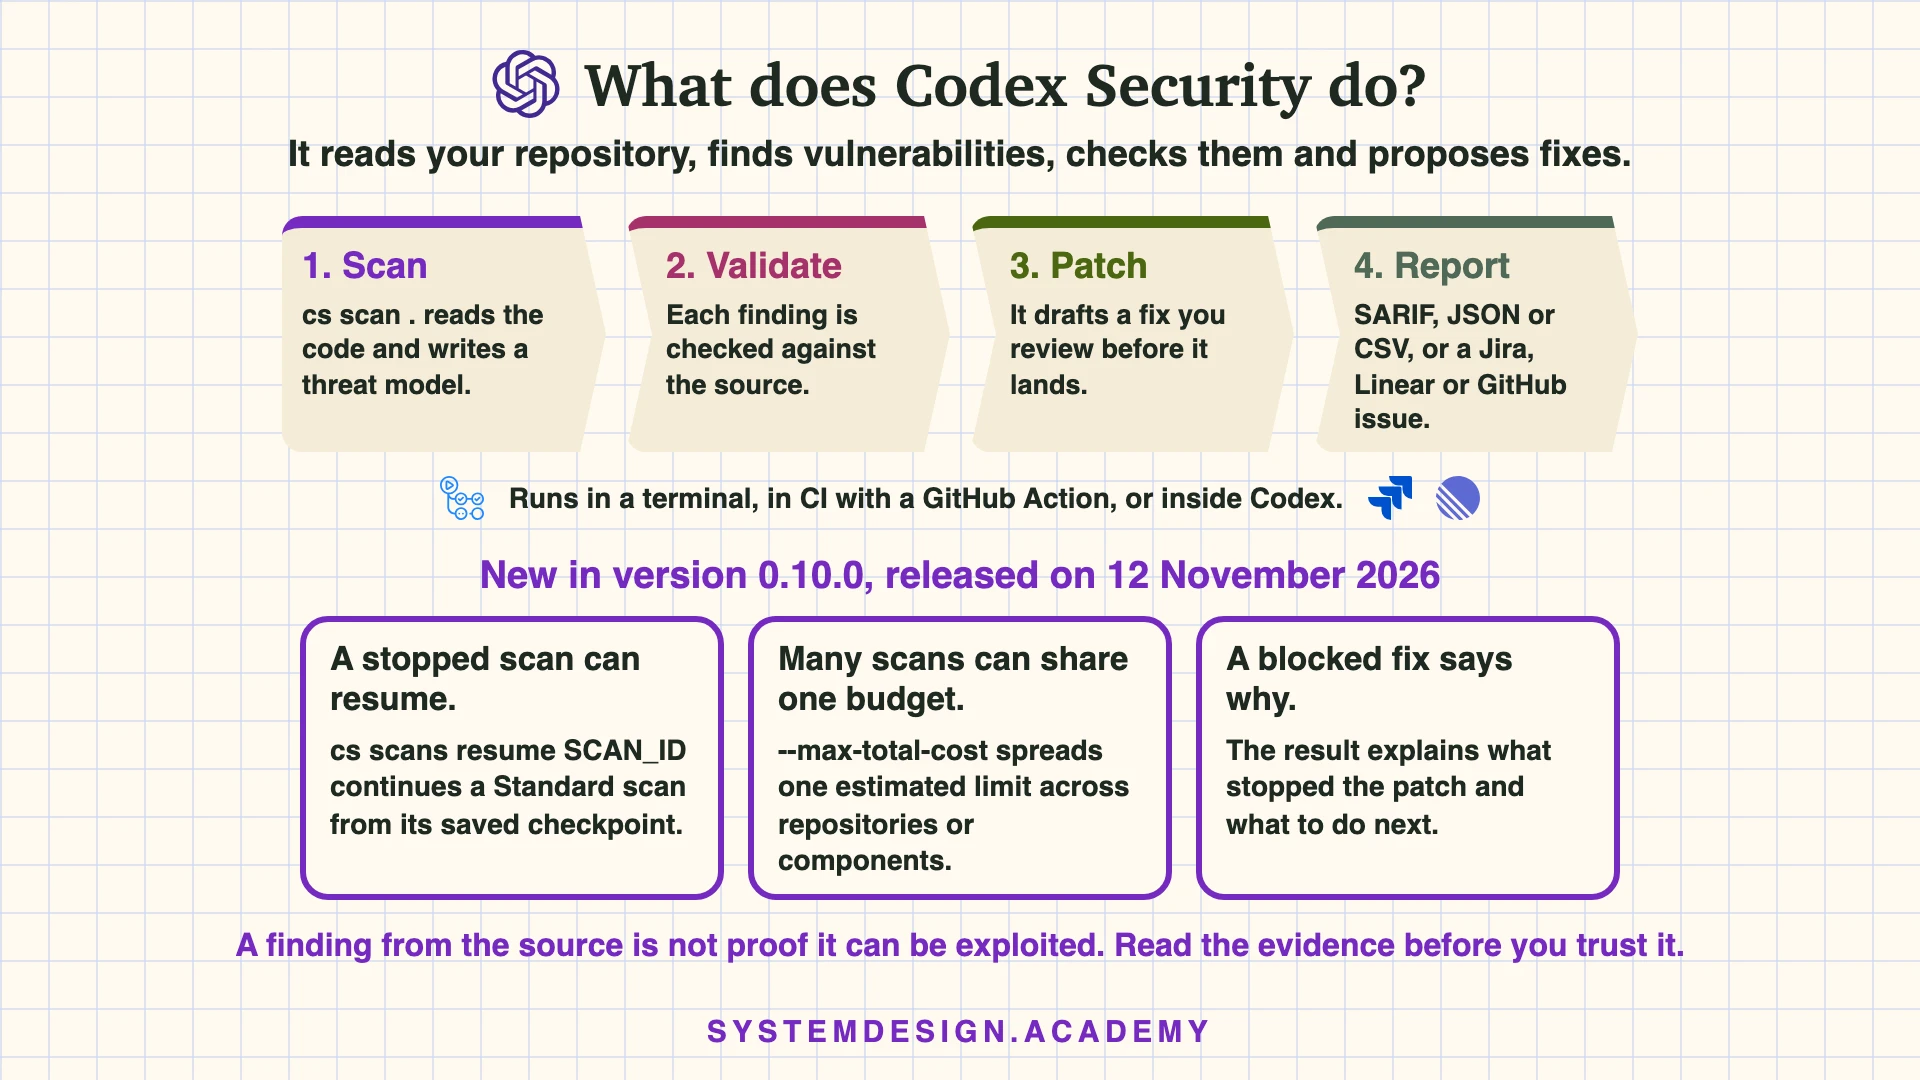
What is OpenAI Codex Security?
“Codex Security helps you find, investigate, and fix vulnerabilities in your code.”
Codex Security is a tool from OpenAI that looks for security vulnerabilities in your code, checks whether each one is real, and helps you fix it. You can use it three ways: inside Codex, where you ask for a security scan in plain English; in a terminal, with the cs command from the @openai/codex-security npm package; or in automation, through the TypeScript SDK or a GitHub Action.
The source is on GitHub under the Apache 2.0 licence. The first npm release, 0.1.0, came out on 31 July 2026, and the latest, 0.10.0, on 12 November 2026, the morning the repository was on GitHub's trending list.
It is built on Codex, OpenAI's coding agent, so a scan is an agent doing the work a security reviewer does: reading the code, forming a theory of what an attacker could reach, and checking it, rather than matching a fixed list of patterns.
